


EN 18286:2026
(Main)Artificial intelligence - Quality management system for EU AI Act regulatory purposes
General Information
- Abstract
This document specifies the requirements and provides guidance for the definition, implementation and maintenance of a quality management system for organizations that provide AI systems.
This document is intended to support the organization in meeting applicable regulatory requirements. It is primarily intended for organizations placing on the market or putting into service high-risk AI systems and is not specific to any particular sector.
- Status
- Published
- Publication Date
- 21-Jul-2026
- Technical Committee
- CEN/CLC/JTC 21 - Artificial Intelligence
- Drafting Committee
- CEN/CLC/JTC 21/WG 2 - Operational aspects
- Current Stage
- 6060 - Definitive text made available (DAV) - Publishing
- Start Date
- 22-Jul-2026
- Due Date
- 27-Jan-2027
- Completion Date
- 22-Jul-2026
- Directive
- Not Harmonized2024/1689 - EU AI Act
Overview
EN 18286:2026 is a European standard developed by CEN, focusing on the establishment and upkeep of a quality management system (QMS) for organizations providing artificial intelligence (AI) systems, specifically aligned with the EU AI Act. This standard offers essential requirements and detailed guidance to help organizations define, implement, maintain, and improve a QMS that supports regulatory compliance for high-risk AI systems within the European Union.
The primary purpose of EN 18286:2026 is to ensure that AI providers can consistently meet the legal and regulatory obligations set forth by the EU AI Act. This standard is sector-neutral and designed for any organization-regardless of size, type, or location-engaged in the development, commercialization, or deployment of AI systems in the EU market.
Key Topics
EN 18286:2026 specifies comprehensive elements for an AI-centric quality management system:
- Regulatory Compliance: Outlines processes for identifying and incorporating EU AI Act requirements, supporting organizations in conforming to relevant European legislation.
- Management Responsibility: Defines leadership roles, responsibilities, and authorities to manage quality and regulatory compliance.
- Life Cycle Management: Details the necessary procedures for controlling AI system development, deployment, monitoring, and retirement.
- Risk Management: Provides guidelines for identifying, analyzing, mitigating, and monitoring risks related to health, safety, and fundamental rights, as imposed by the AI Act.
- Product Realization: Describes the management of the AI system’s inception, design, verification, validation, data management, and documentation.
- Support Processes: Covers competence requirements, resource management, internal communication, and continuous improvement.
- Operation and Post-Market Monitoring: Establishes procedures for deploying AI systems, addressing supply chain issues, managing modifications, reporting incidents, and conducting nonconformity management.
- Performance Evaluation: Requires performance measurements, internal reviews, corrective actions, and ongoing improvement activities.
- Consultation on Fundamental Rights: Recommends stakeholder engagement to ensure respect for human rights throughout the AI system’s life cycle.
Applications
Organizations placing high-risk AI systems on the EU market or putting them into service-such as in medical devices, industrial automation, financial services, or security solutions-benefit from EN 18286:2026 by:
- Achieving Regulatory Readiness: Demonstrates structured and auditable compliance with the EU AI Act and related regulations.
- Mitigating Compliance Risks: Implements systematic approaches to identify and manage potential legal and ethical risks posed by AI.
- Enhancing Trust and Accountability: Provides transparency, documentation, and traceability for AI system development and deployment, thereby fostering trust among stakeholders and regulators.
- Supporting Existing Management Systems: Integrates seamlessly with other management standards (e.g., ISO 9001, ISO/IEC 42001), enabling organizations to holistically manage regulatory and quality requirements.
- Facilitating Market Access: Satisfies preconditions for access to the EU market by offering evidence of conformity to essential requirements for high-risk AI systems.
Related Standards
Organizations utilizing EN 18286:2026 may also refer to:
- ISO 9001:2015 - Quality Management Systems: Provides generic principles for quality management, which EN 18286:2026 aligns with and adapts for AI regulatory compliance.
- ISO/IEC 42001:2023 - AI Management Systems: Specifies requirements for establishing, implementing, maintaining, and continually improving an AI management system, providing a framework complementary to EN 18286:2026.
- prEN 18228 – AI Risk Management: Focuses on risk management for AI systems and is referenced for terminology and risk assessment procedures.
- Regulation (EU) 2024/1689 – EU AI Act: The core legislative framework defining the requirements for high-risk AI systems.
EN 18286:2026 is essential for any organization looking to navigate the increasingly regulated EU AI landscape with a robust, auditable, and future-proof quality management system.
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.

Bureau Veritas
Bureau Veritas is a world leader in laboratory testing, inspection and certification services.
DNV
DNV is an independent assurance and risk management provider.
Sponsored listings
Frequently Asked Questions
EN 18286:2026 is a standard published by the European Committee for Standardization (CEN). Its full title is "Artificial intelligence - Quality management system for EU AI Act regulatory purposes". This standard covers: This document specifies the requirements and provides guidance for the definition, implementation and maintenance of a quality management system for organizations that provide AI systems. This document is intended to support the organization in meeting applicable regulatory requirements. It is primarily intended for organizations placing on the market or putting into service high-risk AI systems and is not specific to any particular sector.
This document specifies the requirements and provides guidance for the definition, implementation and maintenance of a quality management system for organizations that provide AI systems. This document is intended to support the organization in meeting applicable regulatory requirements. It is primarily intended for organizations placing on the market or putting into service high-risk AI systems and is not specific to any particular sector.
EN 18286:2026 is classified under the following ICS (International Classification for Standards) categories: 03.100.70 - Management systems; 35.240.01 - Application of information technology in general. The ICS classification helps identify the subject area and facilitates finding related standards.
EN 18286:2026 is associated with the following European legislation: EU Directives/Regulations: 2024/1689; Standardization Mandates: M/593, M/613. When a standard is cited in the Official Journal of the European Union, products manufactured in conformity with it benefit from a presumption of conformity with the essential requirements of the corresponding EU directive or regulation.
EN 18286:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
SLOVENSKI STANDARD
01-oktober-2026
Umetna inteligenca - Sistem vodenja kakovosti za namene regulativnih zahtev
Akta EU o UI
Artificial intelligence - Quality management system for EU AI Act regulatory purposes
Künstliche Intelligenz - Qualitätsmanagementsystem für EU-AI-Act-Regulierungszwecke
Intelligence artificielle - Système de management de la qualité pour le règlement
européen sur l'IA
Ta slovenski standard je istoveten z: EN 18286:2026
ICS:
03.100.70 Sistemi vodenja Management systems
03.120.10 Vodenje in zagotavljanje Quality management and
kakovosti quality assurance
35.240.01 Uporabniške rešitve Application of information
informacijske tehnike in technology in general
tehnologije na splošno
2003-01.Slovenski inštitut za standardizacijo. Razmnoževanje celote ali delov tega standarda ni dovoljeno.
EUROPEAN STANDARD EN 18286
NORME EUROPÉENNE
EUROPÄISCHE NORM
July 2026
ICS 35.240.01
English version
Artificial intelligence - Quality management system for EU
AI Act regulatory purposes
Intelligence artificielle - Système de management de la Künstliche Intelligenz - Qualitätsmanagementsystem
qualité pour le règlement européen sur l'IA für EU-AI-Act-Regulierungszwecke
This European Standard was approved by CEN on 12 July 2026.
CEN and CENELEC members are bound to comply with the CEN/CENELEC Internal Regulations which stipulate the conditions for
giving this European Standard the status of a national standard without any alteration. Up-to-date lists and bibliographical
references concerning such national standards may be obtained on application to the CEN-CENELEC Management Centre or to
any CEN and CENELEC member.
This European Standard exists in three official versions (English, French, German). A version in any other language made by
translation under the responsibility of a CEN and CENELEC member into its own language and notified to the CEN-CENELEC
Management Centre has the same status as the official versions.
CEN and CENELEC members are the national standards bodies and national electrotechnical committees of Austria, Belgium,
Bulgaria, Croatia, Cyprus, Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Iceland, Ireland, Italy,
Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Republic of North Macedonia, Romania, Serbia,
Slovakia, Slovenia, Spain, Sweden, Switzerland, Türkiye and United Kingdom.
CEN-CENELEC Management Centre:
Rue de la Science 23, B-1040 Brussels
© 2026 CEN/CENELEC All rights of exploitation in any form and by any means
Ref. No. EN 18286:2026 E
reserved worldwide for CEN national Members and for
CENELEC Members.
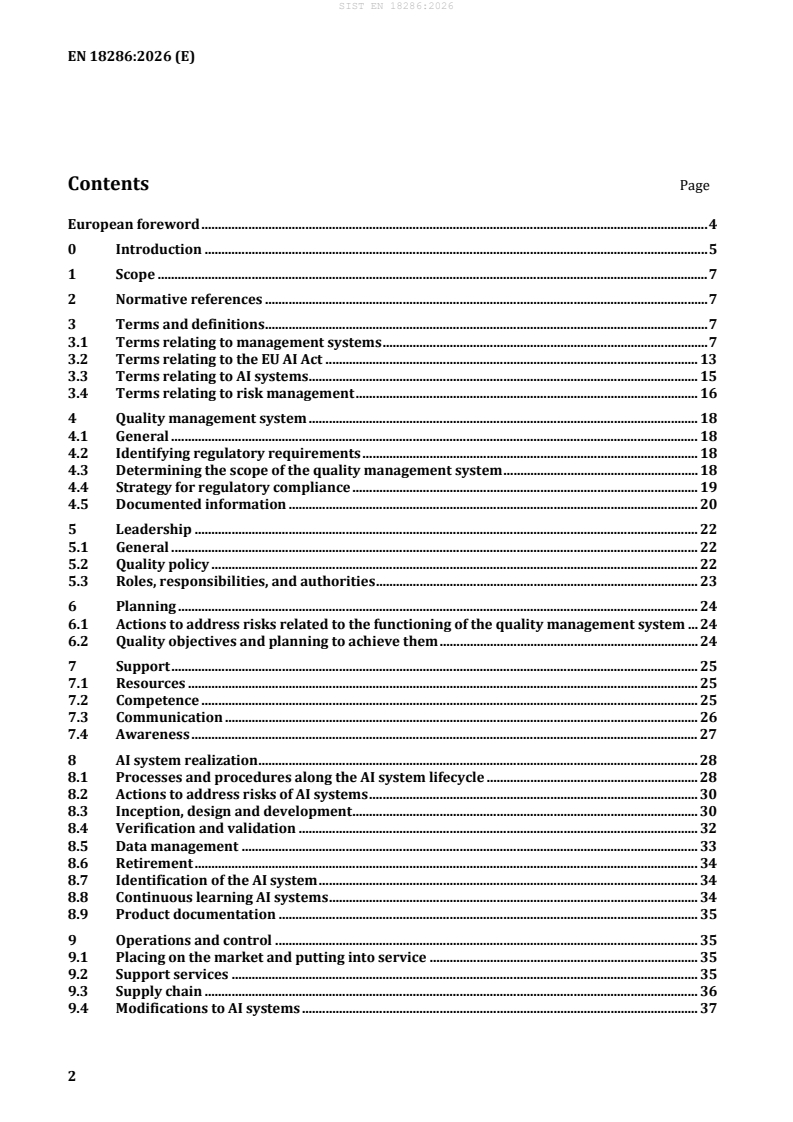
Contents Page
European foreword . 4
0 Introduction . 5
1 Scope . 7
2 Normative references . 7
3 Terms and definitions . 7
3.1 Terms relating to management systems . 7
3.2 Terms relating to the EU AI Act . 13
3.3 Terms relating to AI systems . 15
3.4 Terms relating to risk management . 16
4 Quality management system . 18
4.1 General . 18
4.2 Identifying regulatory requirements . 18
4.3 Determining the scope of the quality management system . 18
4.4 Strategy for regulatory compliance . 19
4.5 Documented information . 20
5 Leadership . 22
5.1 General . 22
5.2 Quality policy . 22
5.3 Roles, responsibilities, and authorities . 23
6 Planning . 24
6.1 Actions to address risks related to the functioning of the quality management system . 24
6.2 Quality objectives and planning to achieve them . 24
7 Support . 25
7.1 Resources . 25
7.2 Competence . 25
7.3 Communication . 26
7.4 Awareness . 27
8 AI system realization . 28
8.1 Processes and procedures along the AI system lifecycle . 28
8.2 Actions to address risks of AI systems . 30
8.3 Inception, design and development . 30
8.4 Verification and validation . 32
8.5 Data management . 33
8.6 Retirement . 34
8.7 Identification of the AI system . 34
8.8 Continuous learning AI systems . 34
8.9 Product documentation . 35
9 Operations and control . 35
9.1 Placing on the market and putting into service . 35
9.2 Support services . 35
9.3 Supply chain . 36
9.4 Modifications to AI systems . 37
9.5 Post-market monitoring . 37
9.6 Reporting serious incidents . 39
9.7 Non-compliance . 40
10 Performance evaluation . 41
10.1 Management review . 41
10.2 Planning of changes . 43
Annex A (informative) Understanding the needs and expectations of interested parties
regarding health, safety and fundamental rights . 45
Annex B (informative) Correspondence between this document and EN ISO 9001:2015 . 46
Annex C (informative) Correspondence between this document and EN ISO/IEC 42001:2026 . 47
Annex ZA (informative) Relationship between this European Standard and the requirements
of Regulation (EU) 2024/1689 aimed to be covered . 48
Bibliography . 50
European foreword
This document (EN 18286:2026) has been prepared by the Joint Technical Committee CEN/CLC/JTC 21
“Artificial Intelligence”, the secretariat of which is held by DS.
This European Standard shall be given the status of a national standard, either by publication of an identical
text or by endorsement, at the latest by January 2027 and conflicting national standards shall be withdrawn
at the latest by January 2027.
Attention is drawn to the possibility that some of the elements of this document may be the subject
of patent rights. CEN-CENELEC shall not be held responsible for identifying any or all such patent rights.
This document has been prepared under a standardization request addressed to CEN-CENELEC by
the European Commission. The Standing Committee of the EFTA States subsequently approves these
requests for its Member States.
For the relationship with EU Legislation, see informative Annex ZA, which is an integral part of this
document.
Any feedback and questions on this document should be directed to the users’ national standards body.
A complete listing of these bodies can be found on the CEN-CENELEC website.
According to the CEN-CENELEC Internal Regulations, the national standards organizations of the following
countries are bound to implement this European Standard: Austria, Belgium, Bulgaria, Croatia, Cyprus,
Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Iceland, Ireland, Italy,
Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Republic of North
Macedonia, Romania, Serbia, Slovakia, Slovenia, Spain, Sweden, Switzerland, Türkiye and the United
Kingdom.
0 Introduction
0.1 General
The EU’s Artificial Intelligence Act (EU AI Act) [1] regulates AI systems through the product safety system
established under the New Legislative Framework. An AI system that is classified as high-risk and must
comply with the relevant EU AI Act obligations can be a product or a component of a product.
NOTE 1 Classification rules for high-risk AI systems can be found in the EU AI Act, Article 6.
AI systems must be in compliance with applicable regulatory requirements at the moment that the AI system
is placed on the market or put into service. An AI system is placed on the market when it is supplied for first
distribution or use on the Union market in the course of a commercial activity, whether in return for
payment or free of charge. An AI system is put into service when it is supplied for the first use directly to
the deployer or for own use in the Union for its intended purpose.
EXAMPLE 1 An in-house developed AI system is put into service when it is used internally.
EXAMPLE 2 An AI system is placed on the market when it is offered for sale on a website.
The quality management system defined in this document can be used by a provider for one or more AI
systems that are intended to be placed on the market or put into service. Quality, in this context can be
understood as compliance with all of the regulatory requirements of the EU AI Act.
Depending on the intended purpose of the AI system, sector-specific regulations including obligations for a
quality management system, can apply. The provider can extend a quality management system following a
sector-specific regulation in such a way that it fulfils the requirements of the EU AI Act regulation instead
of using a separate quality management system.
EXAMPLE 3 Medical devices are commonly compliant to EN ISO 13485 [2] quality management system
requirements. Incorporating the requirements of this document within the existing processes is desirable when
achieving compliance with this document.
This document is intended for use by providers that provide AI systems irrespective of size, nature or
location. The requirements and guidance in this document are, however, specifically tailored to support
providers that operate inside of the European Union, and those located outside of the Union who are active
in the European Union market or who intend to enter that market.
The requirements in this document are the practical implementation from specific requirements from the
EU AI Act (see Annex ZA) by relying on state of the art practices from other widely used standards where
possible (see informative references throughout this document).
The quality management system in this document is described in a way that the implementation can take
into account the size of the provider, while providing the degree of rigour and level of protection required
by applicable regulatory requirements.
Clause 1 defines the scope of applicability of this document, while Clause 2 identifies normative references
essential for its application, although there are none in this document.
Clause 3 establishes the terms and definitions used throughout this document, including terminology
related to management systems, the EU AI Act, AI systems, and risk management, to ensure consistent
interpretation. References to how most of these concepts are based on other standards are also provided
in Clause 3.
Clause 4 specifies the requirements for establishing, implementing and maintaining the quality
management system, including the identification of regulatory requirements, determination of scope,
strategy for regulatory compliance, and control of documented information. After reading the Introduction
and Clause 1, this is a good place to start for readers new to management system standards.
Clause 5 addresses management responsibility, defining leadership commitment, quality policy, and the
assignment of roles, responsibilities, and authorities.
Clause 6 focuses on planning, including actions to address risks to the quality management system and the
setting and achievement of quality objectives.
Clause 7 describes the support processes required for the effective operation of the management system,
covering resources, competence, communication and awareness.
Clause 8 addresses AI system realization, detailing requirements across the AI system lifecycle, not least the
“design and development” and “verification and validation” phases as well as requirements regarding data
management, retirement, identification of the AI system and product documentation. Clause 8 also contains
a subclause on continuous learning AI systems and their predetermined changes.
Clause 9 covers operations and control, during deployment, including monitoring, supply chain
management, change control, post-market monitoring, incident reporting, and handling of non-compliance.
Finally, Clause 10 specifies requirements for performance evaluation of the management system, including
reviews and planning of changes to ensure ongoing effectiveness and compliance.
Annex A describes procedures for consultation with interested parties about risks to health, safety and
fundamental rights, Annex B contains the correspondence between the clauses of this document and
EN ISO 9001:2015 [3], and Annex C contains the correspondence with EN ISO/IEC 42001:2026 [4].
NOTE 2 Italicised terms are defined in Clause 3.
0.2 Verbal forms
In this document, the following verbal forms are used:
— “shall” indicates a requirement;
— “should” indicates a recommendation;
— “may” indicates a permission;
— “can” indicates a possibility or a capability.
0.3 Fundamental rights
The EU AI Act aims to ensure the protection of health, safety and fundamental rights in relation to AI systems
and this document sets out technical requirements to achieve this regulatory objective through a quality
management system.
Fundamental rights are universal legal guarantees without which individuals and groups cannot secure
their fundamental freedoms and human dignity and which apply equally to every human being regardless
of nationality, place of residence, sex, national or ethnic origin, colour, religion, language or any other status
as per the legal system of a country without any conditions.
The EU Charter of Fundamental Rights [5] sets out and codifies the European approach to these
fundamental rights in law which is applicable throughout the EU.
NOTE Further information about their scope and strength can be found in the Charter. Additional EU and
country-specific regulatory requirements can apply.
1 Scope
This document specifies the requirements and provides guidance for the definition, implementation and
maintenance of a quality management system for organizations that provide AI systems.
This document is intended to support the organization in meeting applicable regulatory requirements. It
is primarily intended for organizations placing on the market or putting into service high-risk AI systems
and is not specific to any particular sector.
2 Normative references
There are no normative references in this document.
3 Terms and definitions
For the purposes of this document, the following terms and definitions apply.
ISO and IEC maintain terminology databases for use in standardization at the following addresses:
— ISO Online browsing platform: available at https://www.iso.org/obp/
— IEC Electropedia: available at https://www.electropedia.org/
3.1 Terms relating to management systems
3.1.1
audit
systematic (3.1.30) and independent process (3.1.22) for obtaining evidence and evaluating it objectively
to determine the extent to which the audit criteria are fulfilled
Note 1 to entry: An audit can be an internal audit (first party) or an external audit (second party or third party), and
it can be a combined audit (combining two or more disciplines).
Note 2 to entry: An internal audit is conducted by the organization (3.1.18) itself, or by an external party on its behalf.
Note 3 to entry: “Audit criteria” is defined in EN ISO 19011.
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024),
3.1.18, modified — Removed “audit evidence and” from Note 3.]
3.1.2
authority
authorities
ability of an individual, group or organization (3.1.18) to do something without intervention by another
function on the details of that action
3.1.3
competence
ability to apply knowledge and skills to achieve intended results
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024), 3.9]
3.1.4
compliance
fulfilment of all applicable regulatory requirements (3.1.26)
3.1.5
control
measure that is modifying risk (3.4.5)
Note 1 to entry: Controls include any process (3.1.22), policy, device, practice, or other actions which modify
risk (3.4.5).
Note 2 to entry: It is possible that controls not always exert the intended or assumed modifying effect.
[SOURCE:ISO Guide 73:2009, 3.8.1.1, modified — Note 2 to entry has been changed.]
3.1.6
corrective action
action to eliminate the cause(s) of a non-compliance (3.1.15) and to prevent recurrence
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024),
3.17, modified — Changed “nonconformity” to “non-compliance”.]
3.1.7
documented information
information controlled and maintained by an organization (3.1.18) and the medium on which it is
contained
Note 1 to entry: Documented information can be in any format and media and from any source.
Note 2 to entry: Documented information can refer to:
a) the management system, including related processes (3.1.22);
b) information created in order for the organization (3.1.18) to operate (documented information);
c) evidence of compliance (3.1.4) and results achieved.
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024),
3.10, modified — Removed “required to be” from the definition, in Note 2 b) referenced documented
information instead of documentation, in Note 2 c) added “compliance and” and removed reference to
records.]
3.1.8
effectiveness
extent to which planned activities are realized and planned results are achieved
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024),
3.13]
3.1.9
essential requirement
definition of the results to be attained, or the hazards (3.4.4) to be dealt with, without specifying the
technical solutions for doing so
Note 1 to entry: Essential requirements in relation to the EU AI Act [1] are specified in Chapter III, Section 2 of that
Regulation.
Note 2 to entry: Essential requirements are a subset of regulatory requirements (3.1.26).
[SOURCE: The Blue Guide on implementation of EU product rules 2022/C247/01, modified — Changed
“but do not specify” to “without specifying”.]
3.1.10
harmonized standard
European Standard adopted on the basis of a request made by the Commission for the application of Union
harmonization legislation
Note 1 to entry: A European standardization organization can develop a new standard, adopt an existing international
standard or adapt an existing international standard.
[SOURCE: Regulation (EU) 1025/2012, Article 2(1)(c), modified — Removed “a”, added Note 1 to entry.]
3.1.11
interested party
stakeholder
individual, group or organization (3.1.18) that can affect, be affected by or perceive itself to be affected by
a decision or activity
Note 1 to entry: Affected persons (3.4.1) are a subset of interested parties.
Note 2 to entry: Interested parties include relevant regulatory bodies, national public bodies, bodies that enforce the
protection of fundamental rights (3.4.2) and market surveillance authorities.
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024), 3.2,
modified — In the definition, replaced “person” with “individual” and added “group”; added Notes 1 and
2.]
3.1.12
life cycle
evolution of a system, product, service, project or other human-made entity, from inception through
retirement
[SOURCE: ISO/IEC/IEEE 15288:2023, 3.21, modified — Changed “conception” to “inception”.]
3.1.13
measurement
process (3.1.22) to determine a value
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024),
3.19]
3.1.14
monitoring
repeatedly determining the status of a system, a process (3.1.22) or an activity using inputs including
measurements (3.1.13)
Note 1 to entry: To determine the status, there can be a need to check, supervise or critically observe.
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024),
3.20, modified — Added “repeatedly” and “using inputs including measurements” to definition.]
3.1.15
non-compliance
non-fulfilment of applicable regulatory requirements (3.1.26)
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024),
3.16, modified — Replaced “a requirement” with “applicable regulatory requirements”.]
3.1.16
object
object of conformity assessment
entity to which specified requirements (3.1.27) apply
EXAMPLE Product, process, service, system, installation, project, data, design, material, claim, person, body or
organization (3.1.15), or any combination thereof.
[SOURCE: EN ISO/IEC 17000:2020, modified — Switched preferred and admitted terms, removed Note 1.]
3.1.17
objective evidence
data supporting the existence or verity of something
Note 1 to entry: Objective evidence can be obtained through observation, measurement (3.1.13), test, or by other
means.
Note 2 to entry: Objective evidence for the purpose of audit (3.1.1) generally consists of records, statements of fact
or other information which are relevant to the audit criteria and verifiable.
[SOURCE: EN ISO 9000:2015, 3.8.3]
3.1.18
organization
entity consisting of a person or group of people that has its own functions with responsibilities (3.1.33),
authorities (3.1.2) and relationships to achieve its objectives
Note 1 to entry: The concept of organization includes, but is not limited to, sole-trader, company, corporation, firm,
enterprise, authority, partnership, charity or institution, or part or combination thereof, whether incorporated or not,
public or private.
Note 2 to entry: If the organization is part of a larger entity, the term “organization” refers only to the part of the
larger entity that is within the scope of the quality (3.1.23) management system.
[SOURCE: EN ISO 9000:2015, 3.2.1, modified — Added “Entity consisting of a”.]
3.1.19
performance
measurable result
Note 1 to entry: Performance can relate either to quantitative or qualitative findings.
Note 2 to entry: Performance can relate to the management of activities, processes (3.1.22), products, services,
systems or organizations (3.1.18).
[SOURCE: EN ISO 9000:2015, 3.7.8, modified — Removed Note 3.]
3.1.20
policy
intentions and direction of an organization (3.1.18) as formally expressed by its top management (3.1.28)
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024), 3.5]
3.1.21
procedure
specified way to carry out an activity or a process (3.1.22)
Note 1 to entry: Procedures can be documented.
[SOURCE: EN ISO 9000:2015, 3.4.5, modified — Removed “or not” from Note 1.]
3.1.22
process
set of interrelated or interacting activities that uses or transforms inputs to deliver an intended result
Note 1 to entry: Whether the result of a process is called an output, a product or a service depends on the context of
the reference.
Note 2 to entry: Process can achieve an immediate result but can also consist of information-sharing or other
activities.
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024), 3.8,
modified — Added Note 2; replaced “may” with “can” based on the use of verbal forms in standards.]
3.1.23
quality
set of characteristics of an object (3.1.16) that fulfils regulatory requirements (3.1.26)
Note 1 to entry: Quality includes the protection required by applicable regulatory requirements (3.1.26) aimed at
ensuring and maintaining the protection of health, safety and fundamental rights (3.4.2).
Note 2 to entry: In the context of this document, quality pertains to regulatory compliance to at least the EU AI Act,
including ensuring and maintaining the protection of health, safety and fundamental rights (3.4.2). It differs from the
concept of quality in EN ISO 9001 which includes expectations of customers and other interested parties (3.1.11).
[SOURCE: EN ISO 9000:2015, 3.6.2, modified — In the definition, removed “degree of” and “inherent”, and
added “regulatory” to “requirements”; removed original Notes 1 and 2; and added new Notes 1 and 2.]
3.1.24
quality objective
measurable goal established to ensure that regulatory requirements (3.1.26) are consistently met
throughout the life cycle (3.1.12)
Note 1 to entry: In the context of quality (3.1.19) management systems, quality objectives are set by the provider
(3.2.5), consistent with the quality policy (3.1.20), to achieve specific results.
Note 2 to entry: An objective in EN ISO/IEC 42001:2026, 3.6 and EN ISO 9000:2015, 3.7.1 is a general result to be
achieved. In this document, the term “quality objective” is linked specifically to the regulatory requirements (3.1.26).
3.1.25
quality policy
policy (3.1.20) related to quality (3.1.23)
[SOURCE: EN ISO 9000:2015, 3.5.9, modified — Removed notes.]
3.1.26
regulatory requirement
requirement (3.1.27) defined by applicable regulation and that is necessary to be met for the purposes of
complying with the regulation
Note 1 to entry: Applicable regulation includes at least the EU AI Act [1]
Note 2 to entry: Applicable regulation also includes law and regulation aimed at ensuring and maintaining the
protection of health, safety and fundamental rights (3.4.2).
3.1.27
requirement
need or expectation that is stated or obligatory
Note 1 to entry: A specified requirement is one that is stated, e.g. in documented information (3.1.7).
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024),
3.14, modified — Removed “generally implied” from the definition, replaced Note 1.]
3.1.28
top management
person or group of people who directs and controls an organization (3.2.5) at the highest level
Note 1 to entry: Top management has the power to delegate authority (3.1.2) and provide resources within the
organization (3.1.18).
Note 2 to entry: If the scope of the quality management system (3.1.29) covers only part of an organization of the
provider, then top management refers to those who direct and control that part of the organization of the provider.
Note 3 to entry: In different organizational contexts, top management can be referred to with different terms.
Note 4 to entry: Where the organization is a person, top management is that person.
Note 5 to entry: In this document, top management refers to personnel of the provider.
[SOURCE: ISO/IEC Directives Part 1, Consolidated ISO Supplement, Annex SL Appendix 2 (rev 4 2024), 3.3,
modified — Added “of the provider” to Note 2, added Notes 3, 4 and 5.]
3.1.29
scope of the quality management system
set of AI system(s) (3.2.1) that are covered under a quality (3.1.23) management system and the boundaries
that define where the quality management system applies
EXAMPLE Boundaries can include physical (geographic), organizational (3.1.18), functional, process, system,
service and interface boundaries.
3.1.30
systematic
pursuing defined objective(s) in a planned, step-by-step manner
[SOURCE: ISO/TR 18307:2001, 3.140]
3.1.31
validation
confirmation, through the provision of objective evidence (3.1.17), that the requirements (3.1.27) for a
specific intended purpose (3.2.3) or application have been fulfilled
Note 1 to entry: The objective evidence needed for a validation is the result of a test or other form of determination
such as performing alternative calculations or reviewing documents.
Note 2 to entry: The word “validated” is used to designate the corresponding status.
Note 3 to entry: The use conditions for validation can be real or simulated.
Note 4 to entry: The concept of validation as a procedure (3.1.21) is not directly related to validation datasets used
in machine learning.
[SOURCE: EN ISO 9000:2015, 3.8.13, modified — Changed “intended use” to “intended purpose” and added
Note 4.]
3.1.32
verification
confirmation, through the provision of objective evidence (3.1.17), that specified requirements (3.1.27) have
been fulfilled
Note 1 to entry: The objective evidence needed for a verification can be the result of an inspection or of other forms
of determination such as performing alternative calculations or reviewing documents.
Note 2 to entry: The activities carried out for verification are sometimes called a qualification process.
Note 3 to entry: The word “verified” is used to designate the corresponding status.
Note 4 to entry: Verification can rely on testing activities and results to provide objective evidence.
[SOURCE: EN 18228:—, 3.30]
3.1.33
responsible
responsibility
responsibilities
state of being accountable or answerable for an obligation
[SOURCE: EN ISO 17427-1:2018, 3.21, modified — Removed reference to other types of responsibilities.]
3.2 Terms relating to the EU AI Act
3.2.1
AI system
machine-based system that is designed to operate with varying levels of autonomy and that can exhibit
adaptiveness after deployment, and that, for explicit or implicit objectives, infers, from the input it receives,
how to generate outputs such as predictions, content, recommendations, or decisions that can influence
physical or virtual environments
Note 1 to entry: The verb “can” represents a possibility, not all AI systems that fit the above definition have this ability
to adapt after deployment.
[SOURCE: EU AI Act (Article 3(1)), modified — Removed “a”, replaced “may” with “can” based on the use
of verbal forms in standards, added Note 1.]
3.2.2
deployer
natural or legal person, public authority, agency or other body using an AI system (3.2.1) under its authority
except where the AI system is used in the course of a personal non-professional activity
[SOURCE: EU AI Act 2024/1689 (Article 3(4)), modified — Removed “a”.]
3.2.3
intended purpose
use for which an AI system (3.2.1) is intended by the provider (3.2.5), including the specific context and
conditions of use, as specified in the information supplied by the provider in the instructions for use,
promotional or sales materials and statements, as well as in the technical documentation
[SOURCE: EU AI Act 2024/1689, (Article 3(12)), modified — Removed “a”.]
3.2.4
performance
ability of an AI system (3.2.1) to achieve its intended purpose (3.2.3)
[SOURCE: EU AI Act 2024/1689, (Article 3(18)), modified — Removed “the”.]
3.2.5
provider
natural or legal person, public authority, agency or other body that develops an AI system (3.2.1) or a
general-purpose AI model or that has an AI system or a general-purpose AI model developed and places it
on the market or puts the AI system into service under its own name or trademark, whether for payment
or free of charge
Note 1 to entry: A distributor, importer, deployer (3.2.2) or other third party can be considered a provider of an AI
system in certain circumstances.
Note 2 to entry: For the purposes of this document, a provider shall be interpreted as a provider of high-risk AI
systems and not general-purpose AI models.
[SOURCE: EU AI Act 2024/1689, (Article 3(3)), modified — Removed “a”, added Note 2.]
3.2.6
reasonably foreseeable misuse
use of an AI system (3.2.1) in a way that is not in accordance with its intended purpose (3.2.3), but which
can result from reasonably foreseeable human behaviour or interaction with other systems, including
other AI systems
[SOURCE: EU AI Act 2024/1689, (Article 3(13)), modified — Removed “a”, replaced “may” with “can” based
on the verbal form of standards.]
3.2.7
substantial modification
change to an AI system (3.2.1) after its placing on the market or putting into service which is not foreseen
or planned in the initial conformity assessment (3.2.11) carried out by the provider (3.2.5) and as a result of
which the compliance of the AI system with the applicable regulatory requirements (3.1.26) is affected or
results in a modification to the intended purpose (3.2.3) for which the AI system has been assessed
Note 1 to entry: Rephrased from the EU AI Act Article 3(23) to reference applicable regulatory requirements instead
of a specific reference to the EU AI Act Chapter III, Section 2.
[SOURCE: EU AI Act 2024/1689, (Article 3(23)), modified as described in Note 1 to entry]
3.2.8
serious incident
incident or malfunctioning of an AI system (3.2.1) that directly or indirectly leads to any of the following:
a) the death of a person, or serious harm (3.4.3) to a person’s health;
b) a serious and irreversible disruption of the management or operation of critical infrastructure;
c) the infringement of obligations under Union law intended to protect fundamental rights (3.4.2);
d) serious harm (3.4.3) to property or the environment
[SOURCE: EU AI Act 2024/1689, (Article 3(49))]
3.2.9
AI system presenting a risk
product presenting a risk
product having the potential to affect adversely health and safety of persons in general, health and safety
in the workplace, protection of consumers, the environment, public security and other public interests,
protected by the applicable Union harmonization legislation, to a degree which goes beyond that
considered reasonable and acceptable in relation to its intended purpose (3.2.3) or under the normal or
reasonably foreseeable conditions of use of the product concerned, including the duration of use and,
where applicable, its putting into service, installation and maintenance requirements (3.1.27)
Note 1 to entry: For the purposes of this document, AI systems (3.2.1) presenting a risk (3.4.5) shall only be in so far
as they present risks to the health or safety, or to fundamental rights (3.4.2), of persons.
[SOURCE: Regulation (EU) 2019/1020, (Article 3(19))]
3.2.10
instructions for use
information provided by the provider (3.2.5) to inform the deployer of, in particular, an AI system’s (3.2.1)
intended purpose (3.2.3) and proper use
[SOURCE: EU AI Act 2024/1689, (Article 3(15))]
3.2.11
conformity assessment
process of demonstrating whether the requirements (3.1.27) set out in Chapter III, Section 2 relating to a
high-risk AI system have been fulfilled
Note 1 to entry: In this document, the term conformity assessment is used to refer to compliance with regulation,
which is different to conformity assessment in relation to conformity with a standard.
[SOURCE: EU AI Act (Article 3(20)), modified — Added Note 1 to entry.]
3.3 Terms relating to AI systems
3.3.1
training
model training
process (3.1.22) to determine or to improve the parameters of a machine learning model (3.3.3), based on
a machine learning algorithm (3.3.2), by using training data
[SOURCE: EN ISO/IEC 22989:2023, 3.3.15]
3.3.2
traceability
ability to trace the AI system (3.2.1) and its history
Note 1 to entry: Traceability includes information on how AI systems have been specified, developed, verified (3.1.28),
validated (3.1.29), operated, monitored (3.1.14) and retired.
3.3.3
AI system requirements
functional and non-functional requirements (3.1.27) derived from the intended purpose (3.2.3) and
regulatory requirements (3.1.26)
3.3.4
test procedure
sequence of test cases in execution order, with any associated actions required to set up preconditions and
perform wrap up activities post execution
[SOURCE: ISO/IEC/IEEE 29119-1:2022, 3.1.20]
3.3.5
user
person who interacts with the AI system (3.2.1) when deployed
[SOURCE: ISO 10377:2013, 2.29, modified — Replaced "product or service" with "AI system when
deployed".]
3.4 Terms relating to risk management
3.4.1
affected person
individual, or group of individuals, who is or are directly or indirectly impacted by an AI system (3.2.1)
when used in accordance with its intended purpose (3.2.3) or in the frame of reasonably foreseeable misuse
(3.2.6)
3.4.2
fundamental right
basic right(s) and freedom(s) held by every human being irrespective of birth, religion, belief, age, race,
ethnicity, sex, gender or any other status
Note 1 to entry: For the purposes of this document, fundamental rights and their applicability are those protected by
EU law, including the protection of the rights outlined in EU law, including the Charter of Fundamental Rights of the
EU (EU Charter) and the European Convention on Human Rights.
[SOURCE: EN 18228:—, 3.5.1]
3.4.3
harm
injury or damage to health of a person or groups of persons, or interference (3.4.10) with the fundamental
rights (3.4.2)
Note 1 to entry: For the purposes of this document, damage to property or the environment, and the disruption or
destruction of critical infrastructure, are considered harms when they can result in injury or damage to the health of
a natural person or groups of persons or interference with fundamental rights.
Note 2 to entry: Interference with fundamental rights can be tangible or intangible, physical, psychological, societal or
economic, irrespective of the rightholder’s awareness, in accordance with EU law, including the EU Charter on
Fundamental Rights [4].
Note 3 to entry: Safety in product safety risk (3.4.5) management standards is understood as the absence of
unacceptable risk. In the context of this document, safety refers to the protection from harm from the use of the AI
system (3.2.1).
[SOURCE: EN 18228:—, 3.6.3]
3.4.4
hazard
potential source of harm (3.4.3)
[SOURCE: ISO/IEC Guide 51:2014, 3.2]
3.4.5
risk
combination of the probability of an occurrence of harm (3.4.3) and the severity (3.4.8) of that harm
Note 1 to entry: The probability of occurrence includes the exposure to a hazardous situation and the pos
...