

ISO/IEC 25791-2:2026
(Main)Information technology — OpenID connect FAPI security profile 1.0 — Part 2: Advanced
- Abstract
This part of the document specifies the method of applications to obtain the OAuth tokens in an appropriately secure manner for higher risk access to data; applications to use OpenID Connect to identify the customer; and using tokens to interact with the REST endpoints that provides protected data. This document is applicable to higher risk use cases which includes commercial and investment banking and other similar industries.
- Status
- Published
- Publication Date
- 17-Nov-2026
- Technical Committee
- ISO/IEC JTC 1 - Information technology
- Drafting Committee
- ISO/IEC JTC 1 - Information technology
- Current Stage
- 6060 - International Standard published
- Start Date
- 18-Nov-2026
- Completion Date
- 18-Nov-2026
ISO/IEC 25791-2:2026 is an ISO International Standard from ISO. It specifies the advanced FAPI security profile for OpenID Connect, covering how applications obtain OAuth tokens securely, identify the customer with OpenID Connect, and use those tokens to call protected REST endpoints. It is written for higher-risk deployments such as commercial and investment banking and similar industries, and it is the first edition.
What does ISO/IEC 25791-2:2026 specify?
ISO/IEC 25791-2:2026 specifies an advanced security profile for OAuth and OpenID Connect use in higher-risk APIs. The document focuses on confidential-client deployments that need stronger protection against request tampering, response tampering, phishing, and token misuse.
The document is organized into these main clauses:
- Clause 1 - Scope
- Clause 2 - Normative references
- Clause 3 - Terms and definitions
- Clause 4 - Symbols and abbreviated terms
- Clause 5 - Advanced security profile
- Clause 6 - Accessing protected resources (using tokens)
- Clause 8 - Security considerations
- Clause 9 - Privacy considerations
- Clause 10 - IANA Considerations
It also includes two informative annexes.
| Annex | What it covers |
|---|---|
| Annex A | Examples, including JWKs, a request object, signed and encrypted ID Tokens, a JARM response, and a private_key_jwt client assertion |
| Annex B | Acknowledgement of contributors |
What are the key requirements of ISO/IEC 25791-2:2026?
ISO/IEC 25791-2:2026 sets out the controls that make an OpenID Connect and OAuth deployment suitable for higher-risk data access. The most important requirements are in clause 5 for authorization handling, clause 6 for protected resources, and clause 8 for transport and cryptographic security.
Authorization response security
ISO/IEC 25791-2:2026 requires the authorization server to protect authorization responses in one of two ways: by using an ID Token as a detached signature in the code id_token flow, or by using JWT Secured Authorization Response Mode for OAuth 2.0 (JARM) with code and response_mode jwt. In practice, this means the response is not left as plain front-channel data that can be altered on the browser path.
If the ID Token route is used, the authorization server shall support OpenID Connect, signed ID Tokens, and return an ID Token that binds the authorization response. The client shall check the s_hash value against the state it sent. That verification is what helps detect response tampering and state injection.
If JARM is used, the authorization server shall create JWT-secured authorization responses as specified in JARM, and the client shall verify those responses as required by JARM. This gives the client a signed response object to validate instead of relying on unprotected parameters.
Authorization server and confidential client controls
ISO/IEC 25791-2:2026 requires the authorization server to accept only a JWS signed JWT request object, passed either by value with request or by reference with request_uri. The server shall use only the parameters contained in that signed request object, require aud, exp, and nbf claims with short lifetimes, and not support public clients. This means the request content is integrity protected before the user sees or approves it.
The authorization server shall authenticate the confidential client with either tls_client_auth, self_signed_tls_client_auth, or private_key_jwt. The client, in turn, shall send the authorization request inside a signed request object, and if it does not use RFC 9126 it shall also send duplicate response_type, client_id, and scope parameters in OAuth request syntax. In practice, implementers must keep the browser-visible request aligned with the signed request object.
When RFC 9126 Pushed Authorization Requests (PAR) is used, both the authorization server and the client shall use PKCE with S256 as the code challenge method. That tightens the code exchange step for pushed requests and avoids weaker challenge methods.
Access to protected resources
ISO/IEC 25791-2:2026 requires protected resources to accept only sender-constrained access tokens. They shall not accept bearer access tokens, and they shall follow RFC 8705. For implementers, this means the access token must be bound to the client so that a stolen token is not enough to call the API.
The client supporting this document shall also follow the baseline client provisions from FAPI Security Profile 1.0 - Part 1: Baseline. The advanced profile builds on that baseline rather than replacing it.
Transport, keys, and algorithms
ISO/IEC 25791-2:2026 requires all interactions to be encrypted with TLS over HTTPS. It restricts cipher suites to those recommended in BCP195, with limited additional flexibility for the authorization endpoint when browser interoperability or local regulations require it. This matters because the profile handles confidential authentication and token data.
For JWS, both clients and authorization servers shall use PS256 or ES256, shall not use none, and should avoid RSASSA-PKCS1-v1_5 algorithms such as RS256. For JWE, both sides shall not use RSA1_5. The document also requires jwks_uri endpoints to be served over TLS and recommends avoiding x5u and jku headers and duplicate kid values in a JWK set.
What terms does ISO/IEC 25791-2:2026 define?
ISO/IEC 25791-2:2026 uses these abbreviations in its security model and flows:
- FAPI - financial-grade API; the name used for the security profile covered by this document.
- JARM - JWT-secured authorization response mode; a way to return the authorization response inside a JWT.
- JAR - JWT-secured authorization request; a signed request object used to protect request parameters.
- PKCE - proof key for code exchange; the code challenge and verifier mechanism used to strengthen the code flow.
- MTLS - mutual transport layer security; the certificate-based TLS method used for client authentication and sender-constrained tokens.
- RP - relying party; the client side that receives and processes the OpenID Connect response.
- TLS - transport layer security; the channel protection used for confidential exchanges.
- REST - representational state transfer; the style of protected endpoints the tokens are used to access.
Who uses ISO/IEC 25791-2:2026?
ISO/IEC 25791-2:2026 is used by teams building or operating higher-risk OAuth and OpenID Connect systems. The introductory text says the main audience is parties that already have a certified OpenID Connect implementation and want a higher level of security.
Typical users include:
- authorization server implementers
- confidential client developers
- protected resource and API platform teams
- security architects in banking and payment environments
- quality and conformance teams checking OpenID Connect behavior
- auditors and assessors reviewing token handling, key use, and transport security
The scope specifically names commercial and investment banking and similar industries, where data exposure or payment initiation creates higher risk.
Which standards are used with ISO/IEC 25791-2:2026?
ISO/IEC 25791-2:2026 relies on several normative references that supply the underlying OAuth, OpenID Connect, and privacy behavior:
- FAPI Security Profile 1.0 - Part 1: Baseline - provides the baseline controls that this advanced part extends.
- ISO/IEC 29100 - provides the privacy framework used by the terms and privacy considerations.
- RFC 6749 - provides the OAuth 2.0 authorization framework.
- RFC 6750 - provides bearer token usage.
- RFC 7636 - provides PKCE.
- OpenID Connect Core 1.0 incorporating errata set 2 - provides OpenID Connect identity and token behavior.
- RFC 8705 - provides MTLS client authentication and certificate-bound access tokens.
- JARM - provides JWT-secured authorization response mode.
- RFC 9101 - provides JWT-secured authorization requests.
- RFC 9126 - provides pushed authorization requests.
What does the ISO/IEC 25791-2:2026 document contain?
ISO/IEC 25791-2:2026 contains security guidance, threat discussion, privacy considerations, and an IANA registration update for the s_hash claim. Clause 8 discusses attacks such as endpoint mix-up, request and response parameter injection, token phishing, session fixation, and weak key distribution, and explains the controls used to reduce them.
Annex A gives worked examples that are useful for implementation and testing. It includes a sample JWK for client and server examples, a request object, a signed ID Token, a signed and encrypted ID Token, a JARM response, and a private_key_jwt client assertion.
Clause 10 adds s_hash to the JSON Web Token Claims registry. That makes the state hash value a registered JWT claim for use in the response-protection mechanism described in clause 5.
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.

Bureau Veritas
Bureau Veritas is a world leader in laboratory testing, inspection and certification services.
DNV
DNV is an independent assurance and risk management provider.
Sponsored listings
Frequently Asked Questions
ISO/IEC 25791-2:2026 is a standard published by the International Organization for Standardization (ISO). Its full title is "Information technology — OpenID connect FAPI security profile 1.0 — Part 2: Advanced". This standard covers: This part of the document specifies the method of applications to obtain the OAuth tokens in an appropriately secure manner for higher risk access to data; applications to use OpenID Connect to identify the customer; and using tokens to interact with the REST endpoints that provides protected data. This document is applicable to higher risk use cases which includes commercial and investment banking and other similar industries.
This part of the document specifies the method of applications to obtain the OAuth tokens in an appropriately secure manner for higher risk access to data; applications to use OpenID Connect to identify the customer; and using tokens to interact with the REST endpoints that provides protected data. This document is applicable to higher risk use cases which includes commercial and investment banking and other similar industries.
ISO/IEC 25791-2:2026 is classified under the following ICS (International Classification for Standards) categories: 35.030 - IT Security. The ICS classification helps identify the subject area and facilitates finding related standards.
ISO/IEC 25791-2:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
International
Standard
ISO/IEC 25791-2
First edition
Information technology — OpenID
2026-11
connect FAPI security profile 1.0 —
Part 2:
Advanced
Technologies de l'information — Profil de sécurité 1.0 basé sur le
protocole OpenID Connect conçu pour les API financières, FAPI —
Partie 2: Niveau avancé
Reference number
© ISO/IEC 2026
All rights reserved.
This ISO publication is protected by copyright and is owned by ISO and/or its licensors.
The content of this ISO publication is provided under licence, not sold. Use is subject to the applicable licence terms issued by ISO,
an ISO member body, or an authorized third-party distributor.
Except as required for implementation or expressly permitted by a separate licence, no part of this ISO publication may be
reproduced, distributed, modified, used, or made available in any form or by any means – electronic or mechanical, including
photocopying, scanning, recording, or posting on internal or external digital platforms.
Any use beyond the scope of the granted rights is prohibited and may result in legal action.
ISO copyright office
CP 401 • CH-1214 Vernier, Geneva
Phone: +41 22 749 01 11
Email: copyright@iso.org
Website: www.iso.org
Published in Switzerland
© ISO/IEC 2026 – All rights reserved
ii
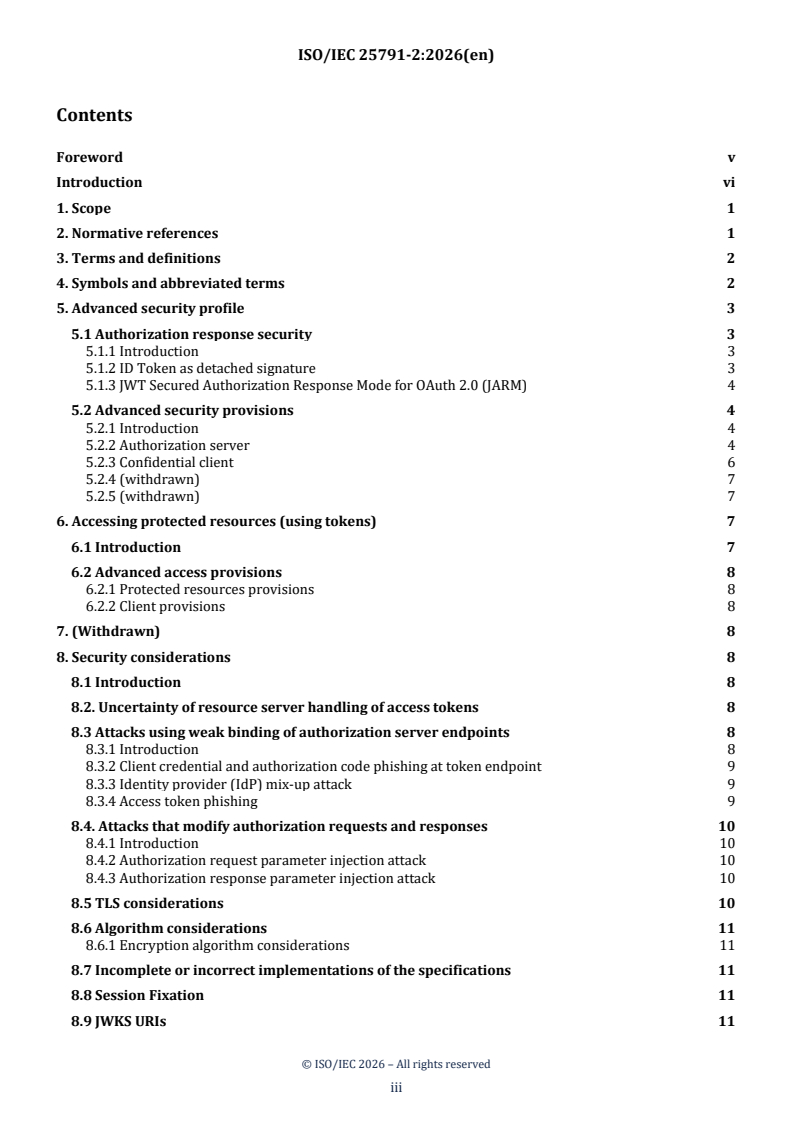
Contents
Foreword v
Introduction vi
1. Scope 1
2. Normative references 1
3. Terms and definitions 2
4. Symbols and abbreviated terms 2
5. Advanced security profile 3
5.1 Authorization response security 3
5.1.1 Introduction 3
5.1.2 ID Token as detached signature 3
5.1.3 JWT Secured Authorization Response Mode for OAuth 2.0 (JARM) 4
5.2 Advanced security provisions 4
5.2.1 Introduction 4
5.2.2 Authorization server 4
5.2.3 Confidential client 6
5.2.4 (withdrawn) 7
5.2.5 (withdrawn) 7
6. Accessing protected resources (using tokens) 7
6.1 Introduction 7
6.2 Advanced access provisions 8
6.2.1 Protected resources provisions 8
6.2.2 Client provisions 8
7. (Withdrawn) 8
8. Security considerations 8
8.1 Introduction 8
8.2. Uncertainty of resource server handling of access tokens 8
8.3 Attacks using weak binding of authorization server endpoints 8
8.3.1 Introduction 8
8.3.2 Client credential and authorization code phishing at token endpoint 9
8.3.3 Identity provider (IdP) mix-up attack 9
8.3.4 Access token phishing 9
8.4. Attacks that modify authorization requests and responses 10
8.4.1 Introduction 10
8.4.2 Authorization request parameter injection attack 10
8.4.3 Authorization response parameter injection attack 10
8.5 TLS considerations 10
8.6 Algorithm considerations 11
8.6.1 Encryption algorithm considerations 11
8.7 Incomplete or incorrect implementations of the specifications 11
8.8 Session Fixation 11
8.9 JWKS URIs 11
© ISO/IEC 2026 – All rights reserved
iii
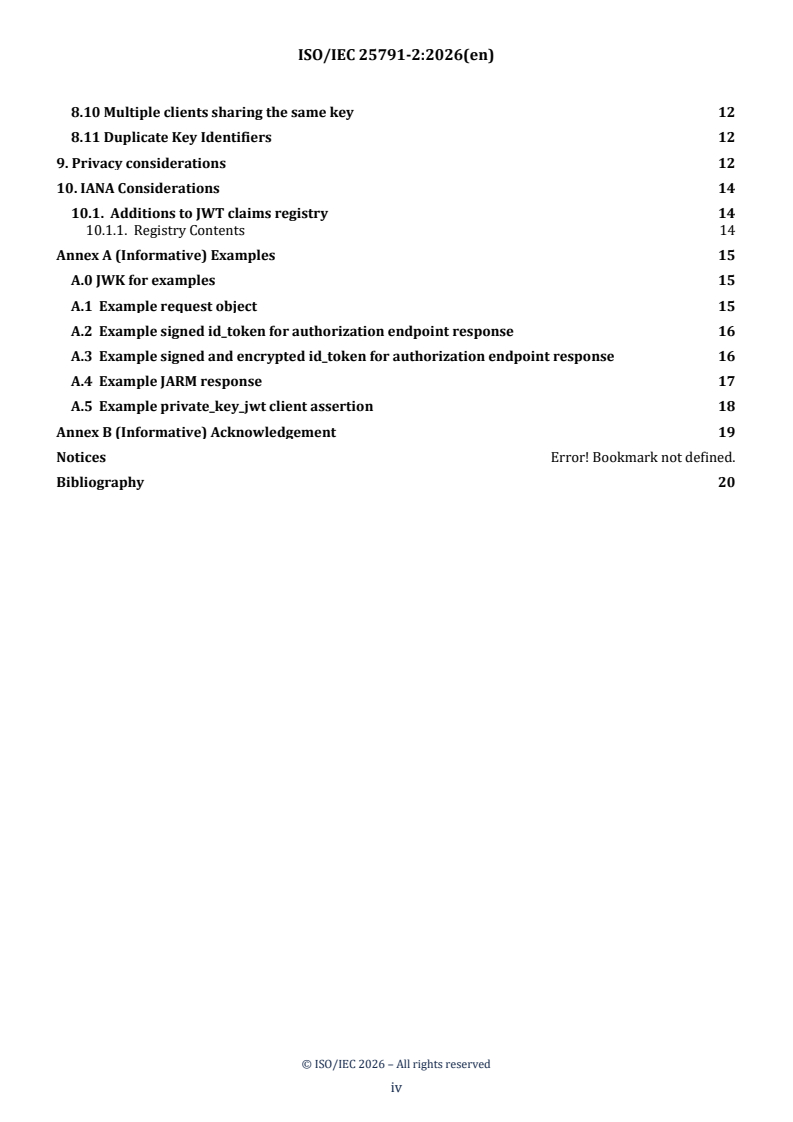
8.10 Multiple clients sharing the same key 12
8.11 Duplicate Key Identifiers 12
9. Privacy considerations 12
10. IANA Considerations 14
10.1. Additions to JWT claims registry 14
10.1.1. Registry Contents 14
Annex A (Informative) Examples 15
A.0 JWK for examples 15
A.1 Example request object 15
A.2 Example signed id_token for authorization endpoint response 16
A.3 Example signed and encrypted id_token for authorization endpoint response 16
A.4 Example JARM response 17
A.5 Example private_key_jwt client assertion 18
Annex B (Informative) Acknowledgement 19
Notices Error! Bookmark not defined.
Bibliography 20
© ISO/IEC 2026 – All rights reserved
iv
Foreword
ISO (the International Organization for Standardization) and IEC (the International Electrotechnical
Commission) form the specialized system for worldwide standardization. National bodies that are members
of ISO or IEC participate in the development of International Standards through technical committees
established by the respective organization to deal with particular fields of technical activity. ISO and IEC
technical committees collaborate in fields of mutual interest. Other international organizations, governmental
and non-governmental, in liaison with ISO and IEC, also take part in the work.
The procedures used to develop this document and those intended for its further maintenance are described
in the ISO/IEC Directives, Part 1. In particular, the different approval criteria needed for the different types of
document should be noted (see www.iso.org/directives or www.iec.ch/members_experts/refdocs).
ISO and IEC draw attention to the possibility that the implementation of this document may involve the use of
(a) patent(s). ISO and IEC take no position concerning the evidence, validity or applicability of any claimed
patent rights in respect thereof. As of the date of publication of this document, ISO and IEC had not received
notice of (a) patent(s) which may be required to implement this document. However, implementers are
cautioned that this may not represent the latest information, which may be obtained from the patent database
available at www.iso.org/patents and https://patents.iec.ch. ISO and IEC shall not be held responsible for
identifying any or all such patent rights.
Any trade name used in this document is information given for the convenience of users and does not
constitute an endorsement.
For an explanation of the voluntary nature of standards, the meaning of ISO specific terms and expressions
related to conformity assessment, as well as information about ISO's adherence to the World Trade
Organization (WTO) principles in the Technical Barriers to Trade (TBT), see www.iso.org/iso/foreword.html.
In the IEC, see www.iec.ch/understanding-standards.
This document was prepared by the OpenID Foundation (OIDF) (as FAPI Security Profile 1.0 - Part 2:
Advanced) and drafted in accordance with its editorial rules. It was adopted, under the JTC 1 PAS procedure,
by Joint Technical Committee ISO/IEC JTC 1, Information technology.
A list of all parts in the ISO/IEC 25791 series can be found on the ISO and IEC websites.
Any feedback or questions on this document should be directed to the user’s national standards body. A
complete listing of these bodies can be found at www.iso.org/members.html and www.iec.ch/national-
committees.
© ISO/IEC 2026 – All rights reserved
v
Introduction
FAPI is a highly secured OAuth profile that aims to provide specific implementation guidelines for security
and interoperability. The FAPI security profile can be applied to APIs in any market area that requires a higher
level of security than provided by standard OAuth or OpenID Connect. Among other security enhancements,
this specification provides a secure alternative to screen scraping. Screen scraping accesses user’s data and
functions by impersonating a user through password sharing. This brittle, inefficient, and insecure practice
creates security vulnerabilities which require institutions to allow what appears to be an automated attack
against their applications.
This document is Part 2 of FAPI Security Profile 1.0 that specifies an advanced security profile of OAuth that
is suitable to be used for protecting APIs with high inherent risk. Examples include APIs that give access to
highly sensitive data or that can be used to trigger financial transactions (e.g., payment initiation). This
document specifies the controls against attacks such as: authorization request tampering, authorization
response tampering including code injection, state injection, and token request phishing. Additional details
are available in the security considerations section.
Although it is possible to code an OpenID provider and relying party from first principles using this
specification, the main audience for this specification is parties who already have a certified implementation
of OpenID Connect and want to achieve a higher level of security. Implementers are encouraged to understand
the security considerations contained in Section 8.7 before embarking on a ‘from scratch’ implementation.
© ISO/IEC 2026 – All rights reserved
vi
International Standard ISO/IEC 25791-2:2026(en)
Information technology — OpenID connect FAPI security
Profile 1.0 —
Part 2:
Advanced
1. Scope
This part of the document specifies the method of
• applications to obtain the OAuth tokens in an appropriately secure manner for higher risk access to
data;
• applications to use OpenID Connect to identify the customer; and
• using tokens to interact with the REST endpoints that provides protected data.
This document is applicable to higher risk use cases which includes commercial and investment banking and
other similar industries.
2. Normative references
The following documents are referred to in the text in such a way that some or all of their content constitutes
requirements of this document. For dated references, only the edition cited applies. For undated references,
the latest edition of the referenced document (including any amendments) applies.
FAPI, Security Profile 1.0 – Part 1: Baseline
ISO/IEC 29100, Information technology – Security techniques – Privacy framework
RFC 6749, The OAuth 2.0 Authorization Framework
RFC 6750, The OAuth 2.0 Authorization Framework: Bearer Token Usage
RFC 7636, Proof Key for Code Exchange by OAuth Public Clients
OIDC, OpenID Connect Core 1.0 incorporating errata set 2
RFC 8705, OAuth 2.0 Mutual-TLS Client Authentication and Certificate-Bound Access Tokens
JARM, JWT Secured Authorization Response Mode for OAuth 2.0 (JARM)
RFC 9101, OAuth 2.0 Authorization Framework: JWT-Secured Authorization Request (JAR)
RFC 9126, OAuth 2.0 Pushed Authorization Requests (PAR)
© ISO/IEC 2026 – All rights reserved
3. Terms and definitions
For the purpose of this document, the terms defined in RFC 6749, RFC 6750, RFC 7636, OpenID Connect Core,
and ISO/IEC 29100 apply.
4. Symbols and abbreviated terms
API – application programming interface
CSRF – cross site request forgery
DN – distinguished name
FAPI – financial-grade API (FAPI is now used as a name rather than an acronym)
HTTP – hypertext transfer protocol
HTTPS – hypertext transfer protocol secure
JAR – JWT-secured authorization request
JARM – JWT-secured authorization response mode
JOSE – javascript object signing and encryption
JSON – javascript object notation
JWE – JSON web encryption
JWK – JSON web key
JWKS – JSON web key sets
JWS – JSON web signature
JWT – JSON web token
MTLS – mutual transport layer security
OIDF – OpenID foundation
PAR – pushed authorization request
PII – personally identifiable information
PKCE – proof key for code exchange
REST – representational state transfer
RP – relying party
TLS – transport layer security
URI – uniform resource identifier
URL – uniform resource locator
© ISO/IEC 2026 – All rights reserved
5. Advanced security profile
5.1 Authorization response security
5.1.1 Introduction
The OIDF FAPI security profile specifies security requirements for high risk API resources protected by the
OAuth 2.0 Authorization Framework that consists of RFC 6749, RFC 6750, RFC 7636, and other specifications.
There are different levels of risks associated with access to these APIs. For example, read and write access to
a bank API has a higher financial risk than read-only access. As such, the security profiles of the authorization
framework protecting these APIs are also different.
This profile describes security provisions for the server and client that are appropriate for highly secured APIs
by defining the measures to mitigate:
• attacks that leverage the weak binding of endpoints in RFC 6749 (e.g., malicious endpoint attacks, IdP
mix-up attacks), and
• attacks that modify authorization requests and responses unprotected in RFC 6749.
This profile does not support public clients.
The following ways are specified to protect against modifications of authorization responses:
Implementations can leverage OpenID Connect's hybrid flow that returns an ID Token in the authorization
response or they can utilize the JWT Secured Authorization Response Mode for OAuth 2.0 (JARM) that returns
and protects all authorization response parameters in a JWT.
5.1.2 ID Token as detached signature
While the name ID Token (as used in the OpenID Connect hybrid flow) suggests that it is something that
provides the identity of the resource owner (subject), it is not necessarily so. While it does identify the
authorization server by including the issuer identifier, it is perfectly fine to have an ephemeral subject
identifier. In this case, the ID Token acts as a detached signature of the issuer to the authorization response
and it was an explicit design decision of OpenID Connect Core to make the ID Token act as a detached signature.
This document leverages this fact and protects the authorization response by including the hash of all of the
unprotected response parameters, e.g. code and state, in the ID Token.
While the hash of the code is defined in OIDC, the hash of the state is not defined. Thus this document defines
it as follows.
5.1.3 s_hash
State hash value. Its value is the base64url encoding of the left-most half of the hash of the octets of the
ASCII representation of the state value, where the hash algorithm used is the hash algorithm used in
the alg header parameter of the ID Token's JOSE header. For instance, if the alg is HS512, hash the state
value with SHA-512, then take the left-most 256 bits and base64url encode them. The s_hash value is
a case sensitive string.
© ISO/IEC 2026 – All rights reserved
5.1.4 JWT Secured Authorization Response Mode for OAuth 2.0 (JARM)
An authorization server may protect authorization responses to clients using the "JWT Secured Authorization
Response Mode" JARM.
JARM allows a client to request that an authorization server encodes the authorization response (of any
response type) in a JWT. It is an alternative to utilizing ID Tokens as detached signatures for providing
increased security on authorization responses and can be used with plain OAuth.
This specification facilitates use of JARM in conjunction with the response type code.
NOTE: JARM can be used to protect OpenID Connect authentication responses. In this case, the OpenID RP
would use response type code, response mode jwt and scope openid. This means JARM protects the
authentication response (instead of the ID Token) and the ID Token containing end-user claims is obtained
from the token endpoint. This facilitates privacy since no end-user claims are sent through the front channel.
It also provides decoupling of message protection and identity providing since a client (or RP) can basically
use JARM to protect all authorization responses and turn on OpenID if needed (e.g. to log the user in).
5.2 Advanced security provisions
5.2.1 Introduction
API resources may contain sensitive data and/or have increased security requirements. In order to fulfill
different security needs, FAPI Security Profile 1.0 defines an advanced profile that is beyond the baseline
security requirements defined in the Part 1: Baseline document.
As a profile of the OAuth 2.0 Authorization Framework, this document mandates the following for the
advanced profile of the FAPI Security Profile 1.0.
5.2.2 Authorization server
5.2.2.1 Authorization server provisions
The authorization server shall support the provisions specified in clause 5.2.2.0 of FAPI Security Profile 1.0 -
Part 1: Baseline, with the exception that Section 5.2.2.0.7 (enforcement of RFC 7636) is not required.
In addition, the authorization server
1. shall require a JWS signed JWT request object passed by value with the request parameter or by
reference with the request_uri parameter;
2. shall require
1. the response_type value code id_token, or
2. the response_type value code in conjunction with the response_mode value jwt;
3. (moved to 5.2.2.1);
4. (moved to 5.2.2.1);
5. shall only issue sender-constrained access tokens;
© ISO/IEC 2026 – All rights reserved
6. shall support RFC 8705 as mechanism for constraining the legitimate senders of access tokens;
7. (withdrawn);
8. (moved to 5.2.2.1);
9. (moved to 5.2.2.1);
10. shall only use the parameters included in the signed request object passed via the request or
request_uri parameter;
11. may support the pushed authorization request endpoint as described in RFC 9126;
12. (withdrawn);
13. shall require the request object to contain an exp claim that has a lifetime of no longer than 60 minutes
after the nbf claim;
14. shall authenticate the confidential client using one of the following methods (this overrides FAPI
Security Profile 1.0 - Part 1: Baseline clause 5.2.2.0.4):
i. tls_client_auth or self_signed_tls_client_auth as specified in section 2 of RFC 8705,
or
ii. private_key_jwt as specified in section 9 of OIDC;
15. shall require the aud claim in the request object to be, or to be an array containing, the authorization
server's issuer identifier URL;
16. shall not support public clients;
17. shall require the request object to contain an nbf claim that is no longer than 60 minutes in the past;
and
18. shall require RFC 9126 requests, if supported, to use PKCE (RFC 7636) with S256 as the code challenge
method.
NOTE: RFC 8705 is currently the only mechanism for sender-constrained access tokens that has been
widely deployed. Future versions of this specification are likely to allow other mechanisms for sender-
constrained access tokens.
NOTE: PAR does not present any additional security concerns that necessitated the requirement to use
PKCE - the reason PKCE is not required in other cases is merely to be backwards compatible with earlier
drafts of this standard.
EXAMPLE
See Annex A for additional information.
5.2.2.2 ID Token as detached signature
In addition, if the response_type value code id_token is used, the authorization server
1. shall support OIDC;
2. shall support signed ID Tokens;
© ISO/IEC 2026 – All rights reserved
3. should support signed and encrypted ID Tokens;
4. shall return ID Token as a detached signature to the authorization response;
5. shall include state hash, s_hash, in the ID Token to protect the state value if the client supplied a
value for state. s_hash may be omitted from the ID Token returned from the token endpoint when
s_hash is present in the ID Token returned from the authorization endpoint; and
6. should not return sensitive PII in the ID Token in the authorization response, but if it needs to, then it
should encrypt the ID Token.
NOTE: The authorization server may return more claims in the ID Token from the token endpoint than in the
one from the authorization response.
5.2.2.3 JARM
In addition, if the response_type value code is used in conjunction with the response_mode value jwt,
the authorization server
1. shall create JWT-secured authorization responses as specified in JARM, subclause 2.3.
5.2.3 Confidential client
5.2.3.1 General provisions
A confidential client shall support the provisions specified in clause 5.2.3 and 5.2.4 of FAPI Security Profile 1.0
- Part 1: Baseline, except for RFC 7636 support.
In addition, the confidential client
1. shall support RFC 8705 as mechanism for sender-constrained access tokens;
2. shall include the request or request_uri parameter as defined in Section 6 of OIDC in the
authentication request;
3. shall ensure the authorization server has authenticated the user to an appropriate level of assurance
for the client's intended purpose;
4. (moved to 5.2.3.1);
5. (withdrawn);
6. (withdrawn);
7. (moved 5.2.3.1);
8. shall send all parameters inside the authorization request's signed request object;
9. shall additionally send duplicates of the response_type, client_id, and scope
parameters/values using the OAuth 2.0 request syntax as required by Section 6.1 of the OpenID
Connect specification if not using RFC 9126;
10. shall send the aud claim in the request object as the authorization server's issuer identifier URL;
© ISO/IEC 2026 – All rights reserved
11. shall send an exp claim in the request object that has a lifetime of no longer than 60 minutes;
12. (moved to 5.2.3.1);
13. (moved to 5.2.3.1);
14. shall send an nbf claim in the request object;
15. shall use RFC 7636 with S256 as the code challenge method if using RFC 9126; and
16. shall additionally send a duplicate of the client_id parameter/value using the OAuth 2.0 request
syntax to the authorization endpoint, as required by Section 5 of RFC 9101, if using RFC 9126.
5.2.3.2 ID Token as detached signature
In addition, if the response_type value code id_token is used, the client
1. shall include the value openid into the scope parameter in order to activate OIDC support;
2. shall require JWS signed ID Token be returned from endpoints;
3. shall verify that the authorization response was not tampered using ID Token as the detached
signature;
4. shall verify that s_hash value is equal to the value calculated from the state value in the authorization
response in addition to all the requirements in 3.3.2.12 of OIDC; and
5. shall support both signed and signed & encrypted ID Tokens.
NOTE: This enables the client to verify that the authorization response was not tampered with, using the ID
Token as a detached signature.
5.2.3.3 JARM
In addition, if the response_type value code is used in conjunction with the response_mode value jwt, the
client
1. shall verify the authorization responses as specified in JARM.
5.2.4 (withdrawn)
5.2.5 (withdrawn)
6. Accessing protected resources (using tokens)
6.1 Introduction
The FAPI endpoints are OAuth 2.0 protected resource endpoints that return protected information for the
resource owner associated with the submitted access token.
© ISO/IEC 2026 – All rights reserved
6.2 Advanced access provisions
6.2.1 Protected resources provisions
The protected resources supporting this document
1. shall support the provisions specified in clause 6.2.1 FAPI Security Profile 1.0 - Part 1: Baseline; and
2. shall adhere to the requirements in RFC 8705.
6.2.2 Client provisions
The client supporting this document shall support the provisions specified in clause 6.2.2 of FAPI Security
Profile 1.0 - Part 1: Baseline.
7. (Withdrawn)
8. Security considerations
8.1 Introduction
As a profile of the OAuth 2.0 Authorization Framework, this specification references the security
considerations defined in Section 10 of RFC 6749, as well as RFC 6819 - OAuth 2.0 Threat Model and Security
Considerations, which details various threats and mitigations. The security of OAuth 2.0 has been proven
formally - under certain assumptions - in OAUTHSEC. A detailed security analysis of FAPI Security Profile 1.0
can be found in FAPISEC.
8.2. Uncertainty of resource server handling of access tokens
There is no way that the client can find out whether the resource access was granted for a bearer or sender-
constrained access token. The two differ in the risk profile and the client may want to differentiate them. The
protected resources that conform to this document differentiate them. The protected resources that conform
to this document shall not accept a bearer access token. They shall only support sender-constrained access
tokens via RFC 8705.
8.3 Attacks using weak binding of authorization server endpoints
8.3.1 Introduction
In RFC 6749 and RFC 6750, the endpoints that the authorization server offers are not tightly bound together.
There is no notion of authorization server identifier (issuer identifier) and it is not indicated in the
authorization response unless the client uses different redirection URI per authorization server. While it is
assumed in the OAuth model, it is not explicitly spelled out and thus many clients use the same redirection
URI for different authorization servers exposing an attack surface. Several attacks have been identified and
the threats are explained in detail in RFC 6819.
© ISO/IEC 2026 – All rights reserved
8.3.2 Client credential and authorization code phishing at token endpoint
In this attack, the client developer is socially engineered into believing that the token endpoint has changed to
the URL that is controlled by the attacker. As a result, the client sends the code and the client secret to the
attacker, which will be replayed subsequently.
When the FAPI Security Profile 1.0 client uses RFC 8705, the client's se
...