

ISO/IEC 19941-1:2026
(Main)Cloud computing — Interoperability and portability — Part 1: Overview, terminology and concepts
- Abstract
This document specifies cloud computing interoperability and portability types, the relationship and interactions between these two cross-cutting aspects of cloud computing and distributed platforms, as well as common terminology and concepts used to discuss interoperability and portability, particularly relating to cloud services. The goal of this document is to ensure that all parties involved in cloud computing, particularly cloud service customers (CSC), cloud service providers (CSP) and cloud service partners (CSN) acting as cloud service developers, have a common understanding of interoperability and portability for their specific needs, including switching service provision from one CSP to another. This common understanding helps to achieve interoperability and portability in cloud computing by establishing common terminology and concepts.
- Status
- Published
- Publication Date
- 09-Nov-2026
- Technical Committee
- ISO/IEC JTC 1/SC 38 - Cloud computing and distributed platforms
- Drafting Committee
- ISO/IEC JTC 1/SC 38/WG 3 - Cloud Computing Fundamentals (CCF)
- Current Stage
- 6060 - International Standard published
- Start Date
- 10-Nov-2026
- Completion Date
- 10-Nov-2026
ISO/IEC 19941-1 is an ISO/IEC standard from ISO that gives the overview, terminology and concepts for cloud computing interoperability and portability. It explains the main types of interoperability and portability, how they relate, and the terms used to discuss them for cloud services and related distributed-platform scenarios. It is aimed at Cloud Service Customers (CSCs), Cloud Service Providers (CSPs) and Cloud Service Partners (CSNs) acting as cloud service developers.
What does ISO/IEC 19941-1 specify?
ISO/IEC 19941-1 specifies cloud computing interoperability and portability types, the relationship between them, and the common terminology used to discuss them. The scope is especially practical for cloud services: it is about how systems, data and applications can work together, move between services, and be switched from one CSP to another.
The document is organized as follows:
| Annex | What it covers |
|---|---|
| Annex A | Relationship between cloud interoperability, portability and switching |
| Annex B | How cloud interoperability, portability and switching support each other |
The main body moves from definitions and concepts to facet models, then to cloud capability types, data portability, application portability, switching, multi-CSP use, SLA aspects and data categories. That structure matters because it lets a reader go from high-level concepts to the specific topic they need for design, migration, procurement or policy work.
What are the key requirements of ISO/IEC 19941-1?
ISO/IEC 19941-1 does not prescribe a single technical design. Instead, it classifies the problem space and gives the concepts a CSC, CSP or CSN should use when planning interoperability, portability or switching.
1. Clause 5 defines the main facet models
Clause 5 breaks the subject into cloud interoperability, cloud data portability and cloud application portability, and it explains the relationship between interoperability and portability. It also highlights key challenges such as security, identity and access management, interfaces, APIs, open source and intermediary services. In practice, this helps a team decide whether a problem is about exchange, migration, policy, or service composition before they start designing a solution.
2. Clause 6 maps those facets to cloud capability types
Clause 6 uses cloud capability types as classification anchors and presents functional component views for interoperability, data portability and application portability. It distinguishes the user layer, access layer, service layer and resource layer, and shows how CSCs interact with cloud services and with their own non-cloud systems. In practice, this gives architects a way to locate where portability work actually happens - for example, in service interfaces, application artefacts, or data transfer paths.
3. Clause 7 classifies cloud interoperability by facet
Clause 7 identifies transport interoperability, syntactic interoperability, semantic data interoperability, behavioural interoperability and policy interoperability. It also makes clear that interoperability applies separately to the service interface, administration interface and business interface. For a buyer or engineer, that means one successful API connection does not automatically mean the service is interoperable in behaviour, semantics or policy.
4. Clause 8 classifies cloud data portability
Clause 8 divides data portability into syntactic, semantic and policy portability, and Table 5 maps those portability types across infrastructure, platform and application capability types. Clause 8.4 defines data policy portability in terms of legal, organizational and policy frameworks, including locality, access rights, use rights and privacy responsibilities. Clause 8.5 treats cloud service derived data as a special case that must be assessed individually, because some derived data are useful to the CSC and some are controlled by the CSP or constrained by privacy, confidentiality or aggregation issues.
5. Clause 9 classifies cloud application portability
Clause 9 treats application portability as movement of an application between a CSC’s on-premises system and a cloud service, or between cloud services. It separates syntactic portability, instruction portability, metadata portability, behavioural portability and policy portability, and it distinguishes infrastructure, platform and application capability types. In practice, this means teams need to identify the application stack, its dependencies, its metadata, and the language or instruction support needed in the target environment.
6. Clause 9.5 limits application portability for application capabilities type cloud service
Clause 9.5 states that an application capabilities type cloud service typically offers a complete application operated by the CSP, so there is no porting of application code to or from that type of service. The meaningful portability topic there is data portability. For a CSC, that is an important procurement point: if code portability matters, this service type is not the one to choose for that use case.
7. Clause 10 defines cloud service switching around CSC digital assets
Clause 10 describes cloud service switching as moving provisioning from one CSP to another, and it focuses on the CSC’s digital assets, the constraints on switching and the responsibilities shared by CSC and CSPs. It highlights privacy, confidentiality, intellectual property, export restrictions and practical barriers. In practice, a switching plan must identify what the CSC can actually move, what must stay behind, and what needs to be agreed in the cloud service agreement.
8. Clauses 11 to 14 add multi-CSP, SLA and data-category considerations
Clauses 11 and 12 guide CSCs using services from multiple CSPs, or moving between an on-premises data centre and a CSP, by checking transport, syntax, semantics, behaviour and policy together. Clause 13 links interoperability and portability to Cloud Service Level Agreements (SLAs), using Service Level Objectives (SLOs) and Service Qualitative Objectives (SQOs) such as data location, deletion, notification and return of assets. Clause 14 points to standardized data categories, especially customer content data, when writing portability and interoperability requirements.
What terms does ISO/IEC 19941-1 define?
- Cloud Service Customer (CSC) - the party that uses cloud services and plans portability or switching of its data, applications or assets.
- Cloud Service Provider (CSP) - the party that provides the cloud service and may control service data, interfaces and operational conditions.
- Cloud Service Partner (CSN) - a cloud service partner, used here for parties acting as cloud service developers.
- Cloud service switching - the process whereby a CSC changes the provisioning of a cloud service from one CSP to another, or to an on-premises service in the case noted in the definition.
- Metadata - data that defines and describes other data, such as file type, permissions, ownership or application version information.
- CSC digital asset - a class of data objects that includes CSC data and some cloud service derived data needed for effective use of the cloud service.
- Observed derived data - cloud service derived data that records CSC interactions with a cloud service, such as logs or audit records.
- Inferred derived data - cloud service derived data created by the CSP through analysis of cloud service use, often as an estimate or interpretation.
- Idempotency - an operation feature meaning there is no additional effect if the operation is called more than once.
Who uses ISO/IEC 19941-1?
ISO/IEC 19941-1 is used by CSCs, CSPs and CSNs when they need a common way to discuss interoperability, portability and switching. It is also useful for cloud architects, migration teams, application developers, data owners, security and privacy teams, procurement staff and quality managers who need to compare services or write requirements.
The document is particularly relevant where an organization uses multiple CSPs, plans cloud migration, or wants to limit lock-in. Regulators and policy makers can also use its terminology when they are considering interoperability between cloud services.
What changed in ISO/IEC 19941-1 from the previous edition?
ISO/IEC 19941-1 is the first edition and it cancels and replaces ISO/IEC 19941:2017. The document says it has been technically revised.
The changes listed are:
- alignment with the ISO/IEC 22123 series, ISO/IEC 19086-1, ISO/IEC 19944-1 and ISO/IEC 5140
- references to the cross-cutting aspects and components identified in ISO/IEC 22123-1 and ISO/IEC 22123-3
- cloud service switching
- interoperability considerations when using cloud services from multiple CSPs
- portability considerations when using cloud services from multiple CSPs or between an on-premises data centre and a CSP
- cloud SLA aspects for interoperability and portability
- data categories for interoperability and portability
Which standards are used with ISO/IEC 19941-1?
| Standard | What it contributes |
|---|---|
| ISO/IEC 22123-1 | Vocabulary and base cloud-computing terms used throughout the document |
| ISO/IEC 22123-2 | Supporting cloud-computing concepts referenced in the background and interpretation of terms |
| ISO/IEC 22123-3 | Reference architecture and functional components reused in the functional diagrams |
| ISO/IEC 19086-1 | SLA framework, including the SLO and SQO concepts used in Clause 13 |
| ISO/IEC 19944-1 | Standardized data categories used in Clause 14 and in derived-data discussions |
| ISO/IEC 19944-2 | Guidance on using and extending the data categories from ISO/IEC 19944-1 |
| ISO/IEC 5140 | Concepts for multi-cloud and the use of multiple cloud services, used in Clauses 11 and 12 |
| ISO/IEC 27001 | Information security management requirements referenced in portability and policy discussions |
| ISO/IEC 27017 | Cloud security controls referenced for cloud-service handling of data |
| ISO/IEC 27018 | Guidance for protection of PII in public clouds acting as PII processors |
What does the ISO/IEC 19941-1 document contain?
ISO/IEC 19941-1 contains an overview, terminology and concepts section, followed by clause-by-clause treatment of interoperability, data portability, application portability, switching, multi-CSP use, SLA aspects and data categories. It includes facet models, functional component diagrams and tables that map portability types to cloud capability types.
The document also contains example consideration tables for data policy portability, cloud service derived data and application portability. Annex A and Annex B provide relationship matrices that show how interoperability, portability and switching support each other in practice.
Relations
- Revises
ISO/IEC 19941:2017 - Information technology — Cloud computing — Interoperability and portability - Effective Date
- 30-Sep-2023
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.
NYCE
Mexican standards and certification body.
Sponsored listings
Frequently Asked Questions
ISO/IEC 19941-1:2026 is a standard published by the International Organization for Standardization (ISO). Its full title is "Cloud computing — Interoperability and portability — Part 1: Overview, terminology and concepts". This standard covers: This document specifies cloud computing interoperability and portability types, the relationship and interactions between these two cross-cutting aspects of cloud computing and distributed platforms, as well as common terminology and concepts used to discuss interoperability and portability, particularly relating to cloud services. The goal of this document is to ensure that all parties involved in cloud computing, particularly cloud service customers (CSC), cloud service providers (CSP) and cloud service partners (CSN) acting as cloud service developers, have a common understanding of interoperability and portability for their specific needs, including switching service provision from one CSP to another. This common understanding helps to achieve interoperability and portability in cloud computing by establishing common terminology and concepts.
This document specifies cloud computing interoperability and portability types, the relationship and interactions between these two cross-cutting aspects of cloud computing and distributed platforms, as well as common terminology and concepts used to discuss interoperability and portability, particularly relating to cloud services. The goal of this document is to ensure that all parties involved in cloud computing, particularly cloud service customers (CSC), cloud service providers (CSP) and cloud service partners (CSN) acting as cloud service developers, have a common understanding of interoperability and portability for their specific needs, including switching service provision from one CSP to another. This common understanding helps to achieve interoperability and portability in cloud computing by establishing common terminology and concepts.
ISO/IEC 19941-1:2026 is classified under the following ICS (International Classification for Standards) categories: 01.040.35 - Information technology (Vocabularies); 35.210 - Cloud computing. The ICS classification helps identify the subject area and facilitates finding related standards.
ISO/IEC 19941-1:2026 has the following relationships with other standards: It is inter standard links to ISO/IEC 19941:2017. Understanding these relationships helps ensure you are using the most current and applicable version of the standard.
ISO/IEC 19941-1:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
International
Standard
ISO/IEC 19941-1
First edition
Cloud computing — Interoperability
2026-11
and portability —
Part 1:
Overview, terminology and concepts
Informatique en nuage — Interopérabilité et portabilité —
Partie 1: Vue d'ensemble, terminologie et concepts
Reference number
© ISO/IEC 2026
All rights reserved.
This ISO publication is protected by copyright and is owned by ISO and/or its licensors.
The content of this ISO publication is provided under licence, not sold. Use is subject to the applicable licence terms issued by ISO,
an ISO member body, or an authorized third-party distributor.
Except as required for implementation or expressly permitted by a separate licence, no part of this ISO publication may be
reproduced, distributed, modified, used, or made available in any form or by any means – electronic or mechanical, including
photocopying, scanning, recording, or posting on internal or external digital platforms.
Any use beyond the scope of the granted rights is prohibited and may result in legal action.
ISO copyright office
CP 401 • CH-1214 Vernier, Geneva
Phone: +41 22 749 01 11
Email: copyright@iso.org
Website: www.iso.org
Published in Switzerland
© ISO/IEC 2026 – All rights reserved
ii
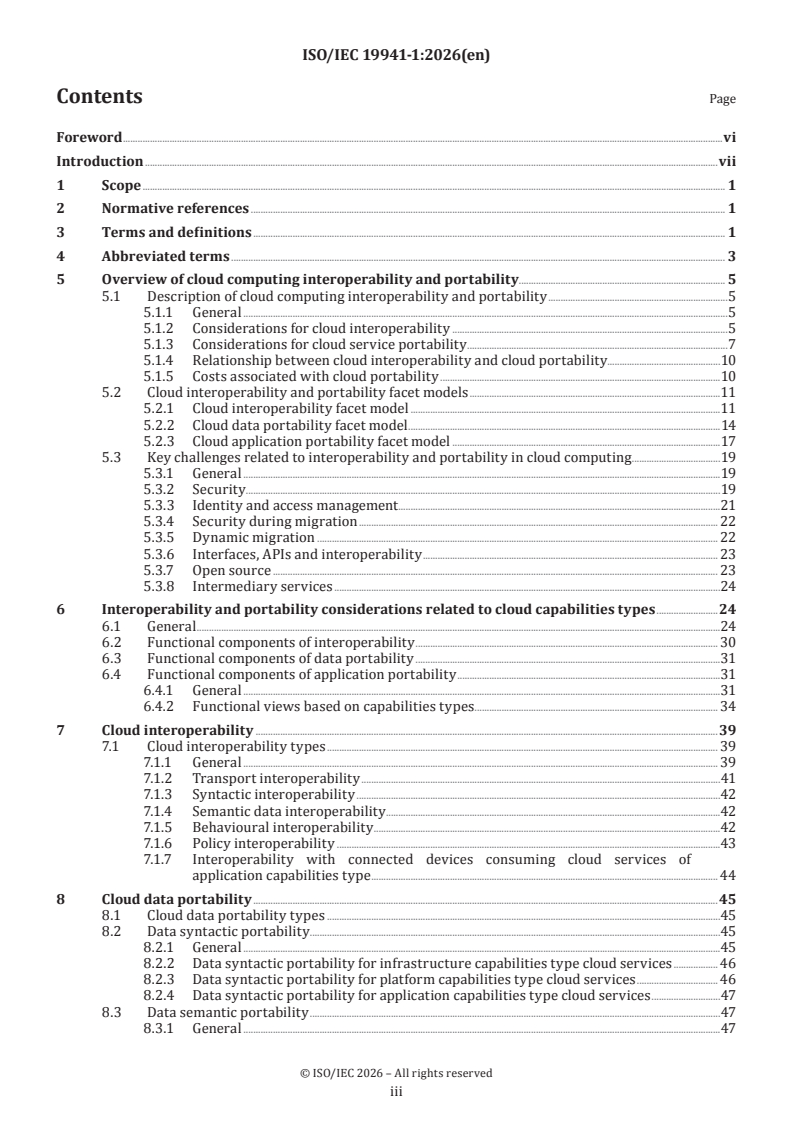
Contents Page
Foreword .vi
Introduction .vii
1 Scope . 1
2 Normative references . 1
3 Terms and definitions . 1
4 Abbreviated terms . 3
5 Overview of cloud computing interoperability and portability . 5
5.1 Description of cloud computing interoperability and portability .5
5.1.1 General .5
5.1.2 Considerations for cloud interoperability .5
5.1.3 Considerations for cloud service portability .7
5.1.4 Relationship between cloud interoperability and cloud portability.10
5.1.5 Costs associated with cloud portability .10
5.2 Cloud interoperability and portability facet models .11
5.2.1 Cloud interoperability facet model .11
5.2.2 Cloud data portability facet model .14
5.2.3 Cloud application portability facet model .17
5.3 Key challenges related to interoperability and portability in cloud computing .19
5.3.1 General .19
5.3.2 Security . . .19
5.3.3 Identity and access management .21
5.3.4 Security during migration . 22
5.3.5 Dynamic migration . 22
5.3.6 Interfaces, APIs and interoperability . 23
5.3.7 Open source . 23
5.3.8 Intermediary services .24
6 Interoperability and portability considerations related to cloud capabilities types .24
6.1 General .24
6.2 Functional components of interoperability . 30
6.3 Functional components of data portability .31
6.4 Functional components of application portability .31
6.4.1 General .31
6.4.2 Functional views based on capabilities types . . 34
7 Cloud interoperability .39
7.1 Cloud interoperability types . 39
7.1.1 General . 39
7.1.2 Transport interoperability .41
7.1.3 Syntactic interoperability .42
7.1.4 Semantic data interoperability .42
7.1.5 Behavioural interoperability .42
7.1.6 Policy interoperability .43
7.1.7 Interoperability with connected devices consuming cloud services of
application capabilities type . 44
8 Cloud data portability .45
8.1 Cloud data portability types .45
8.2 Data syntactic portability . .45
8.2.1 General .45
8.2.2 Data syntactic portability for infrastructure capabilities type cloud services . 46
8.2.3 Data syntactic portability for platform capabilities type cloud services . 46
8.2.4 Data syntactic portability for application capabilities type cloud services .47
8.3 Data semantic portability .47
8.3.1 General .47
© ISO/IEC 2026 – All rights reserved
iii
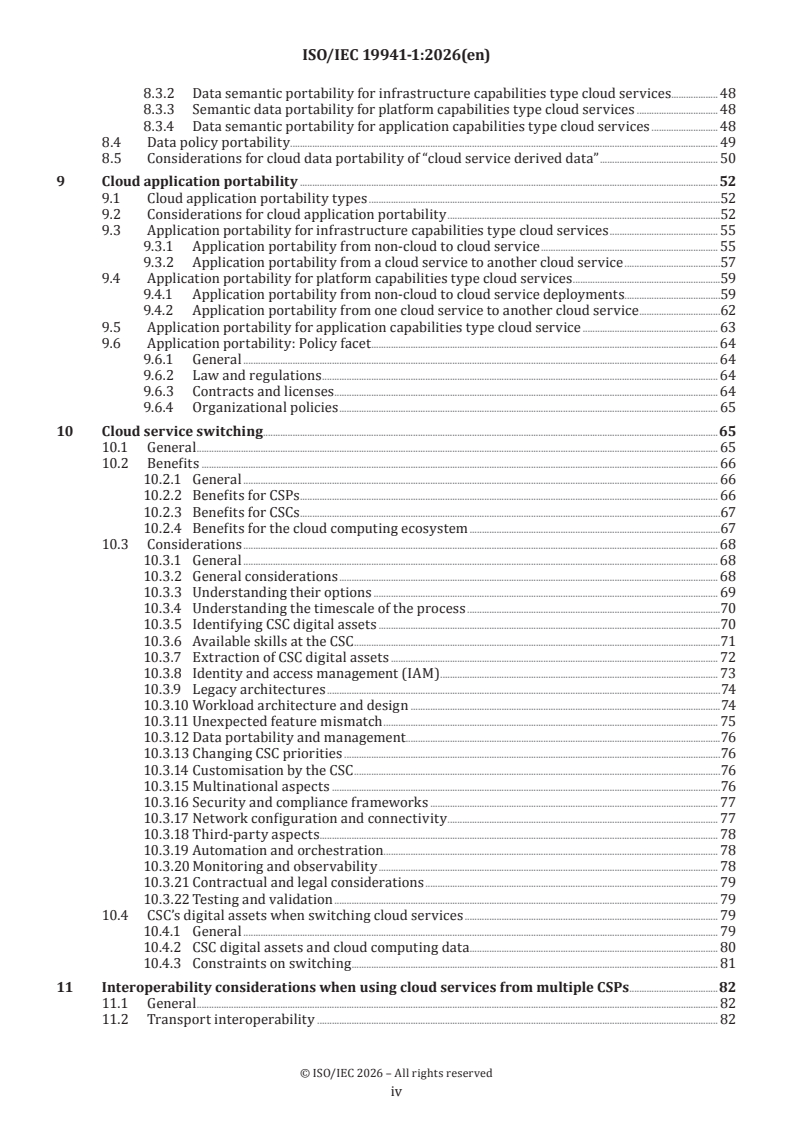
8.3.2 Data semantic portability for infrastructure capabilities type cloud services. 48
8.3.3 Semantic data portability for platform capabilities type cloud services . 48
8.3.4 Data semantic portability for application capabilities type cloud services . 48
8.4 Data policy portability . 49
8.5 Considerations for cloud data portability of “cloud service derived data” . 50
9 Cloud application portability .52
9.1 Cloud application portability types .52
9.2 Considerations for cloud application portability .52
9.3 Application portability for infrastructure capabilities type cloud services . 55
9.3.1 Application portability from non-cloud to cloud service . 55
9.3.2 Application portability from a cloud service to another cloud service .57
9.4 Application portability for platform capabilities type cloud services .59
9.4.1 Application portability from non-cloud to cloud service deployments.59
9.4.2 Application portability from one cloud service to another cloud service .62
9.5 Application portability for application capabilities type cloud service . 63
9.6 Application portability: Policy facet . . 64
9.6.1 General . 64
9.6.2 Law and regulations . 64
9.6.3 Contracts and licenses . 64
9.6.4 Organizational policies . 65
10 Cloud service switching . .65
10.1 General . 65
10.2 Benefits . 66
10.2.1 General . 66
10.2.2 Benefits for CSPs . 66
10.2.3 Benefits for CSCs .67
10.2.4 Benefits for the cloud computing ecosystem .67
10.3 Considerations . 68
10.3.1 General . 68
10.3.2 General considerations . 68
10.3.3 Understanding their options . 69
10.3.4 Understanding the timescale of the process .70
10.3.5 Identifying CSC digital assets .70
10.3.6 Available skills at the CSC .71
10.3.7 Extraction of CSC digital assets . 72
10.3.8 Identity and access management (IAM) . 73
10.3.9 Legacy architectures .74
10.3.10 Workload architecture and design .74
10.3.11 Unexpected feature mismatch . 75
10.3.12 Data portability and management . .76
10.3.13 Changing CSC priorities .76
10.3.14 Customisation by the CSC .76
10.3.15 Multinational aspects .76
10.3.16 Security and compliance frameworks . 77
10.3.17 Network configuration and connectivity . 77
10.3.18 Third-party aspects . . 78
10.3.19 Automation and orchestration . . 78
10.3.20 Monitoring and observability . 78
10.3.21 Contractual and legal considerations . 79
10.3.22 Testing and validation . 79
10.4 CSC’s digital assets when switching cloud services . 79
10.4.1 General . 79
10.4.2 CSC digital assets and cloud computing data. 80
10.4.3 Constraints on switching . 81
11 Interoperability considerations when using cloud services from multiple CSPs .82
11.1 General . 82
11.2 Transport interoperability . 82
© ISO/IEC 2026 – All rights reserved
iv
11.3 Syntactic and semantic interoperability . 82
11.4 Behaviour interoperability . 82
11.5 Policy interoperability . 82
12 Portability considerations when using cloud services from multiple CSPs or between an
on-prem data centre and a CSP .83
12.1 General . 83
12.2 Syntactic data portability . 83
12.3 Semantic data portability . 83
12.4 Policy portability . 83
13 Cloud SLA aspects for interoperability and portability .83
13.1 General . 83
13.2 Cloud SLOs, SQOs and components for interoperability and portability . 83
14 Data categories for interoperability and portability .84
Annex A (informative) Relationship between cloud interoperability, portability and switching .85
Annex B (informative) How cloud interoperability, portability and switching support each other .86
Bibliography .87
© ISO/IEC 2026 – All rights reserved
v
Foreword
ISO (the International Organization for Standardization) and IEC (the International Electrotechnical
Commission) form the specialized system for worldwide standardization. National bodies that are
members of ISO or IEC participate in the development of International Standards through technical
committees established by the respective organization to deal with particular fields of technical activity.
ISO and IEC technical committees collaborate in fields of mutual interest. Other international organizations,
governmental and non-governmental, in liaison with ISO and IEC, also take part in the work.
The procedures used to develop this document and those intended for its further maintenance are described
in the ISO/IEC Directives, Part 1. In particular, the different approval criteria needed for the different types
of documents should be noted. This document was drafted in accordance with the editorial rules of the ISO/
IEC Directives, Part 2 (see www.iso.org/directives or www.iec.ch/members_experts/refdocs).
ISO and IEC draw attention to the possibility that the implementation of this document may involve the
use of (a) patent(s). ISO and IEC take no position concerning the evidence, validity or applicability of any
claimed patent rights in respect thereof. As of the date of publication of this document, ISO and IEC had not
received notice of (a) patent(s) which may be required to implement this document. However, implementers
are cautioned that this may not represent the latest information, which may be obtained from the patent
database available at www.iso.org/patents and https://patents.iec.ch. ISO and IEC shall not be held
responsible for identifying any or all such patent rights.
Any trade name used in this document is information given for the convenience of users and does not
constitute an endorsement.
For an explanation of the voluntary nature of standards, the meaning of ISO specific terms and expressions
related to conformity assessment, as well as information about ISO's adherence to the World Trade
Organization (WTO) principles in the Technical Barriers to Trade (TBT) see www.iso.org/iso/foreword.html.
In the IEC, see www.iec.ch/understanding-standards.
This document was prepared by Joint Technical Committee ISO/IEC JTC 1, Information technology,
Subcommittee SC 38, Cloud computing and distributed platforms.
This first edition cancels and replaces the first edition (ISO/IEC 19941:2017), which has been technically
revised.
The main changes are as follows:
— alignment with the ISO/IEC 22123 series, ISO/IEC 19086-1, ISO/IEC 19944-1, ISO/IEC 5140 and in
particular, references to the cross-cutting aspects and components identified in ISO/IEC 22123-1 and
ISO/IEC 22123-3 respectively;
— cloud service switching;
— interoperability considerations when using cloud services from multiple CSPs;
— portability considerations when using cloud services from multiple CSPs or between an on-prem data
centre and a CSP;
— cloud SLA aspects for interoperability and portability;
— data categories for interoperability and portability.
A list of all parts in the ISO/IEC 19941 series can be found on the ISO and IEC websites.
Any feedback or questions on this document should be directed to the user’s national standards
body. A complete listing of these bodies can be found at www.iso.org/members.html and
www.iec.ch/national-committees.
© ISO/IEC 2026 – All rights reserved
vi
Introduction
This document establishes a common understanding of cloud computing interoperability and portability.
This document is related to other standards, including, ISO/IEC 22123 series, ISO/IEC 19086-1,
ISO/IEC 19944-1, ISO/IEC 5140 and in particular, references to the cross-cutting aspects and components
identified in ISO/IEC 22123-1 and ISO/IEC 22123-3 respectively.
Cloud computing is defined in ISO/IEC 22123-1 as a paradigm for enabling network access to a scalable and
elastic pool of 20 shareable physical or virtual resources with self-service provisioning and administration
[8] [9]
on demand. ISO/IEC 22123-1, ISO/IEC 22123-2 and ISO/IEC 22123-3 provide a starting point for the
understanding of different types of interoperability and portability, relationships with activities and roles
and cloud capabilities types. Interoperability, data portability and application portability are essential to the
use of cloud services. Interoperability enables interaction between non-cloud and cloud services and allows
composition of services. The goal of portability is to enable cloud service customers (CSCs) to move their
data or applications between non-cloud and one or more cloud services and between cloud services. The
benefits of interoperability include lower costs of integration and increasing the value of services through
enrichment or new functionality provided by composing cloud services. The benefits of portability include
greater efficiency by lowering the costs of migration. Both interoperability and portability offer more
choices to CSCs by limiting the effects of being locked into any cloud service or cloud service provider (CSP).
Interoperability and portability are important aspects of cloud computing, but there is no single way of
handling either capability. In new system development, incorporating interoperability and portability as part
of business and technical requirements, can be taken as a part of planning process and all design decisions
and development environment including application design and development are best implemented in a
vendor-neutral way. This approach can simplify portability and interoperability across services. If, on the
other hand, switching, porting or interoperability is desired during the operation and maintenance phase,
the CSC can require assistance of the incumbent CSP for migration, tools thereof and use of open interfaces
and APIs at the interface, immaterial of the internal interfaces used. Additionally, CSCs can use third party
tools and services.
ISO/IEC 22123-1 defines interoperability as the ability of two or more systems or applications to exchange
information and to mutually use the information that has been exchanged. In the context of cloud computing,
interoperability can be viewed as the capability of public cloud services, private cloud services and other CSC
systems to understand each other’s interfaces, configuration, forms of authentication and authorization, etc.
in order to cooperate and work with each other.
Regulators and policy makers are interested in the interoperability of cloud computing. Notably the EU
[18]
Data Act aims to achieve interoperability between cloud services that cover the same service type and in
terms of the ability to exchange data in order to perform their function.
Interoperability is a complex subject in the context of cloud computing because of the number of interactions
involved and the potential variations for each interaction. While interoperability and standards add
significant value and are advantageous to cloud computing, there are no comprehensive solutions. Many
existing IT standards contribute to enabling interoperability between CSC applications and cloud services
and between cloud services themselves. Various standards, including widely adopted industry specifications
and formally established standards, can contribute to interoperability. Using standards can be one way
to build interoperable cloud services. In addition, well-documented API specifications can support the
development of interoperable applications.
Cloud services designed with portability mechanisms can help CSCs move data between services using
defined policies standards, or documented formats, as this allows CSCs to move to a cloud service of another
CSP and also to drive integration of heterogeneous cloud services.
ISO/IEC 22123-1 defines data portability as the ability to easily transfer data from one system to another
without being required to re-enter data and application portability as the ability to migrate an application
from a source system to a target. Portability is relevant where CSCs aim to reduce the risk of vendor lock-in.
Therefore, in the context of cloud computing, portability can have multiple aspects depending on what is
being ported and which cloud services are involved. For portability, there are no specific requirements for
the source and target systems to be directly connected.
© ISO/IEC 2026 – All rights reserved
vii
Portability is not a binary property; applications can vary in the ease with which they can be ported
Applications can often be ported between cloud services when necessary resources and capabilities
are made available. The critical considerations for portability discussions are the porting cost, the risks
associated with the porting and how to control the costs and risks compared to the expected benefits.
© ISO/IEC 2026 – All rights reserved
viii
International Standard ISO/IEC 19941-1:2026(en)
Cloud computing — Interoperability and portability —
Part 1:
Overview, terminology and concepts
1 Scope
This document specifies cloud computing interoperability and portability types, the relationship and
interactions between these two cross-cutting aspects of cloud computing and distributed platforms, as well
as common terminology and concepts used to discuss interoperability and portability, particularly relating
to cloud services.
The goal of this document is to ensure that all parties involved in cloud computing, particularly cloud service
customers (CSC), cloud service providers (CSP) and cloud service partners (CSN) acting as cloud service
developers, have a common understanding of interoperability and portability for their specific needs,
including switching service provision from one CSP to another. This common understanding helps to achieve
interoperability and portability in cloud computing by establishing common terminology and concepts.
2 Normative references
The following documents are referred to in the text in such a way that some or all of their content constitutes
requirements of this document. For dated references, only the edition cited applies. For undated references,
the latest edition of the referenced document (including any amendments) applies.
ISO/IEC 22123-1, Information technology — Cloud computing — Part 1: Vocabulary
3 Terms and definitions
For the purposes of this document, the terms and definitions given in ISO/IEC 22123-1 and the following
apply.
ISO and IEC maintain terminology databases for use in standardization at the following addresses:
— ISO Online browsing platform: available at https:// www .iso .org/ obp
— IEC Electropedia: available at https:// www .electropedia .org/
3.1
cloud service switching
process whereby a CSC changes the provisioning of a cloud service from the current cloud service provider
to another cloud service provider
Note 1 to entry: To move the provisioning of a cloud service to an on-premises service, the other CSP can be the same
party as the CSC.
3.2
CSC-provided code
software code artefacts created by CSDs acting on the CSC’s behalf, that are designed to execute within a
cloud service to meet the needs of the CSC
Note 1 to entry: Such code artefacts can be supplemented by data or metadata.
© ISO/IEC 2026 – All rights reserved
Note 2 to entry: The CSDs creating the code can be employees or contractors of the CSC, or of another organization
such as a vendor, partner, or contractor to the CSC.
[SOURCE: ISO/IEC TS 7339:2024, 3.2]
3.3
metadata
data that defines and describes other data
Note 1 to entry: Metadata can include many different kinds of attributes of the data it describes. Some metadata fields
are almost universal, such as date of creation and last change, type of file or object, permissions, and ownership. Other
metadata can be specific to the type of object, such as the camera settings of a digital image, the author’s name for a
document, the version of a code artefact, etc.
Note 2 to entry: Some metadata can be directly attached to (or embedded within) the data to which it relates and
will always move with it. Other metadata can be stored separately and associated with the data by reference or other
means.
[SOURCE: ISO/IEC TS 7339:2024, 3.3]
3.4
CSC digital asset
class of data objects that includes CSC data and a subset of cloud service derived data essential for the
effective use of the cloud service
Note 1 to entry: Examples of cloud service derived data that are part of CSC digital asset are configuration settings,
security and access and control rights management. Such cloud service derived data is sometimes referred to as CSC
metadata (3.3).
Note 2 to entry: Examples of cloud service derived data that are not part of CSC digital asset are those covered by the
intellectual property rights of others, or that constitute a trade secret of another party, or that can compromise the
security and integrity of the cloud service.
Note 3 to entry: CSPs and CSNs also have their own digital assets, (not defined in this document).
Note 4 to entry: CSC digital assets are in digital form, limited to that for which the CSC has control and is independent
from its contractual relationship with the CSP.
3.5
jurisdiction
geographical or corporate area over which a cloud computing policy extends
Note 1 to entry: In a government policy context this will generally be the geographical area over which the body
enacting the policy has legal authority either as government or as authorised regulator. However, in an enterprise or
government agency environment, the jurisdiction of a policy can cover a business function, department, agency, or
other organisational area of responsibility not tied to geography.
[SOURCE: ISO/IEC TR 22678:2019 3.2]
3.6
observed derived data
subset of cloud service derived data consisting of records of interactions that the CSC has had with a cloud
service
Note 1 to entry: Examples of observed derived data are service configurations, access logs, call logs, change records
and audit records.
3.7
inferred derived data
subset of cloud service derived data created by the CSP through analysis of the cloud service and its usage
Note 1 to entry: Inferred derived data is often a subjective and approximate estimate rather than an objectively
calculated derivative.
© ISO/IEC 2026 – All rights reserved
Note 2 to entry: Inferred derived data is often (though not exclusively) used to estimate CSC attributes, interests and
potential behaviours.
Note 3 to entry: Examples of using inferred derived data include product recommendations.
3.8
idempotency
idempotence
operation feature which means there is no additional effect if the operation is called more than once
Note 1 to entry: Idempotent operations are often used to design a Web-based system since it is hard to restrict
redundancy access.
[SOURCE: ISO/IEC TS 23029:2020, 3.2]
4 Abbreviated terms
ACL Access Control List
AI Artificial Intelligence
AMQP Advanced Message Queuing Protocol
API Application Programming Interface
ASCII American Standard Code for Information Interchange
ASN.1 Abstract Syntax Notation 1
BPEL Business Process Execution Language
BPML Business Process Management Language
CD Continuous Deployment
CI Continuous Integration
CPU Central Processing Unit
CRM Customer Relationship Management
CSA Cloud Service Agreement
CSC Cloud Service Customer
CSD Cloud Service Developer
CSN Cloud Service Partner
CSP Cloud Service Provider
CSU Cloud Service User
CSV Comma-separated Values
DSP Data Space Protocol
EC European Commission
ERP Enterprise Resource Planning
© ISO/IEC 2026 – All rights reserved
ESB Enterprise Service Bus
EU European Union
FIPS Federal Information Processing Standard
GDPR General Data Protection Regulation (EU)
GPU Graphics Processing Unit
HCM Human Capital Management
HTTP Hyper Text Transfer Protocol
HTTPS Hypertext Transfer Protocol Secure
IaaS Infrastructure as a Service
IaC Infrastructure as Code
IAM Identity and Access Management
ICT Information & Communication Technology
IDAM Identity and Access Management
IDaaS Identity as a Service
IoT Internet of Things
IP Internet Protocol
IT Information Technology
JPEG Joint Photographic Experts Group
JSON JavaScript Object Notation
LCIM Levels of Conceptual Interoperability Model
MIME Multipurpose Internet Mail Extensions
MQTT Message Queuing Telemetry Transport
OVF Open Virtualization Format
OWL Web Ontology Language
PaaS Platform as a Service
PCI-DSS Payment Card Industry – Data Security Standard
PII Personally identifiable information
RDF Resource Description Framework
REST Representational State Transfer
SaaS Software as a Service
SAML Security Assertion Markup Language
© ISO/IEC 2026 – All rights reserved
SDK Software Development Kit
SLA Service Level Agreement
SLO Service Level Objective
SOAP Simple Object Access Protocol
SPARQL SPARQL Protocol and RDF Query Language
SQO Service Qualitative Objective
SSO Single Sign-On
TAR Tape Archive
TCK Technology Compatibility Kit
TCP Transmission Control Protocol
TLS Transport Layer Security
UML Unified Modeling Language
VM Virtual Machine
VPN Virtual Private Network
XML eXtensible Markup Language
YAML Yet Another Mark-Up Language
5 Overview of cloud computing interoperability and portability
5.1 Description of cloud computing interoperability and portability
5.1.1 General
This clause provides an overview and models (known as “facet models”; refer to 5.2.1, 5.2.2 and 5.2.3 for
details) for cloud interoperability, cloud data portability and cloud application portability. There are various
perspectives of interoperability and portability that need to be considered. These perspectives are called
“facets”.
Interoperability and portability in cloud computing involve interactions affected by technological,
information and human aspects. Portability in this document includes both data portability and application
portability. Interoperability and portability related challenges can increase in complexity as systems grow
more interconnected. In cloud computing environments with internationally interconnected systems, the
complexities also include matters of corporate policy, regulation and laws of applicable jurisdictions.
For information on cloud service switching, see Clause 10.
5.1.2 Considerations for cloud interoperability
ISO/IEC 22123-1 defines interoperability as “the ability for two or more systems or applications to exchange
information and mutually use the information that has been exchanged”. In the context of cloud computing,
interoperability is further described as a cross-cutting aspect providing the ability for a CSC’s on-premises
system to interact with a cloud service and exchange information according to a prescribed method and
[8]
obtain predictable results (see ISO/IEC 22123-2:2023, 7.5 ). Interoperability also includes the ability
[9]
for one cloud service to interact with other cloud services (see ISO/IEC 22123-3:2023, 8.3.4 ). Figure 1
illustrates that cloud interoperability takes place both between a CSC's application and cloud services (A)
© ISO/IEC 2026 – All rights reserved
and also between cloud services (B). There are typically multiple interactions involved in both of these
cases, as indicated by the multiple arrows. The interactions can be for different services or for multiple
instances of the same cloud service. In Figure 1 the arrows indicate that the information to be exchanged is
bi-directional, with either end able to initiate the interaction
Key
A application to/from cloud service
B cloud service to/from cloud service
Figure 1 — High-level view of cloud interoperability
NOTE 1 Figure 1 illustrates basic interaction styles only. Other configurations, such as using Cloud 1 as a relay or
intermediary for indirect interactions between the CSC application and Cloud 2, are possible.
NOTE 2 Interoperability in cloud computing has multi-faceted requirements that demand consideration, such
as clearly defined IT capabilities and interoperability requirements, realistic expectations, flexibility in approach,
commitment of necessary resources, informed decision making, a long-term perspective and active participation
...