

ISO 15801:2026
(Main)Document management — Electronically stored information — Requirements and guidance for trustworthiness and reliability
- Abstract
This document specifies requirements for and guidance on the implementation and operation of processes and systems to manage, store and provide access to electronically stored information (ESI) in a trustworthy and reliable manner. Such ESI can be of any type, including “page based” information, information in databases and audio/video information. This document is intended for any organization that uses processes and systems to store trustworthy ESI over time. Such processes and systems incorporate policies, procedures, technology and audit requirements that ensure that trustworthiness of the ESI is maintained. This document does not cover processes and systems used to evaluate whether ESI can be considered trustworthy before it is stored or imported into the system. However, it can be used to demonstrate that, once the electronic information is stored, output from the system will be a true and accurate reproduction of the ESI.
- Status
- Published
- Publication Date
- 18-May-2026
- Technical Committee
- ISO/TC 171/SC 1 - Quality, preservation and integrity of information
- Drafting Committee
- ISO/TC 171/SC 1 - Quality, preservation and integrity of information
- Current Stage
- 6060 - International Standard published
- Start Date
- 19-May-2026
- Due Date
- 10-Aug-2026
- Completion Date
- 19-May-2026
ISO 15801:2026 is an International Standard from ISO for organizations that manage electronically stored information (ESI). It specifies requirements and guidance for processes and systems that store, transfer, preserve and provide access to ESI in a trustworthy and reliable way, so the output can be relied on as a true and accurate reproduction once the information is stored.
What does ISO 15801:2026 specify?
ISO 15801:2026 specifies how an organization sets up and runs processes and systems for ESI so that trustworthiness and reliability are maintained over time. The document is aimed at any organization that stores ESI for later use, including page-based information, database content and audio/video material.
ISO 15801:2026 also states what is outside its scope: it does not cover the separate decision of whether ESI is trustworthy before it is stored or imported into the system. The document is organized into clauses 1 to 7, followed by a bibliography. Clause 4 covers processes and systems, Clause 5 covers roles and responsibilities, Clause 6 covers the business environment, and Clause 7 covers operational procedures.
What are the key requirements of ISO 15801:2026?
ISO 15801:2026 builds trust in ESI by requiring organizations to define scope, assign responsibility, control capture and transfer, and keep evidence of what happened to the information. In practice, the standard is about being able to show that stored ESI has been managed in a controlled way from creation through disposal.
Scope and risk-based planning - Clause 4.2 and 4.3 require the organization to define the scope of the ESI system and use risk management to set the related requirements. The organization should group ESI into information types and base policy statements on those types. This matters because not every document or data set needs the same level of control.
Policies for the full lifecycle - Clause 4.6 and 4.7 require policy coverage for storage, transfer and final disposition of ESI, and the policy must be maintained, communicated and resourced. The policy statements also need to address identity, authority, copyright protection and information security. In practice, this gives staff a single set of rules for how ESI is handled from start to finish.
Clear roles and accountability - Clause 5 requires documented roles for organizational management, information stewards, system managers and ESI users. The organization must appoint accountable people for policy, stewardship and system operation. That matters because trustworthiness depends on named people who can make decisions, monitor issues and act when something goes wrong.
Controlled creation, import and capture - Clause 7.2 and 7.3 require procedures for creating and importing ESI, including format conversion, metadata, audit trail records and, where relevant, voice, audio and video material. When ESI comes from outside the organization, the organization should confirm that it has not been altered and that the origin is genuine. This is what lets later users rely on the stored version.
Special handling for complex information - Clause 7.4 to 7.12 address workflow systems, scanning, information extraction, metadata capture, self-modifying files, compound documents, structured databases, big data, IoT and blockchain and distributed ledger technologies. The organization is expected to document how these sources are handled, where information loss can occur, and what checks or mitigations are used. This matters because these formats can hide changes or lose context more easily than simple documents.
Storage, migration, formats and compression - Clause 7.14 requires suitable storage technology, migration planning, approved file formats and controlled use of compression. The organization should choose storage that fits retention and access needs, keep ESI accessible over the storage period, and document any conversion or lossy compression. In practice, this is how organizations avoid losing readability or evidential value over time.
Transfer, identity, security and recovery - Clause 7.15, 7.17, 7.18 and 7.20 require controlled transfer procedures, authenticated output, identity controls, access control, encryption, digital signatures or digital seals, backup and recovery, and business continuity planning. These controls matter when ESI is sent between systems or later presented as evidence, because the organization has to show who sent it, who received it and whether it was protected along the way.
Retention, redaction, disposal and testing - Clause 7.19, 7.22 and 7.23 require retention schedules, redaction procedures, controlled disposal, external service provider controls and regular system testing. The organization must be able to suspend disposal for legal holds, keep audit trail evidence, and test the whole system against business requirements. This is what supports long-term defensibility of stored ESI.
What terms does ISO 15801:2026 define?
ISO 15801:2026 defines the core vocabulary used throughout the standard.
- Digital seal - Data in electronic form attached to or linked with other data to show the origin and integrity of that data.
- Electronically stored information (ESI) - Information of any kind from any source whose existence is shown by storage on an electronic medium.
- Information type - A group of related information, such as invoices, financial documents, data sheets or correspondence.
- Trustworthiness - The ability to demonstrate authenticity, integrity and availability of ESI over time.
Who uses ISO 15801:2026?
ISO 15801:2026 is used by organizations that need to keep ESI reliable for business, compliance, legal or dispute resolution purposes. The introduction specifically points to managers and professionals in data, information, records, knowledge, digital preservation and e-discovery, as well as designers, vendors and operators of systems that create, receive, store, transmit, preserve and dispose of ESI.
Typical users include:
- governance, records and information managers
- compliance and legal teams
- system designers and vendors
- operators of document and information systems
- organizations that may need ESI as evidence in a dispute
What changed in ISO 15801:2026 from the previous edition?
ISO 15801:2026 is the first edition of ISO 15801 and cancels and replaces ISO/TR 15801:2017. The document states that the main change is the update from a Technical Report to an International Standard.
Which standards are used with ISO 15801:2026?
ISO 15801:2026 refers to several related standards that support its use.
- ISO 12651 (all parts) - Supplies the vocabulary for electronic document management.
- ISO 31000 - Provides general risk management guidance used when setting scope and requirements.
- ISO 4669-1 - Supports information classification, marking and handling.
- ISO/IEC 27001, ISO/IEC 27002 and ISO/IEC 27005 - Support information security management, controls and security risk analysis.
- ISO 12653 (all parts) - Provides test targets and procedures that can support scanner testing.
- ISO 14641 - Can be used with ISO 15801:2026 when preservation of electronic documents is being considered.
- ISO 14721 and ISO 19005-1 - Support long-term storage and preservation-oriented file formats.
- ISO 22301 - Supports business continuity planning.
- ISO/IEC 27038 and ISO/IEC 27040 - Support redaction and storage security.
- ISO/TS 24574 and ISO/TS 7538 - Relate to digital safe storage and disposition of records.
What does the ISO 15801:2026 document contain?
ISO 15801:2026 contains policy requirements, role definitions and operational procedures for managing ESI across its lifecycle. Clause 7 is the most detailed part and covers creation, importing, scanning, OCR/ICR and e-forms, metadata capture, version control, storage systems, transfer, indexing, authenticated output, identity, retention, redaction, disposal, security, external service provision and system testing.
The document also gives guidance on special cases such as structured databases, big data, blockchain and distributed ledger technologies, IoT, workflow systems and self-modifying files. These sections are useful when an organization needs to show that the ESI it retains still reflects what was originally received or created.
Many clauses point to audit trail records, retained procedures and documented decisions. In practice, the document is meant to support design, implementation, internal control, audit and later evidential use of ESI.
Relations
- Effective Date
- 13-May-2023
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.
NYCE
Mexican standards and certification body.
Sponsored listings
Frequently Asked Questions
ISO 15801:2026 is a standard published by the International Organization for Standardization (ISO). Its full title is "Document management — Electronically stored information — Requirements and guidance for trustworthiness and reliability". This standard covers: This document specifies requirements for and guidance on the implementation and operation of processes and systems to manage, store and provide access to electronically stored information (ESI) in a trustworthy and reliable manner. Such ESI can be of any type, including “page based” information, information in databases and audio/video information. This document is intended for any organization that uses processes and systems to store trustworthy ESI over time. Such processes and systems incorporate policies, procedures, technology and audit requirements that ensure that trustworthiness of the ESI is maintained. This document does not cover processes and systems used to evaluate whether ESI can be considered trustworthy before it is stored or imported into the system. However, it can be used to demonstrate that, once the electronic information is stored, output from the system will be a true and accurate reproduction of the ESI.
This document specifies requirements for and guidance on the implementation and operation of processes and systems to manage, store and provide access to electronically stored information (ESI) in a trustworthy and reliable manner. Such ESI can be of any type, including “page based” information, information in databases and audio/video information. This document is intended for any organization that uses processes and systems to store trustworthy ESI over time. Such processes and systems incorporate policies, procedures, technology and audit requirements that ensure that trustworthiness of the ESI is maintained. This document does not cover processes and systems used to evaluate whether ESI can be considered trustworthy before it is stored or imported into the system. However, it can be used to demonstrate that, once the electronic information is stored, output from the system will be a true and accurate reproduction of the ESI.
ISO 15801:2026 is classified under the following ICS (International Classification for Standards) categories: 35.240.30 - IT applications in information, documentation and publishing. The ICS classification helps identify the subject area and facilitates finding related standards.
ISO 15801:2026 has the following relationships with other standards: It is inter standard links to ISO/TR 15801:2017. Understanding these relationships helps ensure you are using the most current and applicable version of the standard.
ISO 15801:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
International
Standard
ISO 15801
First edition
Document management —
2026-05
Electronically stored information
— Requirements and guidance for
trustworthiness and reliability
Gestion documentaire — Informations stockées électroniquement
— Exigences et recommandations pour la fiabilité et la sécurité
Reference number
© ISO 2026
All rights reserved. Unless otherwise specified, or required in the context of its implementation, no part of this publication may
be reproduced or utilized otherwise in any form or by any means, electronic or mechanical, including photocopying, or posting on
the internet or an intranet, without prior written permission. Permission can be requested from either ISO at the address below
or ISO’s member body in the country of the requester.
ISO copyright office
CP 401 • Ch. de Blandonnet 8
CH-1214 Vernier, Geneva
Phone: +41 22 749 01 11
Email: copyright@iso.org
Website: www.iso.org
Published in Switzerland
ii
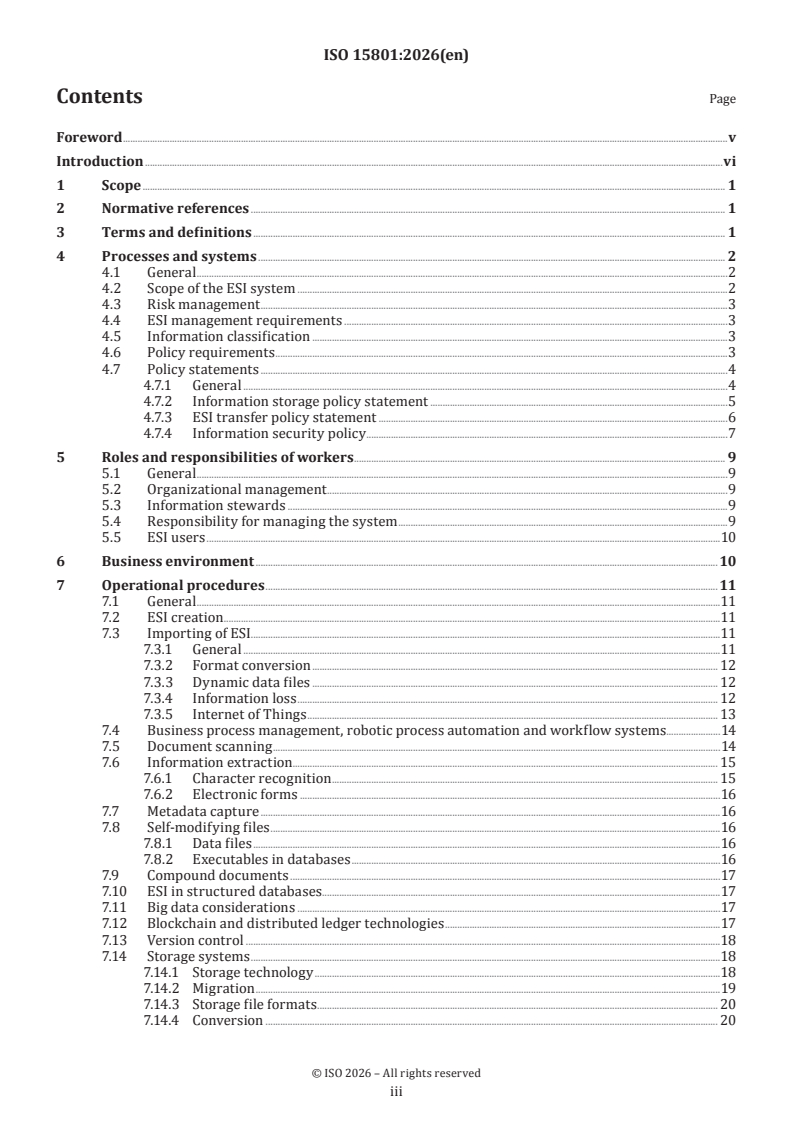
Contents Page
Foreword .v
Introduction .vi
1 Scope . 1
2 Normative references . 1
3 Terms and definitions . 1
4 Processes and systems . 2
4.1 General .2
4.2 Scope of the ESI system .2
4.3 Risk management .3
4.4 ESI management requirements .3
4.5 Information classification .3
4.6 Policy requirements .3
4.7 Policy statements .4
4.7.1 General .4
4.7.2 Information storage policy statement .5
4.7.3 ESI transfer policy statement .6
4.7.4 Information security policy .7
5 Roles and responsibilities of workers . 9
5.1 General .9
5.2 Organizational management .9
5.3 Information stewards .9
5.4 Responsibility for managing the system .9
5.5 ESI users .10
6 Business environment . 10
7 Operational procedures .11
7.1 General .11
7.2 ESI creation . .11
7.3 Importing of ESI.11
7.3.1 General .11
7.3.2 Format conversion . 12
7.3.3 Dynamic data files . 12
7.3.4 Information loss . 12
7.3.5 Internet of Things . 13
7.4 Business process management, robotic process automation and workflow systems.14
7.5 Document scanning .14
7.6 Information extraction. 15
7.6.1 Character recognition . 15
7.6.2 Electronic forms .16
7.7 Metadata capture .16
7.8 Self-modifying files .16
7.8.1 Data files .16
7.8.2 Executables in databases .16
7.9 Compound documents .17
7.10 ESI in structured databases.17
7.11 Big data considerations .17
7.12 Blockchain and distributed ledger technologies .17
7.13 Version control .18
7.14 Storage systems .18
7.14.1 Storage technology .18
7.14.2 Migration .19
7.14.3 Storage file formats . . 20
7.14.4 Conversion . 20
iii
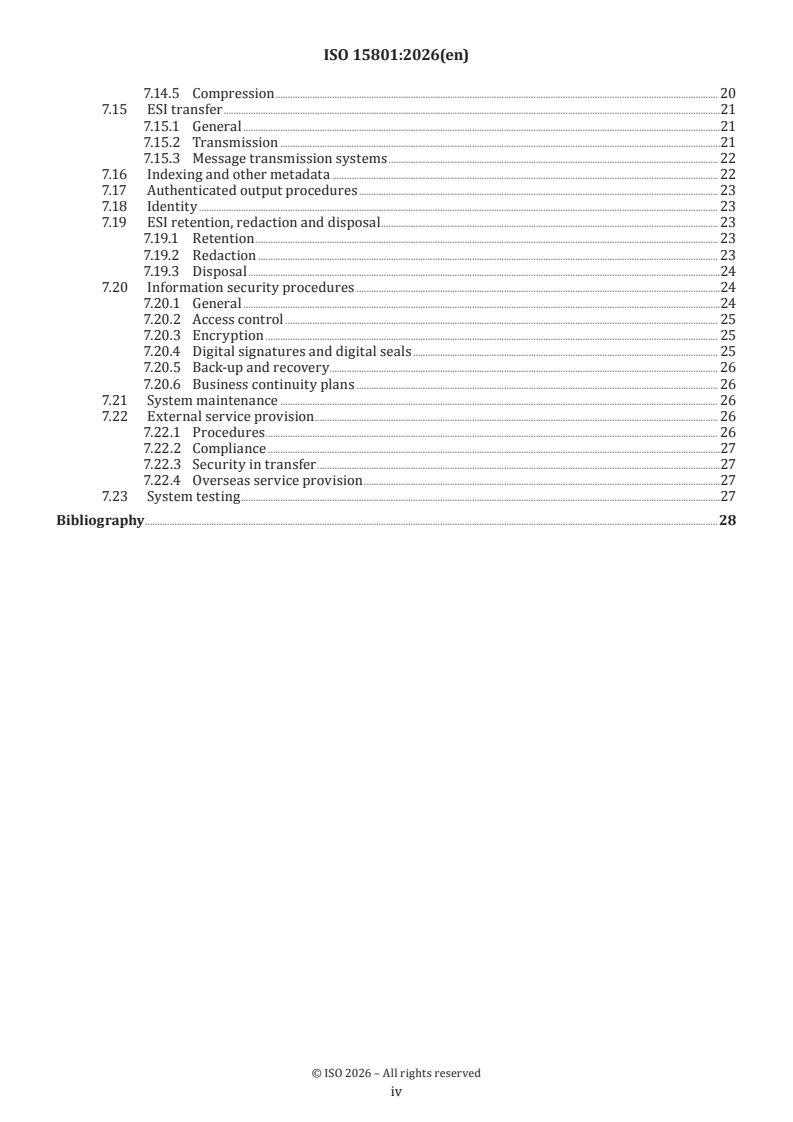
7.14.5 Compression . 20
7.15 ESI transfer .21
7.15.1 General .21
7.15.2 Transmission .21
7.15.3 Message transmission systems . 22
7.16 Indexing and other metadata . 22
7.17 Authenticated output procedures . 23
7.18 Identity . 23
7.19 ESI retention, redaction and disposal . 23
7.19.1 Retention . 23
7.19.2 Redaction . 23
7.19.3 Disposal .24
7.20 Information security procedures .24
7.20.1 General .24
7.20.2 Access control . 25
7.20.3 Encryption . 25
7.20.4 Digital signatures and digital seals . 25
7.20.5 Back-up and recovery . . 26
7.20.6 Business continuity plans . 26
7.21 System maintenance . 26
7.22 External service provision . 26
7.22.1 Procedures . 26
7.22.2 Compliance .27
7.22.3 Security in transfer .27
7.22.4 Overseas service provision .27
7.23 System testing .27
Bibliography .28
iv
Foreword
ISO (the International Organization for Standardization) is a worldwide federation of national standards
bodies (ISO member bodies). The work of preparing International Standards is normally carried out through
ISO technical committees. Each member body interested in a subject for which a technical committee
has been established has the right to be represented on that committee. International organizations,
governmental and non-governmental, in liaison with ISO, also take part in the work. ISO collaborates closely
with the International Electrotechnical Commission (IEC) on all matters of electrotechnical standardization.
The procedures used to develop this document and those intended for its further maintenance are described
in the ISO/IEC Directives, Part 1. In particular, the different approval criteria needed for the different types
of ISO document should be noted. This document was drafted in accordance with the editorial rules of the
ISO/IEC Directives, Part 2 (see www.iso.org/directives).
ISO draws attention to the possibility that the implementation of this document may involve the use of (a)
patent(s). ISO takes no position concerning the evidence, validity or applicability of any claimed patent
rights in respect thereof. As of the date of publication of this document, ISO had not received notice of (a)
patent(s) which may be required to implement this document. However, implementers are cautioned that
this may not represent the latest information, which may be obtained from the patent database available at
www.iso.org/patents. ISO shall not be held responsible for identifying any or all such patent rights.
Any trade name used in this document is information given for the convenience of users and does not
constitute an endorsement.
For an explanation of the voluntary nature of standards, the meaning of ISO specific terms and expressions
related to conformity assessment, as well as information about ISO's adherence to the World Trade
Organization (WTO) principles in the Technical Barriers to Trade (TBT), see www.iso.org/iso/foreword.html.
This document was prepared by Technical Committee ISO/TC 171, Document management applications,
Subcommittee SC 1, Quality, preservation and integrity of information.
This first edition of ISO 15801 cancels and replaces ISO/TR 15801:2017, which has been technically revised.
The main changes are as follows:
— update from a Technical Report to an International Standard.
Any feedback or questions on this document should be directed to the user’s national standards body. A
complete listing of these bodies can be found at www.iso.org/members.html.
v
Introduction
Information is an organizational asset that should be appropriately managed throughout its lifecycle.
Ensuring that the organization is able to demonstrate the trustworthiness and reliability of electronically
stored information (ESI) is a key consideration. Failure to do so can result in non-compliance, loss of
evidential value for information used in business, dispute resolution or legal proceedings.
This document specifies how ESI can be managed by an organization using processes and systems, thus
enabling the organization to demonstrate the trustworthiness and reliability of the ESI throughout its
lifecycle.
NOTE These processes and systems are sometimes referred to as an information management system.
This document is intended for use in business, compliance, legal or other dispute resolution purposes, where
the retained ESI needs to be relied upon to be exactly what it purports to be. This document is intended to
be used by:
— managers and professionals involved in management and governance of data, information, records,
knowledge, digital preservation or e-discovery;
— designers, vendors and operators of the systems and processes that create, receive, store, transmit,
preserve and dispose of ESI.
It would also benefit the academic community and general public.
Where an organization implements the requirements in this document, it is anticipated that the weight of
evidence of ESI managed by the systems and processes will be maximized by ensuring its trustworthiness
and reliability. This is likely to reduce the effort and cost involved in dispute resolution, as the resolution
process will place less emphasis on the trustworthiness or reliability of disclosed ESI. It is also likely that
organizations will minimize their risks concerning the credibility of ESI retained for the long term.
ESI originates from many sources. This document covers ESI in any form, from traditional scanned images,
word-processed documents and spreadsheets to the more modern forms which include email, web content,
instant messages, computer-aided design (CAD) drawing files, blogs, wikis, audio files, pictures and video.
Also included is ESI stored in databases, Internet of Things (IoT) systems, distributed ledger technology
(including blockchain systems) and other storage systems, including the use of cloud storage.
When ESI preservation is considered, the requirements of ISO 14641 can be used in conjunction with this
document.
vi
International Standard ISO 15801:2026(en)
Document management — Electronically stored information
— Requirements and guidance for trustworthiness and
reliability
1 Scope
This document specifies requirements for and guidance on the implementation and operation of processes
and systems to manage, store and provide access to electronically stored information (ESI) in a trustworthy
and reliable manner. Such ESI can be of any type, including “page based” information, information in
databases and audio/video information.
This document is intended for any organization that uses processes and systems to store trustworthy ESI
over time. Such processes and systems incorporate policies, procedures, technology and audit requirements
that ensure that trustworthiness of the ESI is maintained.
This document does not cover processes and systems used to evaluate whether ESI can be considered
trustworthy before it is stored or imported into the system. However, it can be used to demonstrate that,
once the electronic information is stored, output from the system will be a true and accurate reproduction
of the ESI.
2 Normative references
The following documents are referred to in the text in such a way that some or all of their content constitutes
requirements of this document. For dated references, only the edition cited applies. For undated references,
the latest edition of the referenced document (including any amendments) applies.
ISO 12651 (all parts), Electronic document management — Vocabulary
3 Terms and definitions
For the purposes of this document, the terms and definitions given in ISO 12651-1, ISO 12651-2 and the
following apply.
ISO and IEC maintain terminology databases for use in standardization at the following addresses:
— ISO Online browsing platform: available at https:// www .iso .org/ obp
— IEC Electropedia: available at https:// www .electropedia .org/
3.1
digital seal
data in electronic form which is attached to or logically associated with other data in electronic form to
inform on the latter’s origin and integrity
3.2
electronically stored information
ESI
information of any kind and from any source, whose temporal existence is evidenced by being stored in or
on any electronic medium
Note 1 to entry: ESI includes traditional email, memos, letters, spreadsheets, databases, office documents,
presentations and other electronic formats commonly found on a computer. ESI also includes system, application and
file-associated metadata such as timestamps, revision history, file type, etc.
Note 2 to entry: Electronic medium can take the form of, but is not limited to, storage devices and storage elements.
3.3
information type
groups of related information
Note 1 to entry: In specific applications, “groups” can be identified as “sets”, “files”, “collections” or other similar terms.
EXAMPLE Invoices, financial documents, data sheets, correspondence.
3.4
trustworthiness
ability to demonstrate authenticity, integrity and availability of electronically stored information over time
4 Processes and systems
4.1 General
Information is one of the most important assets that any organization has at its disposal. Everything an
organization does involves using information in some way. The quantity of information can be vast and
there are many different ways of representing and storing it. The value of information used and the manner
in which it is applied and moved within and between organizations can determine the success or failure of
those organizations.
Information, like any other asset, should be classified, structured, validated, valued, secured, monitored,
measured and managed efficiently and effectively.
Where processes and systems manage ESI that may be used as evidence in any legal or business process, the
appropriate legal advisors should be consulted to ensure that compliance with relevant legal or regulatory
requirements is demonstrable. As legal and regulatory requirements vary from country to country (and
sometimes within a country), legal advice should cover all relevant jurisdictions.
4.2 Scope of the ESI system
The organization shall determine the scope and requirements for the ESI system with respect to
trustworthiness and reliability.
All ESI used by an organization that is within the scope of the ESI system should be classified into information
types. This classification should be used in the creation of policy statement(s).
NOTE For further information on classification, see the ISO 4669 series.
It is possible that the policy statements described in 4.6 do not cover all the different types of ESI that the
organization uses. The ESI that will be included in its scope should be identified and grouped into types, with
the policy for all ESI within a type being consistent. Where a retention schedule and disposal procedures
(see 7.19) exist, it can be appropriate to use the same ESI type groups.
When determining this scope, the organization should consider:
a) the results of the risk management process (see 4.3);
b) the requirements for ESI management (see 4.4); and
c) information classification systems in use (see 4.5).
The scope should be available as part of the policy statement(s).
In many organizations, the trustworthiness and reliability of ESI can only be of importance to part of the
overall ESI asset. Individual ESI assets should be identified and a decision should be taken as to whether
each should be included within the scope of the related policy.
4.3 Risk management
A risk management process shall be used to identify the scope and requirements that are relevant to the
trustworthiness and reliability of ESI.
NOTE 1 The scope and requirements can typically cover the following:
a) the size and complexity of the organization;
b) the level of business risk attached to the inability to demonstrate trustworthiness and reliability of ESI;
c) drivers for business efficiency improvements;
d) specific stakeholder requirements; and
e) the existing technology and infrastructure systems.
NOTE 2 The risk management processes defined in ISO 31000 can be appropriate.
NOTE 3 In order to define and assess the security risks to which ESI is exposed, it can be useful to use a risk analysis
method such as that defined in ISO 27005.
4.4 ESI management requirements
When determining ESI management requirements, any applicable legal and regulatory requirements, duty
of care expectations, contractual obligations, business requirements and ESI stewardship throughout the
ESI lifecycle shall be taken into account. These requirements should cover:
a) stakeholders that are relevant to the trustworthiness and reliability of ESI;
b) the requirements of these stakeholders relevant to that ESI; and
c) the requirements for information stewardship within the organization.
The requirements of each stakeholder should be taken into consideration when producing policy statements
(see 4.6).
Information stewardship should be managed by the identification of information asset owners who are
typically those responsible for the processes that manage the ESI asset in question.
4.5 Information classification
In some applications, it is appropriate to implement an ESI classification system. Typically, ESI classification
systems are used to indicate the accessibility of particular documents to workers and other individuals.
In government and other public bodies, this is often indicated by the use of security labels such as “top
secret”, “classified” or “publicly available”. In the private sector, ESI classification schemes can be aligned to
departmental requirements (such as accounts, credit control or customer services).
The organization shall determine whether to implement an information classification, marking and handling
scheme (ICMH) and, if it is decided not to implement an ICMH scheme, the organization shall document the
decision and rationale.
NOTE For further information on information classification, marking and handling (ICMH), see ISO 4669-1.
In the event of the organization deciding to implement an ICMH scheme, the structure and operation of that
scheme shall be included in the organizational documentation (see 7.1) and shall be retained for at least as
long as any ESI utilizing the ICMH scheme is retained.
4.6 Policy requirements
This clause describes documentation that states the organization’s policy for the management of ESI.
Additionally, this clause provides guidance to organizations with respect to the level of documentation
required to enable an organization to clearly establish how the ESI contained in a trusted system is reliable,
accurate and trustworthy. Availability of this documentation can also be used to demonstrate that ESI
management is part of normal business procedures.
The organization shall set a clear policy direction and demonstrate support for, and commitment to, the
management of ESI that is within the scope of the system through the issue and maintenance of a policy
covering the management of ESI.
The policy shall address the whole lifecycle of the referenced ESI and shall identify the role of the information
steward(s) responsible for the referenced ESI at each stage of the lifecycle.
NOTE 1 The information stewardship can be transferred between individuals at different stages in the lifecycle
of an ESI asset. This continuity of stewardship is important to demonstrate an unbroken chain of management and
accountability throughout the life of the ESI.
The policy shall cover:
a) the storage of electronic information (see 4.7.2);
b) the transfer of ESI between systems (see 4.7.3); and
c) the final disposition of electronic information
The policy shall be linked to or combined with the information security policy of the organization (see 4.7.4).
NOTE 2 In some organizations, this is called an information risk management policy.
The policy shall be published and communicated to all appropriate workers.
The policy shall have a custodian, responsible for its maintenance and review in accordance with the
approved review procedure of the organization.
The policy shall be integrated into the processes of the organization.
Sufficient resource shall be available to implement the policy and to ensure the relevant outcomes are
achieved and, where appropriate, improved.
The policy shall be documented in one or more policy statements.
4.7 Policy statements
4.7.1 General
A procedure shall be established to ensure that the policies covering the management of ESI are reviewed at
regular intervals, and when any significant changes occur to the appropriate business, legal or regulatory
environment.
NOTE The review period is typically the same as the normal procedural audit cycle within the organization, e.g.
occurring annually or in the event of major changes to the system.
The policy statements should set out guidelines for the appropriate application of an electronic identity
for each document type. These statements should include the organizational requirements for identity,
authority and copyright protection.
The underlying issue with these items is the requirement to understand the significance of an electronic
identity attached to a document. If this electronic identity is always attached to someone within the same
organization, it is significantly less complex than between organizations because the organization can set
its own rules. For all inter-organizational documents controlled with electronic signatures or copyright
protection, the recipient organization shall be capable of understanding the significance of what is
communicated to it, recognizing, implementing and utilizing the relevant controls.
This document also specifies the contents of an information security policy within which the information
storage policy operates. The information security policy statement should document the level and rigour of
protection required, detailing the requirements for each document type.
Where there is a requirement, the policy statements should describe the degree of security required, for
example, some documents are not as significant as others and proof of the identity of the signatories is of
less importance, for instance, an internal memo as opposed to a contractual commitment.
Approved policy statements should be retained in compliance with the retention schedule (see 7.19).
4.7.2 Information storage policy statement
4.7.2.1 Structure
The information storage policy statement shall state the commitment of the management to, and approach
for, the use of electronic systems in the storage of ESI over time in a controlled manner, taking account of the
need to preserve the trustworthiness and reliability of the ESI.
Availability of this documentation should, when combined with appropriate proof of compliance,
demonstrate (e.g. to a court of law) that responsible information storage is part of the normal business
practice of the organization.
The information storage policy statement should be approved by the organization and should be reviewed
for relevance and content at regular intervals. The frequency for review should be appropriate to the
application.
The policy statement shall, as a minimum, include the following elements or, where applicable, reference
separate documentation on:
a) the scope of the policy (see 4.7.2.2);
b) the application of any relevant information classification to ESI (see 4.5);
c) the implementation of various international and national standards and industry-related requirements
and guidelines;
d) the compliance with the policy of the organization for capture and retention of information;
e) the definition and allocation of roles and responsibilities (see Clause 5);
f) any consultations that the organization is required to undertake (see Clause 6);
g) the use of the appropriate ESI storage technology (see 7.14.1);
h) the use of the appropriate ESI file formats (see 7.14.3);
i) the use of compression technology (see 7.14.5);
j) the management of the linking of electronic identity to ESI (see 7.18);
k) the capture, retention and disposal of ESI, including the management of temporary halts to the
destruction of specific ESI (see 7.19);
l) the use of encryption technology (see 7.20.3).
4.7.2.2 Scope
Where formal records management procedures are implemented, ESI types will generally be used in
classification schemes (file plans) or taxonomies. Where this is the case, the same file grouping and naming
conventions should be used.
NOTE ESI types can be specified by reference to application (e.g. financial projections, invoices or customer
address list) or by reference to generic group (e.g. accounting data, customer documents or manufacturing documents).
All applicable ESI types should be included in the policy statements.
An alternative to this approach of including only identified ESI types in the policy scope can be adopted,
since there is a risk that the organization will be required to produce some of its ESI assets in the event of
a dispute. The organization should consider whether it needs to have any ESI that is totally unmanaged,
including the ESI that is regarded as of very low value to the organization.
In this case, it is worth considering whether the policy scope should include a “default” ESI type (with
associated policy and policy implementation and compliance requirements) as well as the explicitly
identified ESI types. ESI outside the scope of the explicitly identified types should be managed according to
the default.
4.7.2.3 Standards related to ESI management
Frequently, business benefits can be achieved by complying with relevant national or international
standards, codes of practice or other guidance materials. The policy statements should state whether all or
specific parts of any such publication(s) should be complied with.
NOTE ISO/IEC 27000, ISO/IEC 27001, ISO/IEC 27002 and ISO/IEC 27005 are the reference documents for
information security management.
Where the organization operates a quality management system (e.g. ISO 9001), whose scope includes part or
all of the processes and systems related to the management of ESI within the scope of compliance, then all
documentation that this document requires should be included in the quality management system.
Where information classification systems are used within the system, it is recommended to refer to
ISO 4669-1 for relevant requirements for the subsequent marking and handling of the classified information.
4.7.3 ESI transfer policy statement
There are many forms of technologies and procedures that can be used for ESI transfers. The ESI transfer
policy statement should give guidelines on:
— the type of transfer technology to use in particular circumstances;
— the content and layout of unstructured transfers;
— the identification of the appropriate systems to be used for all corporate ESI transfers.
In particular, the use of structured and unstructured forms of ESI transfers should be included.
Where unstructured or structured ESI transfers are involved, corporate guidelines on message structures
should be included within the ESI transfer policy statement, or referenced by it.
The ESI transfer policy statement shall state the management's commitment to, and approach for, the use of
electronic systems for the transfer of ESI in a controlled manner, taking account of the need to preserve the
trustworthiness and reliability of the ESI.
The ESI transfer policy statement shall include, as a minimum, the following elements or, where applicable,
reference separate documentation on:
a) the scope of the ESI transfer policy [which can be different from that of information storage (see 4.7.2.2)];
b) the definition and allocation of roles and responsibilities for ESI transfer (see Clause 5);
c) the use of data compression (see 7.14.5);
d) the use of particular systems for the transfer of ESI (see 7.15);
e) the receiving of transferred electronic ESI (see 7.15);
f) the management of the linking of electronic identity to ESI (see 7.18);
g) the use of encryption (see 7.20.3).
The critical procedural issues are related to the delivery and receipt of ESI transfers, thus the ESI transfer
policy statement should give guidelines on how these procedures should be developed, and which standards
apply to these procedures, including where ESI transfers are either sent or received, or both. These
procedures (which can be different for send and receipt) should include:
h) the avoidance of messages with illegal content;
i) the avoidance of copyright issues;
j) protection against malicious software;
k) appropriate security procedures;
l) the application of the organization’s retention and disposal policies;
m) the avoidance of spam and other inappropriate messages (incoming and outgoing); and
n) the capture of audit trail evidence of transfer, send and receipt.
4.7.4 Information security policy
4.7.4.1 General
The organization should be aware of the value of the information that it manages within the organization, or
with its trading partners. This awareness includes an understanding of the duty of care principles.
To fulfil its duty of care obligations, the organization should:
a) be able to demonstrate compliance with legislation and regulatory bodies pertinent to its business
sector (e.g. public or private sector);
b) be able to demonstrate compliance with legislation and regulatory bodies pertinent to its country (or
other relevant geographical area) of origin, routing or receipt of electronic identity document attributes;
c) establish a chain of accountability and assign responsibility for all relevant activities; and
d) keep abreast of developments by keeping in contact with the appropriate legislative, regulatory, trade
and professional bodies and organizations.
The implications of an insecure processes and systems that manage ESI can be far reaching, and potentially
damaging to an organization. In order to ensure the integrity of ESI, it should be managed under the controls
specified in this document.
Suitable guidelines, which specify system security requirements, can already exist in organizational policies
or working practices. There can also be sector-specific guidance (e.g. financial or pharmaceutical) and
national or international standards. Where these do not exist, suitable guidelines should be developed,
approved and implemented.
The organization shall ensure that the ESI management and transfer systems operate within its information
security policy.
The information security policy shall cover:
e) the storage of electronic information over time (see 4.7.2); and
f) the transfer of ESI between systems (see 4.7.3).
NOTE ISO/IEC 27001 covers information security management. When requirements from ISO/IEC 27001 are
implemented within the boundaries of this document, it can provide helpful supporting evidence of the trustworthiness
and reliability of the ESI.
Different types of ESI can require different security techniques. These should be documented in the
information security policy.
4.7.4.2 Storage security policy statement
All processes and systems that manage ESI are vulnerable to compromise or change, whether accidental or
malicious. To protect these processes and systems, appropriate security measure
...