

SIST EN 18239:2026
(Main)Digital product passport - Access rights management, information system security, and business confidentiality
- Abstract
This document specifies the requirements for digital product passport (DPP) access rights management, including IT security, data protection, and responsibility transfer between economic operators. It defines the framework for managing confidential information access, while acknowledging that public DPP data requires no access restrictions to be read.
- Status
- Published
- Public Enquiry End Date
- 29-Sep-2025
- Publication Date
- 27-Sep-2026
- Technical Committee
- DPP - Digital Product Passport
- Current Stage
- 6060 - National Implementation/Publication (Adopted Project)
- Start Date
- 24-Sep-2026
- Due Date
- 29-Nov-2026
- Completion Date
- 28-Sep-2026
SIST EN 18239:2026 is the Slovenian adoption of EN 18239:2026, published by SIST and developed by CEN/CENELEC. It specifies how digital product passport (DPP) access rights are managed, how information system security and data protection are handled, and how responsibilities can be transferred between economic operators and other actors in the DPP life cycle.
What does SIST EN 18239:2026 specify?
SIST EN 18239:2026 specifies the framework for controlling access to DPP data, with public DPP data readable without access restrictions and controlled DPP data protected by access rights, authentication and authorization. It also sets expectations for confidentiality, auditability, service resilience and the transfer of responsibilities and data between actors.
The document is organized into:
- Clause 4 - business transactions and responsibilities related to the DPP
- Clause 5 - protection of business confidentiality and management of access rights
- Clause 6 - system and service resilience
- Annex A - authentication assumptions
- Annex ZA - link to Regulation (EU) 2024/1781
| Annex | What it covers |
|---|---|
| A | Authentication assumptions for managing controlled DPP data |
| ZA | Relationship with Regulation (EU) 2024/1781 and presumption of conformity |
What are the key requirements of SIST EN 18239:2026?
SIST EN 18239:2026 builds access control around the DPP life cycle and the actors who handle the product along the value chain. In practice, organisations need to assign roles and access based on the business stage and the legal role of the actor, not just on the existence of a DPP record.
- Clause 4 ties access management to DPP life-cycle phases and stages. This matters because access is not one-size-fits-all: a repairer, recycler, authority or service provider may need different DPP data at different times.
- Clause 4.2 identifies the main actor groups, including economic operators, consumers, professional repairers, independent operators, recyclers, market surveillance authorities, customs authorities and DPP service providers. This helps define who can request, manage or update DPP data.
- Clause 5.2 requires globally unique operator identifiers, logging, auditable changes and tamper-resistant records for access and role changes. In practice, this supports traceability when permissions are granted, modified or revoked.
- Clause 5.2 requires access to controlled DPP data to be authenticated and authorized, with least privilege and data element-level control. This means organisations should give only the minimum data and functions needed for a role.
- Clause 5.2 and Clause 6.2 distinguish public DPP data from controlled DPP data. Public data can be read without authentication, while controlled data requires role-based access.
- Clause 5.2 also addresses delegation, emergency revocation, anti-scraping measures and non-repudiation. This matters when access rights change, when an actor is no longer authorized, or when misuse must be provable.
- Clause 6 requires access revocation policies, digital operational resilience, security by design, incident response, redundancy and recovery capability. In practice, DPP services need continuity planning, backup arrangements and measures against denial-of-service attacks.
- Annex A sets authentication assumptions such as identity proofing, multifactor authentication, protected cryptographic information and timely suspension or revocation. This gives a baseline for secure login and identity checks.
What terms does SIST EN 18239:2026 define?
SIST EN 18239:2026 defines the terms used to describe DPP access control and security.
- controlled DPP data - DPP information whose access is limited by the user’s access rights.
- system resilience - the ability to recover from security compromises or attacks.
- system availability - the property of being accessible and usable on demand by an authorized actor.
- cyber resilience - the ability to maintain business continuity despite adverse conditions, attacks or compromises.
- actor - an organization or individual that fulfils a role.
- notified actor - an organization or individual entitled by an authorized accrediting body or authority to fulfil a role in the DPP life cycle.
- digital product passport (DPP) - a digital record of product characteristics throughout its life cycle.
- identity proofing - the process of capturing and verifying information to identify an entity to a specified assurance level.
Who uses SIST EN 18239:2026?
SIST EN 18239:2026 is used by organisations that create, host, update, protect or access DPP data. That includes manufacturers, authorized representatives, importers, distributors, dealers, fulfilment service providers, DPP service providers, professional repairers, recyclers, customs authorities and market surveillance authorities.
It is also relevant for IT and security teams, compliance staff and product data managers who define access rights, build authentication and authorization flows, log changes, manage revocation and support transfers of responsibility between operators.
Which standards are used with SIST EN 18239:2026?
SIST EN 18239:2026 has one normative reference:
- EN 18219:2026 - provides the globally unique operator identifiers used in access management.
The text also cites supporting standards that shape specific requirements:
- EN ISO 11354-1:2011 - provides the framework for the enterprise interoperability life-cycle phases and stages used in Clause 4.
- EN ISO/IEC 27000:2020 and EN ISO/IEC 27001:2023 - support information security management, access security and the ISMS approach in Clause 5 and Clause 6.
- EN ISO 22301:2019 and ISO/IEC 27031:2025 - support business continuity and ICT readiness for resilience.
- ISO/IEC 29115:2013 and ISO 26800:2011 - underpin some authentication and user-related terminology.
- ISO 23234:2021 and ISO/IEC 29180:2012 - are cited in the definitions for actor and system resilience.
What does the SIST EN 18239:2026 document contain?
SIST EN 18239:2026 contains requirements for identifying actors, assigning access roles, protecting confidential DPP information and keeping controlled data auditable and revocable. It also includes operational expectations for authentication, logging, service availability, incident response, recovery and continuous improvement.
Annex A gives authentication assumptions for controlled DPP data, including identity proofing, multifactor authentication and secure handling of cryptographic information. Annex ZA maps the standard to Article 11 of Regulation (EU) 2024/1781 and explains where the standard is intended to support presumption of conformity.
The bibliography points to related standards on business continuity, information security, supplier relationships, authentication assurance and enterprise interoperability.
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.

Bureau Veritas
Bureau Veritas is a world leader in laboratory testing, inspection and certification services.
DNV
DNV is an independent assurance and risk management provider.
Sponsored listings
Frequently Asked Questions
SIST EN 18239:2026 is a standard published by the Slovenian Institute for Standardization (SIST). Its full title is "Digital product passport - Access rights management, information system security, and business confidentiality". This standard covers: This document specifies the requirements for digital product passport (DPP) access rights management, including IT security, data protection, and responsibility transfer between economic operators. It defines the framework for managing confidential information access, while acknowledging that public DPP data requires no access restrictions to be read.
This document specifies the requirements for digital product passport (DPP) access rights management, including IT security, data protection, and responsibility transfer between economic operators. It defines the framework for managing confidential information access, while acknowledging that public DPP data requires no access restrictions to be read.
SIST EN 18239:2026 is classified under the following ICS (International Classification for Standards) categories: 13.020.20 - Environmental economics. Sustainability; 35.240.63 - IT applications in trade. The ICS classification helps identify the subject area and facilitates finding related standards.
SIST EN 18239:2026 is associated with the following European legislation: EU Directives/Regulations: 2024/1781, (EU) 2024/1781; Standardization Mandates: M/604, M/604 AMD 1. When a standard is cited in the Official Journal of the European Union, products manufactured in conformity with it benefit from a presumption of conformity with the essential requirements of the corresponding EU directive or regulation.
SIST EN 18239:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
SLOVENSKI STANDARD
01-november-2026
Digitalni potni list izdelka - Upravljanje dostopnih pravic, varnost informacijskega
sistema in poslovna zaupnost
Digital product passport - Access rights management, information system security, and
business confidentiality
Digitaler Produktpass - Management der Benutzerrechte, IT-Sicherheit und
Geschäftsgeheimnisse
Passeport numérique des produits - Gestion des droits d'accès, sécurité du système
d'information et confidentialité des affaires
Ta slovenski standard je istoveten z: EN 18239:2026
ICS:
13.020.20 Okoljska ekonomija. Environmental economics.
Trajnostnost Sustainability
35.240.63 Uporabniške rešitve IT v IT applications in trade
trgovini
2003-01.Slovenski inštitut za standardizacijo. Razmnoževanje celote ali delov tega standarda ni dovoljeno.
EUROPEAN STANDARD EN 18239
NORME EUROPÉENNE
EUROPÄISCHE NORM
September 2026
ICS 13.020.20
English version
Digital product passport - Access rights management,
information system security, and business confidentiality
Passeport numérique des produits - Gestion des droits Digitaler Produktpass - Management der
d'accès, sécurité du système d'information et Benutzerrechte, IT-Sicherheit und
confidentialité des affaires Geschäftsgeheimnisse
This European Standard was approved by CEN on 17 August 2026.
CEN and CENELEC members are bound to comply with the CEN/CENELEC Internal Regulations which stipulate the conditions for
giving this European Standard the status of a national standard without any alteration. Up-to-date lists and bibliographical
references concerning such national standards may be obtained on application to the CEN-CENELEC Management Centre or to
any CEN and CENELEC member.
This European Standard exists in three official versions (English, French, German). A version in any other language made by
translation under the responsibility of a CEN and CENELEC member into its own language and notified to the CEN-CENELEC
Management Centre has the same status as the official versions.
CEN and CENELEC members are the national standards bodies and national electrotechnical committees of Austria, Belgium,
Bulgaria, Croatia, Cyprus, Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Iceland, Ireland, Italy,
Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Republic of North Macedonia, Romania, Serbia,
Slovakia, Slovenia, Spain, Sweden, Switzerland, Türkiye and United Kingdom.
CEN-CENELEC Management Centre:
Rue de la Science 23, B-1040 Brussels
© 2026 CEN/CENELEC All rights of exploitation in any form and by any means
Ref. No. EN 18239:2026 E
reserved worldwide for CEN national Members and for
CENELEC Members.
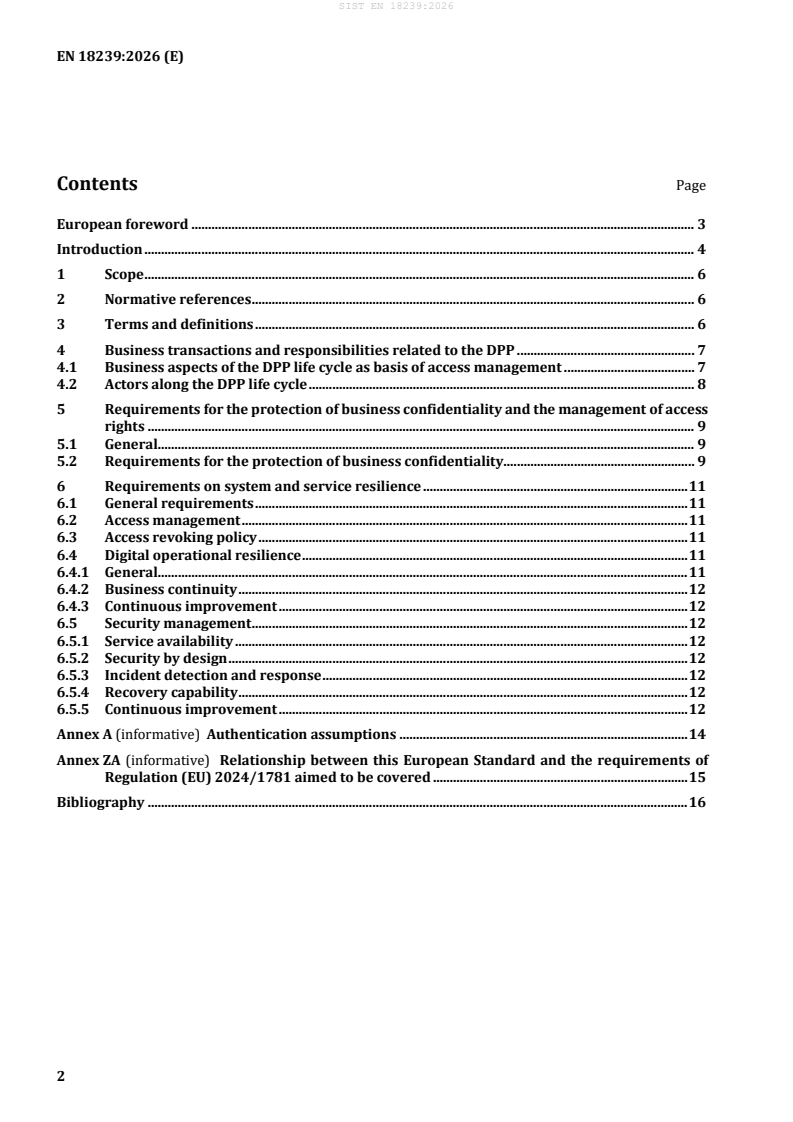
Contents Page
European foreword . 3
Introduction . 4
1 Scope . 6
2 Normative references . 6
3 Terms and definitions . 6
4 Business transactions and responsibilities related to the DPP . 7
4.1 Business aspects of the DPP life cycle as basis of access management . 7
4.2 Actors along the DPP life cycle . 8
5 Requirements for the protection of business confidentiality and the management of access
rights . 9
5.1 General. 9
5.2 Requirements for the protection of business confidentiality . 9
6 Requirements on system and service resilience . 11
6.1 General requirements . 11
6.2 Access management . 11
6.3 Access revoking policy . 11
6.4 Digital operational resilience . 11
6.4.1 General. 11
6.4.2 Business continuity . 12
6.4.3 Continuous improvement . 12
6.5 Security management . 12
6.5.1 Service availability . 12
6.5.2 Security by design . 12
6.5.3 Incident detection and response . 12
6.5.4 Recovery capability . 12
6.5.5 Continuous improvement . 12
Annex A (informative) Authentication assumptions . 14
Annex ZA (informative) Relationship between this European Standard and the requirements of
Regulation (EU) 2024/1781 aimed to be covered . 15
Bibliography . 16
European foreword
This document (EN 18239:2026) has been prepared by the Joint Technical Committee CEN-CENELEC/
JTC 24 “Digital Product Passport - Framework and System”, the secretariat of which is held by DIN.
This European Standard shall be given the status of a national standard, either by publication of an
identical text or by endorsement, at the latest by March 2027, and conflicting national standards shall be
withdrawn at the latest by March 2027.
Attention is drawn to the possibility that some of the elements of this document may be the subject of
patent rights. CEN-CENELEC shall not be held responsible for identifying any or all such patent rights.
This document has been prepared under a standardization request addressed to CEN-CENELEC by the
European Commission. The Standing Committee of the EFTA States subsequently approves these
requests for its Member States.
For the relationship with EU Legislation, see informative Annex ZA, which is an integral part of this
document.
Any feedback and questions on this document should be directed to the users’ national standards
body/national committee. A complete listing of these bodies can be found on the CEN and CENELEC
websites.
According to the CEN-CENELEC Internal Regulations, the national standards organisations of the
following countries are bound to implement this European Standard: Austria, Belgium, Bulgaria, Croatia,
Cyprus, Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Iceland, Ireland,
Italy, Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Republic of North
Macedonia, Romania, Serbia, Slovakia, Slovenia, Spain, Sweden, Switzerland, Türkiye and the United
Kingdom.
Introduction
0.1 Background
A digital product passport (DPP) is a key enabling mechanism to make product information traceable and
accessible across value chains – supporting economic operators, manufacturers, distributors, repairers,
recyclers and consumers to make informed decisions and to support a circular economy. The
implementation of DPPs will be carried out progressively. Sector-specific initiatives will determine the
precise DPP content and requirements for individual product groups.
To support the implementation of DPPs, 8 standards have been developed:
— EN 18219:2026 – Digital product passport – Unique identifiers
— EN 18220:2026 – Digital product passport – Data carriers
— EN 18216:2026 – Digital product passport – Data exchange protocols
— EN 18222:2026 – Digital product passport – Application Programming Interfaces (APIs) for the
product passport lifecycle management and searchability
— EN 18223:2026 – Digital product passport – System interoperability
— EN 18221:2026 – Digital product passport – Data storage, archiving, and data persistence
— EN 18239:2026 – Digital product passport – Access rights management, information system security,
and business confidentiality (this document)
— EN 18246:2026 – Digital product passport – Data authentication, reliability and integrity
0.2 Overview
This document aims at harmonizing the identity management that ensures that organisations,
individuals, machines and services are provided with acknowledged identities. This document defines
clear requirements related to access control measures to regulate the access to controlled DPP data.
This document defines rules and requirements related to:
— access right management;
— access control;
— clarification of DPP system roles and responsibilities to provide the means to define mechanisms on
how to exchange access right information between economic operators, back-up system operators
and registry of the regulated market controlling entity;
— measures to regulate the access to controlled DPP data;
— possibility for product group specific definition of access rights by relevant legal acts;
— information system security;
— business confidentiality and their representation in access rights management;
— differentiation of access rights of different user groups and authorities;
— guarantee of IT-security, cybersecurity, and data protection; and
— clarification of DPP system roles and responsibilities to provide the means to define mechanisms on
how to transfer responsibilities, access-rights, and data from one economic operator to another.
EXAMPLE When a DPP will need to be updated to include information related to repair activities performed
by a professional repairer.
1 Scope
This document specifies the requirements for digital product passport (DPP) access rights management,
including IT security, data protection, and responsibility transfer between economic operators. It defines
the framework for managing confidential information access, while acknowledging that public DPP data
requires no access restrictions to be read.
2 Normative references
The following documents are referred to in the text in such a way that some or all of their content
constitutes requirements of this document. For dated references, only the edition cited applies. For
undated references, the latest edition of the referenced document (including any amendments) applies.
EN 18219:2026, Digital product passport — Unique identifiers
3 Terms and definitions
For the purposes of this document, the following terms and definitions apply:
ISO and IEC maintain terminology databases for use in standardization at the following addresses:
— ISO Online browsing platform: available at https://www.iso.org/obp
— IEC Electropedia: available at https://www.electropedia.org/
3.1
controlled DPP data
information on DPP whose access is controlled based on the user’s access rights
Note 1 to entry: User: person who interacts with a system, product or service
[SOURCE: ISO 26800:2011, 2.10, modified – Notes changed]
3.2
system resilience
ability to recover from security compromises or attacks
[SOURCE: ISO/IEC 29180:2012]
3.3
system availability
property of being accessible and usable on demand by an authorized actor
[SOURCE: EN ISO/IEC 27000:2020]
3.4
cyber resilience
ability to maintain business continuity despite adverse conditions, attacks, or compromises on critical
data flow and related information systems
3.5
actor
organization or individual that fulfils a role
[SOURCE: ISO 23234:2021, 3.4]
3.6
notified actor
organization or individual entitled by an authorized accrediting body or authority, that fulfils a role in the
DPP life cycle
3.7
digital product passport
DPP
digital record of product characteristics throughout its life cycle
Note 1 to entry: Example characteristics include environment sustainability, environmental impact and
recyclability.
3.8
non-repudiation
ability to protect against denial by one of the entities involved in an action of having participated in all or
part of the action
[SOURCE: ISO/IEC 29115:2013, 3.19]
3.9
information/communication technology
ICT
technology for gathering, storing, retrieving, processing, analysing and transmitting information
[SOURCE: ISO 9241-20:2021, definition 3.4]
3.10
identity proofing
process by which the registration authority captures and verifies sufficient information to identify an
entity to a specified or understood level of assurance
[SOURCE: ISO/IEC 29115:2013, 3.15]
4 Business transactions and responsibilities related to the DPP
4.1 Business aspects of the DPP life cycle as basis of access management
Access rights management is defined for the different life cycle phases and stages of a DPP. Such phases
and stages are based on EN ISO 11354-1:2011.
In general, not all the phases and the stages mentioned in this document might be applicable to every
product sector. Therefore, only the phases and stages relevant for a specific product group shall be
considered. Moreover, in case a product group specific stage is not represented in the following list, it
shall be considered during the access rights management implementation.
4.2 Actors along the DPP life cycle
This section identifies the main actors who are responsible for the handling of a DPP relevant product
across the value chain and therefore need to access a DPP along its business stages. The identified actors
are the following:
1. Economic operators (in short EOs): role encompassing the manufacturer, the authorized
representative, the importer, the distributor, the dealer and the fulfilment service provider.
a. Manufacturers: any natural or legal person that manufactures a product or that has a product
designed or manufactured and markets that product under their name or trademark.
b. Authorized representatives: any natural or legal person established in the regulated market
that has received a legally binding (e.g. written) mandate from the manufacturer to act on the
manufacturer’s behalf in relation to specified tasks with regard to the manufacturer’s
obligations.
c. Importers: any natural or legal person that places a product coming from outside the regulated
market on the regulated market.
d. Distributors: any natural or legal person in the supply chain, other than the manufacturer or
the importer, that makes a product available on the market.
e. Dealers: a distributor or any other natural or legal person that offers products for sale, hire or
hire purchase, or that displays products to end users in the course of a commercial activity,
including through distance selling; and includes any natural or legal person that puts a product
into service in the course of a commercial activity.
f. Fulfilment service providers: any natural or legal person offering, in the course of commercial
activity, services such as: warehousing, packaging, addressing and dispatching, without having
ownership of the products involved.
2. Other value chain actors
a. Consumers: individual member of the general public purchasing or using goods, property or
services for private purposes [EN ISO 14025:2010, 3.16].
b. Professional repairers: a natural or legal person that provides professional repair or
maintenance services for a product, irrespective of whether that person acts within the
manufacturer’s distribution system or independently.
c. Independent operators: natural or legal person that is independent of the manufacturer and is
directly or indirectly involved in the refurbishment, repair, maintenance or repurposing of a
product, and includes waste management operators, refurbishers, repairers, manufacturers or
distributors of repair equipment, tools or spare parts, as
...