

SIST EN 18246:2026
(Main)Digital product passport - Data authentication, reliability and integrity
- Abstract
This document defines the requirements and frameworks for secure information processing and communication to safeguard integrity, authenticity and reliability in the digital product passport (DPP) data exchange, minimizing product fraud and counterfeiting through data verification and integrity enforcement mechanisms.
This document provides a framework for establishing trust, interoperability, and interoperation via secure electronically signed data construct (ESDC) for multi-actor applications, applicable across various sectors and in multilingual environments. Existing hardware and software systems for unique product identification and storage of this identification are to be considered.
The following is out of scope of the document: system architecture for DPP, DPP use cases, secure elements related to data carriers and cryptographic security features for unique product identifiers.
NOTE 1 While not disrupting existing traceability and authentication systems, this document facilitates interoperability by introducing an ESDC scheme to be combined with existing data constructs to cover and preserve existing data models.
NOTE 2 Annex B includes illustrative examples and references to supporting implementations, intended to demonstrate approaches that promote interoperability across diverse environments. These references are provided to assist stakeholders in selecting appropriate solutions that comply with applicable legal obligations and technical standards, while preserving existing systems.
- Status
- Published
- Public Enquiry End Date
- 30-Oct-2025
- Publication Date
- 27-Sep-2026
- Technical Committee
- DPP - Digital Product Passport
- Current Stage
- 6060 - National Implementation/Publication (Adopted Project)
- Start Date
- 24-Sep-2026
- Due Date
- 29-Nov-2026
- Completion Date
- 28-Sep-2026
SIST EN 18246:2026 is the Slovenian adoption of EN 18246:2026 from SIST. It specifies how digital product passport (DPP) data can be authenticated, verified and protected so that integrity, authenticity and reliability are preserved during data exchange. The document is aimed at economic operators, DPP service providers, verifiers and other actors that create, exchange or check DPP data across sectors.
What does SIST EN 18246:2026 specify?
SIST EN 18246:2026 sets requirements and frameworks for secure information processing and communication in the DPP context. Its focus is the trust layer around DPP data, not the whole DPP system design.
The standard covers secure exchange of DPP data, the use of electronically signed data constructs (ESDCs), and the way identifiers, data carriers and actor identities support trust. It is written to work across sectors and in multilingual environments, while taking existing hardware and software for unique product identification into account.
It excludes system architecture for the DPP, DPP use cases, secure elements related to data carriers, and cryptographic security features for unique product identifiers.
| Annex | What it covers |
|---|---|
| Annex A | The essential characteristics of ESDCs for secure, verifiable DPP data |
| Annex B | Informative examples of ESDCs such as electronic attestation of attributes, VDS, DigSig and W3C Verifiable Credentials |
| Annex C | Fair competition risks, including vendor-specific software and SME resource pressure |
| Annex ZA | Link between this European Standard and Regulation (EU) 2024/1781 |
What are the key requirements of SIST EN 18246:2026?
SIST EN 18246:2026 combines open public access with stronger controls for restricted data, and it requires that DPP changes remain attributable and auditable. In practice, that means a reader should be able to understand what is public, what is protected, and how authenticity is proven.
Public access and usability
- Public DPP data shall be accessible without authentication and without additional software, and it shall not require encryption or authentication for access to public information. This matters because a consumer or inspector should be able to reach the basic DPP view with a normal browser or common device.
- Public access shall not collect personal information from the person accessing the data, and the system shall avoid profiling where technically feasible. This reduces privacy risk during ordinary product look-up.
- The system shall not ask for personal data or use advanced device functions such as location, messaging, call control or app installation when only public DPP data is being read. This keeps the access path simple and limits overreach on the user device.
Identity, communication and trust
- Actors accessing controlled DPP data shall be identified by a globally unique identifier, and authentication shall use the required level of assurance. This gives controlled access a traceable identity basis.
- Communication of DPP data shall be secure, using encryption and authentication for protected data exchanges. For public data, those mechanisms are not required. The document also points readers to ETSI EN 319 401:2024 for Trust Service Providers.
- The product identifier in the data carrier should be protected where relevant, and any solution for authenticity and integrity shall be interoperable with EN 18219:2026. The physical data carrier, where protected, shall also remain interoperable with EN 18220:2026.
Authenticity, integrity and audit trail
- A DPP shall be verifiable for authenticity and integrity, and that verification shall be free of charge and available without limitation for the verifier. This is important for customs, market surveillance and other checks.
- All data providers shall be authenticated by proof of ownership of a digital certificate issued through identity proofing. Every creation, update and deletion shall be bound to the authenticated actor, for example by a digital signature, digital seal, electronic attestation of attributes or an ESDC.
- Creation, modification and deletion shall be logged in a non-repudiable and audit-proof manner, with log integrity preserved over time. The responsible editor of a change shall be identifiable through a globally unique operator identifier.
- Annex A explains ESDCs as signed data sets with a header, payload, signature and optional fields. That structure is what lets the DPP link data to an issuer and detect later changes.
Risk, anti-fraud and accessibility
- The standard addresses risks to data security, privacy, product counterfeiting, and exclusion. It calls for protection against phishing, quishing, malicious code and mass data scraping.
- For counterfeiting risk, the document allows proportionate mitigation such as visible indicators or DPP-linked authentication services.
- Access shall be available to any natural person with an internet-connected device, and persons with disabilities shall be able to perceive, understand, navigate and interact with public DPP content. Security measures shall not block that access.
What terms does SIST EN 18246:2026 define?
- Electronically signed data construct (ESDC) - A structured data set with a header, payload, signature and optional data fields, used to make DPP data portable and verifiable.
- Digital product passport (DPP) - A digital record of product characteristics throughout the product life cycle.
- Unique product identifier - A unique string that identifies a product and can also link to the DPP.
- Controlled DPP data - DPP information whose access is limited according to user access rights.
- Economic operator - The manufacturer, authorized representative, importer, distributor, dealer or fulfilment service provider that places the product on the market.
- Verifier - The entity that performs verification.
- Non-repudiation - The ability to prove that an action or event took place so it cannot later be denied.
Who uses SIST EN 18246:2026?
SIST EN 18246:2026 is used by economic operators that issue or update DPP data, and by DPP service providers that host, present or protect that data. It is also relevant to verifiers who check authenticity and integrity, and to organizations that manage controlled access.
In practice, it supports manufacturers, importers, distributors, dealers and fulfilment service providers when they place products on the market or maintain DPP information. It also matters for customs, market surveillance authorities, repairers, recyclers and consumers who need trustworthy product information without unnecessary barriers.
Which standards are used with SIST EN 18246:2026?
The document’s main normative references are:
| Standard | Contribution in this document |
|---|---|
| EN 18216:2026 | Sets the DPP data exchange protocols used for secure communication |
| EN 18219:2026 | Defines unique identifiers for products and economic operators |
| EN 18220:2026 | Defines data carriers used to store or relay identification data |
| EN 18221:2026 | Covers data storage, archiving and persistence, including recording of changes |
| EN 18239:2026 | Covers access rights management, information system security and business confidentiality |
The annexes also cite implementation standards and frameworks such as ISO 22376, ISO/IEC 20248, W3C Verifiable Credentials, and ETSI digital signature standards. These support the practical formats used for ESDCs, visible digital seals, DigSig and related trust services.
What does the SIST EN 18246:2026 document contain?
SIST EN 18246:2026 contains general security assumptions for DPPs, followed by a risk-and-requirements section that separates public data access, controlled access, product identification, product fraud risks and accessibility. It then gives a normative annex on ESDCs and informative annexes with examples and competition-related considerations.
Annex A explains how ESDCs support authenticity, integrity and non-repudiation. Annex B gives practical examples, including electronic attestation of attributes, visible digital seals, DigSig and W3C Verifiable Credentials, and shows how they can be used for scanning, verification and offline checks where trust information is available.
Annex C discusses market fairness, especially the risk of vendor-specific software creating barriers and the need to avoid disproportionate effort for SMEs. Annex ZA maps Clause 4.2 to Regulation (EU) 2024/1781 and Table ZA.1 identifies the correspondence used for presumption of conformity within the scope of the standard.
Relations
- Referred By
SIST EN ISO 28881:2022 - Machine tools - Safety - Electrical discharge machines (ISO 28881:2022) - Effective Date
- 28-Jan-2026
- Effective Date
- 28-Jan-2026
- Referred By
SIST EN ISO 19085-15:2026 - Woodworking machines - Safety - Part 15: Presses (ISO 19085 -15:2025) - Effective Date
- 28-Jan-2026
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.

Bureau Veritas
Bureau Veritas is a world leader in laboratory testing, inspection and certification services.
DNV
DNV is an independent assurance and risk management provider.
Sponsored listings
Frequently Asked Questions
SIST EN 18246:2026 is a standard published by the Slovenian Institute for Standardization (SIST). Its full title is "Digital product passport - Data authentication, reliability and integrity". This standard covers: This document defines the requirements and frameworks for secure information processing and communication to safeguard integrity, authenticity and reliability in the digital product passport (DPP) data exchange, minimizing product fraud and counterfeiting through data verification and integrity enforcement mechanisms. This document provides a framework for establishing trust, interoperability, and interoperation via secure electronically signed data construct (ESDC) for multi-actor applications, applicable across various sectors and in multilingual environments. Existing hardware and software systems for unique product identification and storage of this identification are to be considered. The following is out of scope of the document: system architecture for DPP, DPP use cases, secure elements related to data carriers and cryptographic security features for unique product identifiers. NOTE 1 While not disrupting existing traceability and authentication systems, this document facilitates interoperability by introducing an ESDC scheme to be combined with existing data constructs to cover and preserve existing data models. NOTE 2 Annex B includes illustrative examples and references to supporting implementations, intended to demonstrate approaches that promote interoperability across diverse environments. These references are provided to assist stakeholders in selecting appropriate solutions that comply with applicable legal obligations and technical standards, while preserving existing systems.
This document defines the requirements and frameworks for secure information processing and communication to safeguard integrity, authenticity and reliability in the digital product passport (DPP) data exchange, minimizing product fraud and counterfeiting through data verification and integrity enforcement mechanisms. This document provides a framework for establishing trust, interoperability, and interoperation via secure electronically signed data construct (ESDC) for multi-actor applications, applicable across various sectors and in multilingual environments. Existing hardware and software systems for unique product identification and storage of this identification are to be considered. The following is out of scope of the document: system architecture for DPP, DPP use cases, secure elements related to data carriers and cryptographic security features for unique product identifiers. NOTE 1 While not disrupting existing traceability and authentication systems, this document facilitates interoperability by introducing an ESDC scheme to be combined with existing data constructs to cover and preserve existing data models. NOTE 2 Annex B includes illustrative examples and references to supporting implementations, intended to demonstrate approaches that promote interoperability across diverse environments. These references are provided to assist stakeholders in selecting appropriate solutions that comply with applicable legal obligations and technical standards, while preserving existing systems.
SIST EN 18246:2026 is classified under the following ICS (International Classification for Standards) categories: 13.020.20 - Environmental economics. Sustainability; 35.240.63 - IT applications in trade. The ICS classification helps identify the subject area and facilitates finding related standards.
SIST EN 18246:2026 has the following relationships with other standards: It is inter standard links to SIST EN ISO 28881:2022, SIST EN ISO 3691-4:2023, SIST EN ISO 19085-15:2026. Understanding these relationships helps ensure you are using the most current and applicable version of the standard.
SIST EN 18246:2026 is associated with the following European legislation: EU Directives/Regulations: 2024/1781, (EU) 2024/1781; Standardization Mandates: M/604, M/604 AMD 1. When a standard is cited in the Official Journal of the European Union, products manufactured in conformity with it benefit from a presumption of conformity with the essential requirements of the corresponding EU directive or regulation.
SIST EN 18246:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
SLOVENSKI STANDARD
01-november-2026
Digitalni potni list izdelka - Preverjanje pristnosti, zanesljivost in celovitost
podatkov
Digital product passport - Data authentication, reliability and integrity
Digitaler Produktpass - Datenauthentifizierung, Zuverlässigkeit und Integrität
Passeport numérique des produits - Authentification, fiabilité et intégrité des données
Ta slovenski standard je istoveten z: EN 18246:2026
ICS:
13.020.20 Okoljska ekonomija. Environmental economics.
Trajnostnost Sustainability
35.240.63 Uporabniške rešitve IT v IT applications in trade
trgovini
2003-01.Slovenski inštitut za standardizacijo. Razmnoževanje celote ali delov tega standarda ni dovoljeno.
EUROPEAN STANDARD EN 18246
NORME EUROPÉENNE
EUROPÄISCHE NORM
September 2026
ICS 35.240.63
English version
Digital product passport - Data authentication, reliability
and integrity
Passeport numérique des produits - Authentification, Digitaler Produktpass - Datenauthentifizierung,
fiabilité et intégrité des données Zuverlässigkeit und Integrität
This European Standard was approved by CEN on 17 August 2026.
CEN and CENELEC members are bound to comply with the CEN/CENELEC Internal Regulations which stipulate the conditions for
giving this European Standard the status of a national standard without any alteration. Up-to-date lists and bibliographical
references concerning such national standards may be obtained on application to the CEN-CENELEC Management Centre or to
any CEN and CENELEC member.
This European Standard exists in three official versions (English, French, German). A version in any other language made by
translation under the responsibility of a CEN and CENELEC member into its own language and notified to the CEN-CENELEC
Management Centre has the same status as the official versions.
CEN and CENELEC members are the national standards bodies and national electrotechnical committees of Austria, Belgium,
Bulgaria, Croatia, Cyprus, Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Iceland, Ireland, Italy,
Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Republic of North Macedonia, Romania, Serbia,
Slovakia, Slovenia, Spain, Sweden, Switzerland, Türkiye and United Kingdom.
CEN-CENELEC Management Centre:
Rue de la Science 23, B-1040 Brussels
© 2026 CEN/CENELEC All rights of exploitation in any form and by any means
Ref. No. EN 18246:2026 E
reserved worldwide for CEN national Members and for
CENELEC Members.
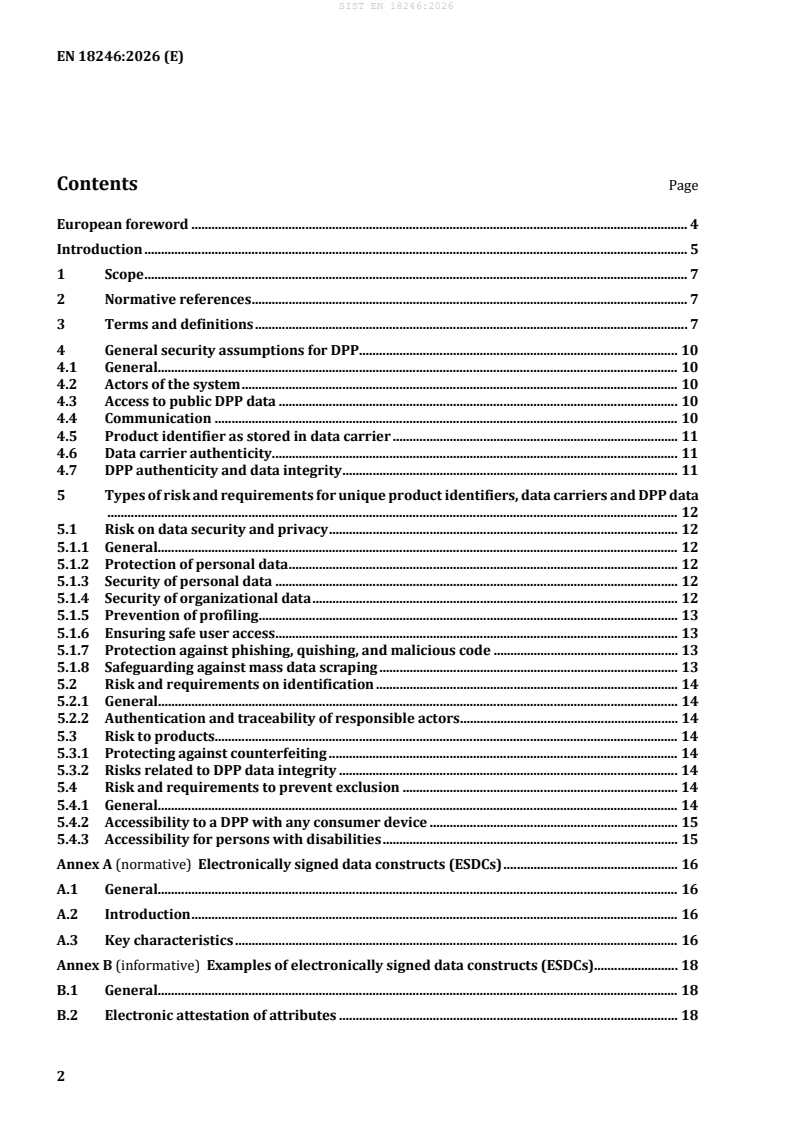
Contents Page
European foreword . 4
Introduction . 5
1 Scope . 7
2 Normative references . 7
3 Terms and definitions . 7
4 General security assumptions for DPP. 10
4.1 General. 10
4.2 Actors of the system . 10
4.3 Access to public DPP data . 10
4.4 Communication . 10
4.5 Product identifier as stored in data carrier . 11
4.6 Data carrier authenticity. 11
4.7 DPP authenticity and data integrity . 11
5 Types of risk and requirements for unique product identifiers, data carriers and DPP data
.......................................................................................................................................................................... 12
5.1 Risk on data security and privacy . 12
5.1.1 General. 12
5.1.2 Protection of personal data . 12
5.1.3 Security of personal data . 12
5.1.4 Security of organizational data . 12
5.1.5 Prevention of profiling . 13
5.1.6 Ensuring safe user access . 13
5.1.7 Protection against phishing, quishing, and malicious code . 13
5.1.8 Safeguarding against mass data scraping . 13
5.2 Risk and requirements on identification . 14
5.2.1 General. 14
5.2.2 Authentication and traceability of responsible actors . 14
5.3 Risk to products. 14
5.3.1 Protecting against counterfeiting . 14
5.3.2 Risks related to DPP data integrity . 14
5.4 Risk and requirements to prevent exclusion . 14
5.4.1 General. 14
5.4.2 Accessibility to a DPP with any consumer device . 15
5.4.3 Accessibility for persons with disabilities . 15
Annex A (normative) Electronically signed data constructs (ESDCs) . 16
A.1 General. 16
A.2 Introduction . 16
A.3 Key characteristics . 16
Annex B (informative) Examples of electronically signed data constructs (ESDCs). 18
B.1 General. 18
B.2 Electronic attestation of attributes . 18
B.3 Visible digital seal (VDS - ISO 22376) . 19
B.4 AIDC digital signature verifiable data structure (DigSig - ISO/IEC 20248) . 20
B.5 W3C Verifiable Credentials . 21
B.6 Digital signatures and electronic seals . 22
Annex C (informative) Risk and considerations related to fair competition . 23
C.1 General . 23
C.2 Avoiding market restrictions by vendor-specific software . 23
C.3 Disproportionate resource demand for SMEs . 23
Annex ZA (informative) Relationship between this European Standard and the requirements of
Regulation (EU) 2024/1781 aimed to be covered . 24
Bibliography . 25
European foreword
This document (EN 18246:2026) has been prepared by the Joint Technical Committee CEN-CENELEC/
JTC 24 “Digital Product Passport - Framework and System”, the secretariat of which is held by DIN.
This European Standard shall be given the status of a national standard, either by publication of an
identical text or by endorsement, at the latest by March 2027, and conflicting national standards shall be
withdrawn at the latest by March 2027.
Attention is drawn to the possibility that some of the elements of this document may be the subject of
patent rights. CEN-CENELEC shall not be held responsible for identifying any or all such patent rights.
This document has been prepared under a standardization request addressed to CEN-CENELEC by the
European Commission. The Standing Committee of the EFTA States subsequently approves these
requests for its Member States.
For the relationship with EU Legislation, see informative Annex ZA, which is an integral part of this
document.
Any feedback and questions on this document should be directed to the users’ national standards
body/national committee. A complete listing of these bodies can be found on the CEN and CENELEC
websites.
According to the CEN-CENELEC Internal Regulations, the national standards organisations of the
following countries are bound to implement this European Standard: Austria, Belgium, Bulgaria, Croatia,
Cyprus, Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Iceland, Ireland,
Italy, Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Republic of North
Macedonia, Romania, Serbia, Slovakia, Slovenia, Spain, Sweden, Switzerland, Türkiye and the United
Kingdom.
Introduction
0.1 Background
A digital product passport (DPP) is a key enabling mechanism to make product information traceable and
accessible across value chains – supporting economic operators, manufacturers, distributors, repairers,
recyclers and consumers to make informed decisions and to support a circular economy. The
implementation of DPPs will be carried out progressively. Sector-specific initiatives will determine the
precise DPP content and requirements for individual product groups.
To support the implementation of DPPs, 8 standards have been developed:
— EN 18219:2026 – Digital product passport – Unique identifiers
— EN 18220:2026 – Digital product passport – Data carriers
— EN 18216:2026 – Digital product passport – Data exchange protocols
— EN 18222:2026 – Digital product passport – Application Programming Interfaces (APIs) for the
product passport lifecycle management and searchability
— EN 18223:2026 – Digital product passport – System interoperability
— EN 18221:2026 – Digital product passport – Data storage, archiving, and data persistence
— EN 18239:2026 – Digital product passport – Access rights management, information system security,
and business confidentiality
— EN 18246:2026 – Digital product passport – Data authentication, reliability and integrity (this
document)
0.2 Overview
Trust is key to any transaction whether physical or digital. Data and information collected during the
whole life cycle of the product is to be protected from both accidental and malicious compromise and
misuse.
Reasonable security expectation is likely to address the following elements of the DPP deployment:
— management and verification of identifiers;
— relationship between the unique identifiers and possible authentication elements related to them;
— questions that deal with the identification of the verifier and any authorized access to privileged
product-related information;
— authentication solutions;
— artefact metrics (technical measurements used to support verification or trust in physical objects),
where relevant;
— information processing and communication that protects integrity along the supply chain of physical
and related electronic documents, products, software and services life cycle to mitigate the risk of
product fraud and counterfeit goods, by using object identification techniques; and
— electronically signed data constructs (ESDCs) or equivalent functions.
A wide variety of information security techniques are routinely deployed at scale and at different levels.
For example, the banking, retail, and entertainment industries are global, connected, and always
available. The EU DPP system should leverage industry standards and best practices in all aspects of the
DPP solution, from data generation by the economic operator and data storage in distributed data
centres, through to the management of access rights for data access and data queries. The DPP end users,
product owners, and enforcement agencies will all benefit from a trustworthy DPP infrastructure.
The unique product identifier, as stored in a data carrier can be considered as the DPP access anchor.
Trust in the identifier is therefore a foundational element to the trust of DPP.
1 Scope
This document defines the requirements and frameworks for secure information processing and
communication to safeguard integrity, authenticity and reliability in the digital product passport (DPP)
data exchange, minimizing product fraud and counterfeiting through data verification and integrity
enforcement mechanisms.
This document provides a framework for establishing trust, interoperability, and interoperation via
secure electronically signed data construct (ESDC) for multi-actor applications, applicable across various
sectors and in multilingual environments. Existing hardware and software systems for unique product
identification and storage of this identification are to be considered.
The following is out of scope of the document: system architecture for DPP, DPP use cases, secure
elements related to data carriers and cryptographic security features for unique product identifiers.
NOTE 1 While not disrupting existing traceability and authentication systems, this document facilitates
interoperability by introducing an ESDC scheme to be combined with existing data constructs to cover and preserve
existing data models.
NOTE 2 Annex B includes illustrative examples and references to supporting implementations, intended to
demonstrate approaches that promote interoperability across diverse environments. These references are
provided to assist stakeholders in selecting appropriate solutions that comply with applicable legal obligations and
technical standards, while preserving existing systems.
2 Normative references
The following documents are referred to in the text in such a way that some or all of their content
constitutes requirements of this document. For dated references, only the edition cited applies. For
undated references, the latest edition of the referenced document (including any amendments) applies.
EN 18216:2026, Digital product passport — Data exchange protocols
EN 18219:2026, Digital product passport — Unique identifiers
EN 18220:2026, Digital product passport — Data carriers
EN 18221:2026, Digital product passport — Data storage, archiving, and data persistence
EN 18239:2026, Digital product passport — Access rights management, information system security, and
business confidentiality
3 Terms and definitions
For the purposes of this document, the following terms and definitions apply.
ISO and IEC maintain terminology databases for use in standardization at the following addresses:
— ISO Online browsing platform: available at https://www.iso.org/obp/
— IEC Electropedia: available at https://www.electropedia.org/
3.1
electronically signed data construct
ESDC
structured data set containing the header, payload, signature and optional data fields
3.2
digital product passport
DPP
digital record of product characteristics throughout its life cycle
Note 1 to entry: Example characteristics include environmental sustainability, environmental impact, and
recyclability
3.3
unique product identifier
unique string of characters for the identification of a product that also enables a web link to the DPP
3.4
identity proofing
process by which the Registration Authority (RA) captures and verifies sufficient information to identify
an entity to a specified or understood level of assurance
[SOURCE: ISO/IEC 29115:2013, 3.15]
3.5
level of assurance
description of the strength of entity authentication assurance
Note 1 to entry: ISO/IEC 29115:2013 specifies multiple levels of assurance.
[SOURCE: ISO/IEC 24760-1:2025, 3.4.11]
3.6
digital certificate
certificate
public key information of an entity signed by the certification authority (CA) and thereby rendered
unforgeable
[SOURCE: ISO/IEC 9798-1]
3.7
data carrier
device or medium used to store data as a relay mechanism in an automatic identification and data capture
system
[SOURCE: EN 18220:2026]
3.8
signature
digital signature
data appended to, or a cryptographic transformation of, a data unit that allows the recipient of the data
unit to prove the origin and integrity of the data unit and protect against forgery, e.g. by the recipient
Note 1 to entry: Digital signatures may be used for purposes of authentication, data integrity, and non-repudiation.
[SOURCE: ISO/IEC 19784-1:2018, 4.34]
3.9
unique economic operator identifier
unique string of characters for the identification of an actor involved in a product’s value chain
3.10
additional software
additional application, program, or tool that a user will install or access separately from the default setup
of most smartphones or similar devices to interact with the DPP
EXAMPLE Proprietary applications, plugins or extensions, dedicated apps, specialized middleware, or
customized software readers.
Note 1 to entry: Standard functionalities, such as web browsers, camera-based QR readers, and universal
communication protocols (e.g. DNS, HTTP, HTTPS), are not considered as additional software.
3.11
non-repudiation
ability to prove an action or event has taken place, so that this event or action cannot be repudiated later
[SOURCE: ISO/IEC 27000]
3.12
personally identifiable information
PII
information that can be used in a given context to identify, contact, or locate a single person, or to identify
an individual in context
[SOURCE: ISO 19414:2020, 3.1]
3.13
verifier
entity that performs the verification process
[SOURCE: ISO/IEC 23264-1:2021, 3.27]
3.14
economic operator
manufacturer, authorized representative, importer, distributor, dealer or fulfilment service provider that
places the product onto the market
3.15
controlled DPP data
information on DPP whose access is controlled based on the user’s access rights
Note 1 to entry: User: person who interacts with a system, product or service.
[SOURCE: ISO 26800:2011, 2.10, modified – Notes changed]
3.16
DPP service
means by which DPP data is made accessible or presented
4 General security assumptions for DPP
4.1 General
The DPP provides required information for products. Product information consists of public and
controlled data.
All DPP data shall be protected against unauthorised modification and shall be attributable to a verifiable
source.
The mechanisms ensuring the integrity and authenticity of DPP data shall be independent from the
security mechanisms used for the communication channels over which the data are transmitted.
NOTE 1 The existence of a unique product identifier is a prerequisite for data verifiability.
NOTE 2 ISO 22373, ISO 22380 and ISO 22383 outline principles for addressing physical product fraud, focusing
on authenticity, integrity, and trust for products and documents. They provide guidelines for organizations to
identify and mitigate risks associated with inter alia product fraud, which can range from counterfeiting to
tampering and substitution. The standard emphasizes the importance of understanding the situational context of
fraud, including the motives and behaviours of fraudsters, to develop effective countermeasures such as the
selection of relevant physical authentication solutions. Types of fraud addressed include recreational, situational
context, occasional, occupational, professional and activism fraud and misinformation.
4.2 Actors of the system
Actors within the DPP system are defined in EN 18239:2026.
The unique economic operator identifier is defined in 3.9 in this document and in EN 18219:2026.
All actors accessing controlled DPP data shall be identified by a globally unique identifier.
Authentication processes shall be based on the required level of assurance.
4.3 Access to public DPP data
Access to DPP data, limited to reading purposes, differ from other use cases due to the following
considerations:
— No Authentication Required: Accessing public data shall not require authentication.
— Privacy Considerations: Measures shall be put in place to avoid profiling of users.
— Ease of Use and Scalability: The access control of DPP data should be capable of handling a large
number of requests while maintaining usability and system stability.
— No technological barriers: public DPP data shall be accessible without any additional software.
— Optional Additional Security: Additional security measures shall not prevent access to public DPP
data without additional software.
4.4 Communication
Communication within the DPP context refers to the transmission of product-related information
between stakeholders, ensuring that all involved parties, such as manufacturers, regulators, and
consumers, have access to accurate, relevant and up-to-date data.
The communication of this data shall be secure, using encryption and authentication methods in
accordance with relevant standards to prevent tampering, unauthorized access, or data breaches,
maintaining the integrity and confidentiality of the DPP. For access to public data, no encryption or
authentication mechanisms are required.
The requirements from ETSI EN 319 401:2024, relevant for Trust Service Providers, should be applied to
DPP service providers.
Responsible parties shall establish seamless and interoperable communication channels. These channels
shall enable different systems and actors to exchange DPP data while ensuring compatibility across
various platforms and compliance with both national and international regulatory frameworks as defined
in EN 18216:2026.
4.5 Product identifier as stored in data carrier
The product identifier contained within the data carrier should be, where relevant and appropriate,
protected by security measures to support authenticity and integrity.
Any solution for ensuring the authenticity and integrity of the product identifier shall be fully
interoperable with the unique identifiers as defined in EN 18219:2026.
At least one data carrier on each product shall allow all users to access the public DPP data without the
need for additional software.
DPP data may indicate that the unique identifier is protected and may provide the user with explicit
instructions for authenticating it.
4.6 Data carrier authenticity
The economic operator may secure the data carrier. In such cases, the DPP can include information on
how to inspect the related security feature(s).
Any solution for ensuring the physical authenticity of the physical data carrier shall be fully interoperable
with the data carriers as they are defined in EN 18220:2026.
Such solutions may require additional data carrier(s) and/or data source(s).
The protected data carrier shall allow all users to access the public DPP data without the need for
additional software.
DPP data may indicate that the data carrier(s) are protected and may provide the user with explicit
instructions for authenticating it.
4.7 DPP authenticity and data integrity
A DPP shall be verifiable in terms of authenticity and integrity of the data. Such verification shall be free
of charge and based on interoperable mechanisms in regulated scenarios, e.g. cross border.
All actors providing DPP data shall be authenticated using a mechanism that requires proof of ownership
of a digital certificate issued through an identity proofing process compatible with the provisions of the
relevant legal acts.
Every modification to the DPP data, including its first creation and deletion, shall be bound to the identity
of the authenticated actor performing such modification, through e.g. valid digital certificates, to provide
non-repudiation over the specific modification. Examples of technologies for achieving this are digital
signatures, digital seals, electronic attestation of attributes or ESDCs, based on digital certificates.
Checking the validity and integrity of the DPP data shall be free of charge and without limitations for the
verifier.
A user is not obliged to verify the DPP data.
Any creation, modification, or deletion of data shall be logged in a non-repudiable manner, should be
tamper-proof. Log data integrity shall be provided over time. This should be ensured without the need
for additional supporting documents or offline procedures.
The responsible editor of any change shall be identifiable through a globally unique operator identifier.
Any event that modifies a DPP during its operational phase shall be logged in an audit-proof manner, such
that they can be accessed by the relevant parties.
5 Types of risk and requirements for unique product identifiers, data carriers
and DPP data
5.1 Risk on data security and privacy
5.1.1 General
These subclauses refer to anonymous access to public data of one or many DPPs of interest, when using
common devices, such as smartphones using built-in capabilities, without requiring additional software.
These devices will follow the link enabled by the unique product identifier from the data carrier, as well
as using any kind of online system or software to access DPP data from a server running on behalf of the
economic operator or a DPP service provider.
These subclauses cover authenticated access to controlled data by authorized user groups, including the
performance of CRUD (create, read, update, delete) operations.
5.1.2 Protection of personal data
Implementation shall not gather any personal information from natural persons accessing public data
only.
In case of access to restricted data, authentication information may be requested.
5.1.3 Security of personal data
In case that personal data are gathered for permitted reasons, this data shall be secured against data loss,
disallowed access and against any use not intended and not covered by permitted reasons.
Implementation and/or operator shall provide legally required information, correction and deletion
possibilities for personal data.
DPP service shall not use external analytic tools and shall not include any reference to external
components in the response to the user.
5.1.4 Security of organizational data
Ensuring the security of organizational data is crucial to protect sensitive business information,
intellectual property, and operationa
...