

ISO 37304
(Main)Compliance management systems — Requirements for bodies providing audit and certification of compliance management systems
- Abstract
This standard establishes requirements for certification bodies to follow in order to ensure that certification bodies implement certification programs in a competent, consistent and impartial manner, to promote international recognition of those certification bodies, and to provide confidence in the effectiveness of CMS of certified organizations. This standard may be used as a guideline document for designated use by government departments, certification program owners, accreditation bodies, or others. The requirements of this standard are general guidelines for certification bodies implementing a CMS certification program. This document addresses the additional requirements necessary for the CMS audit process. It covers the planning process, the initial certification, conducting audits, audit time, etc. This standard does not impose requirements on the content of the certification program and its development, nor does it limit the role or choices of the program owner, but it is not appropriate for the content of the program to exclude or conflict with any of the requirements of this standard. This standard applies not only to third-party CMS certification, but many of its provisions may also be used in first- and second-party CMS assessment programs.
- Status
- Not Published
- Technical Committee
- ISO/TC 309 - Governance of organizations
- Drafting Committee
- ISO/TC 309 - Governance of organizations
- Current Stage
- 6000 - International Standard under publication
- Start Date
- 26-Sep-2026
- Completion Date
- 10-Oct-2026
Buy Documents
ISO/FDIS 37304 - Compliance management systems — Requirements for bodies providing audit and certification of compliance management systems
REDLINE ISO/FDIS 37304 - Compliance management systems — Requirements for bodies providing audit and certification of compliance management systems
ISO 37304 is an ISO standard for bodies that audit and certify compliance management systems (CMS). It adds CMS-specific requirements to ISO/IEC 17021-1 so certification bodies can work competently, consistently and impartially, and so certified CMS can inspire confidence. It is not a forensic audit, legal review or financial audit.
What does ISO 37304 specify?
ISO 37304 specifies additional requirements and guidance for bodies that provide audit and certification of CMS, on top of ISO/IEC 17021-1. It is written for certification bodies, but the scope also says it can be used as guidance by government departments, certification program owners, accreditation bodies and others. The document follows the ISO/IEC 17021-1 structure, so readers familiar with that base standard will recognize the flow.
The standard is organized into clauses 1 to 10 and two annexes. Clauses 4 to 10 cover the principles, general requirements, structure, resources, information handling, audit process and the certification body’s own management system.
| Annex | What it covers |
|---|---|
| Annex A, informative | Further competence considerations for CMS auditing and certification |
| Annex B, normative | CMS audit time |
ISO 37304 also says that it does not set the content of a certification program or its development. A program owner keeps that role, but the program content should not exclude or conflict with the requirements in this standard.
What are the key requirements of ISO 37304?
ISO 37304 keeps the base certification-body requirements from ISO/IEC 17021-1 and adds CMS-specific controls where CMS auditing needs more detail. The most important practical points are about competence, scope definition, audit planning, confidentiality, audit time and the way certification is described.
Base requirements still apply - Clauses 4, 5, 6, 7.3 to 7.5, 8.1, 8.5 and much of Clause 9 and Clause 10 defer to ISO/IEC 17021-1. In practice, a CMS certification body still needs the usual controls for legal matters, impartiality, liability, structure, outsourcing, public information, audit process, appeals, complaints and management-system operation.
CMS competence has to be defined function by function - Clause 7.1 requires the certification body to define competence requirements for each certification function, and Annex A links those functions to the knowledge needed. This matters because CMS auditing depends on more than generic audit skill: the team must also understand the organization’s compliance obligations, compliance risks and CMS operation.
The audit team needs CMS-specific knowledge - Clause 7.2.1 requires audit teams to understand the requirements of ISO 37301 and the relationship between those requirements. They also need knowledge of the organization’s context, laws, regulations and other requirements, compliance risk assessment and controls, and how a CMS is established and implemented. The standard also says the team members do not all need the same competence, but their combined competence must be enough for the audit objectives.
Other personnel also need CMS competence - Clause 7.2.2 covers people who review applications, select audit team members, determine audit time, review reports and make certification decisions. This is important because certification quality depends not only on auditors, but also on the people who plan the audit and decide on certification.
Certification documents must be specific and claims must not mislead - Clause 8.2.2 requires certification documents to identify the relevant compliance risk areas within scope, such as anti-bribery, anti-trust or money laundering. Clause 8.3.2 requires legally enforceable arrangements to prevent claims that go beyond the certificate, such as saying the client meets all compliance obligations or that all business activities comply with laws and regulations.
Confidential or sensitive information has to be handled before the audit - Clause 8.4.2 requires the certification body to ask in advance whether any CMS-related information cannot be shown to the audit team. If the audit objectives cannot be met without that information, the audit cannot proceed until access arrangements are made. For users, that means document access and confidentiality questions need to be resolved early.
The audit scope, site model and sampling approach have to be justified - Clause 9.1.3 requires the client to define the organizational boundaries of the CMS and the compliance obligations in scope. Clause 9.1.5 allows sample-based multi-site certification only when sites share a centrally managed CMS, are included in internal audits and are covered by management review. Sampling has to reflect site differences, risk and non-compliance history, so the certification body can defend why the chosen sites were representative.
Stage 1 has a specific CMS purpose - Clause 9.3.2.1 requires stage 1 to review the design of the CMS, the documented information required by ISO 37301, the compliance policy and objectives, and the client’s readiness for stage 2. The certification body also has to confirm that the compliance risk assessment covers all compliance obligations in scope. This reduces the chance of finding basic design gaps during the main audit.
Audit time is based on CMS effective personnel, then adjusted for risk factors - Annex B makes audit time depend on CMS effective personnel and then adjusts it for factors such as the number of compliance obligations, legal context, the type and impact of non-compliance, CMS maturity, number of sites, outsourcing, ICT use, centralized control, language needs and CMS complexity. In practice, audit duration is meant to match the actual compliance burden, not just headcount.
What terms does ISO 37304 define?
ISO 37304 uses the definitions from ISO/IEC 17000, ISO 37301 and ISO/IEC 17021-1. The most useful terms for readers are these:
- Compliance management systems (CMS) - The management system an organization uses to establish, operate and improve compliance with its compliance policy and applicable requirements.
- Certification audit - An independent audit carried out to certify a client’s management system; in this document, “audit” is used for third-party certification audit.
- CMS effective personnel - Personnel who materially contribute to the effectiveness of the CMS or affect compliance performance; this count is used to determine audit time.
- Audit time - The time needed to plan and perform a complete and effective audit of the client organization’s management system.
Who uses ISO 37304?
ISO 37304 is mainly used by certification bodies that audit and certify CMS. They use it to define competence, plan audits, choose teams, set audit time, issue certification documents and manage surveillance, re-certification, appeals and complaints.
Accreditation bodies and certification program owners use ISO 37304 to align CMS certification programs with a common set of expectations. Government departments and other designated users can also use it as a guideline when they want a CMS certification approach with clear competence and audit-time rules.
It is relevant across public, private and civil sector organizations because Clause 7.2 and Annex B both refer to the organization’s context, compliance obligations and compliance risks. It can also support first- and second-party CMS assessment programs where organizations want to use the same auditing logic internally.
What changed in ISO 37304 from the previous edition?
ISO 37304 is the first edition and it cancels and replaces ISO/IEC TS 17021-13:2021. The main change stated in the foreword is that the content of ISO/IEC TS 17021-13:2021 was incorporated into Clause 7.2 on competence requirements, with one modification moved into Clause 7.2.1.2 as a requirement.
Which standards are used with ISO 37304?
- ISO/IEC 17000 - Provides conformity assessment vocabulary and general principles used by the document.
- ISO/IEC 17021-1 - Supplies the base requirements for bodies providing audit and certification of management systems; ISO 37304 adds CMS-specific requirements on top of it.
- ISO 37301 - Gives the CMS requirements that certification audits assess against.
- ISO 19011 - Is mentioned in a note as the source for auditing principles.
- ISO 50003:2021 - Is used as the source for the adapted term CMS effective personnel.
What does the ISO 37304 document contain?
ISO 37304 contains a competence model for CMS audit and certification functions in Clause 7 and Annex A, including a knowledge matrix in Table A.1. It also contains a normative audit-time method in Annex B, with Table B.1 setting initial audit-time bands by effective personnel and Clause B.4 listing the factors that can adjust the time.
The process clauses cover application review, audit-programme scope, multi-site sampling, combined audits, stage 1 and stage 2 certification, surveillance, re-certification, special audits, suspension or withdrawal, appeals, complaints and client records. The information clauses cover public information, certification documents, use of marks, confidentiality and information exchange.
The document also includes the certification body’s own management system requirements in Clause 10. Taken together, it is a practical rule set for planning and running CMS certification in a way that is traceable, impartial and defensible.
Relations
- Effective Date
- 23-May-2026
Buy Documents
ISO/FDIS 37304 - Compliance management systems — Requirements for bodies providing audit and certification of compliance management systems
REDLINE ISO/FDIS 37304 - Compliance management systems — Requirements for bodies providing audit and certification of compliance management systems
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.

Bureau Veritas
Bureau Veritas is a world leader in laboratory testing, inspection and certification services.
DNV
DNV is an independent assurance and risk management provider.
Sponsored listings
Frequently Asked Questions
ISO 37304 is a draft published by the International Organization for Standardization (ISO). Its full title is "Compliance management systems — Requirements for bodies providing audit and certification of compliance management systems". This standard covers: This standard establishes requirements for certification bodies to follow in order to ensure that certification bodies implement certification programs in a competent, consistent and impartial manner, to promote international recognition of those certification bodies, and to provide confidence in the effectiveness of CMS of certified organizations. This standard may be used as a guideline document for designated use by government departments, certification program owners, accreditation bodies, or others. The requirements of this standard are general guidelines for certification bodies implementing a CMS certification program. This document addresses the additional requirements necessary for the CMS audit process. It covers the planning process, the initial certification, conducting audits, audit time, etc. This standard does not impose requirements on the content of the certification program and its development, nor does it limit the role or choices of the program owner, but it is not appropriate for the content of the program to exclude or conflict with any of the requirements of this standard. This standard applies not only to third-party CMS certification, but many of its provisions may also be used in first- and second-party CMS assessment programs.
This standard establishes requirements for certification bodies to follow in order to ensure that certification bodies implement certification programs in a competent, consistent and impartial manner, to promote international recognition of those certification bodies, and to provide confidence in the effectiveness of CMS of certified organizations. This standard may be used as a guideline document for designated use by government departments, certification program owners, accreditation bodies, or others. The requirements of this standard are general guidelines for certification bodies implementing a CMS certification program. This document addresses the additional requirements necessary for the CMS audit process. It covers the planning process, the initial certification, conducting audits, audit time, etc. This standard does not impose requirements on the content of the certification program and its development, nor does it limit the role or choices of the program owner, but it is not appropriate for the content of the program to exclude or conflict with any of the requirements of this standard. This standard applies not only to third-party CMS certification, but many of its provisions may also be used in first- and second-party CMS assessment programs.
ISO 37304 is classified under the following ICS (International Classification for Standards) categories: 03.100.02 - Governance and ethics; 03.100.70 - Management systems; 03.120.20 - Product and company certification. Conformity assessment. The ICS classification helps identify the subject area and facilitates finding related standards.
ISO 37304 has the following relationships with other standards: It is inter standard links to ISO/IEC TS 17021-13:2021. Understanding these relationships helps ensure you are using the most current and applicable version of the standard.
ISO 37304 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
FINAL DRAFT
International
Standard
ISO/FDIS 37304
ISO/TC 309
Compliance management
Secretariat: BSI
systems — Requirements for bodies
Voting begins on:
providing audit and certification of
2026-07-31
compliance management systems
Voting terminates on:
2026-09-25
Systèmes de management de la conformité — Exigences
pour les organismes d’audit et de certification des système de
management de la conformité
Member bodies are requested to consult relevant national interests in
ISO/CASCO before casting their ballot to the e-Balloting application.
RECIPIENTS OF THIS DRAFT ARE INVITED TO SUBMIT,
WITH THEIR COMMENTS, NOTIFICATION OF ANY
RELEVANT PATENT RIGHTS OF WHICH THEY ARE AWARE
AND TO PROVIDE SUPPOR TING DOCUMENTATION.
IN ADDITION TO THEIR EVALUATION AS
BEING ACCEPTABLE FOR INDUSTRIAL, TECHNO
LOGICAL, COMMERCIAL AND USER PURPOSES, DRAFT
INTERNATIONAL STANDARDS MAY ON OCCASION HAVE
TO BE CONSIDERED IN THE LIGHT OF THEIR POTENTIAL
TO BECOME STAN DARDS TO WHICH REFERENCE MAY BE
MADE IN NATIONAL REGULATIONS.
Reference number
ISO/FDIS 37304:2026(en) © ISO 2026
FINAL DRAFT
ISO/FDIS 37304:2026(en)
International
Standard
ISO/FDIS 37304
ISO/TC 309
Compliance management
Secretariat: BSI
systems — Requirements for bodies
Voting begins on:
providing audit and certification of
compliance management systems
Voting terminates on:
Systèmes de management de la conformité — Exigences
pour les organismes d’audit et de certification des système de
management de la conformité
Member bodies are requested to consult relevant national interests in
ISO/CASCO before casting their ballot to the e-Balloting application.
RECIPIENTS OF THIS DRAFT ARE INVITED TO SUBMIT,
WITH THEIR COMMENTS, NOTIFICATION OF ANY
RELEVANT PATENT RIGHTS OF WHICH THEY ARE AWARE
AND TO PROVIDE SUPPOR TING DOCUMENTATION.
© ISO 2026
IN ADDITION TO THEIR EVALUATION AS
All rights reserved. Unless otherwise specified, or required in the context of its implementation, no part of this publication may
BEING ACCEPTABLE FOR INDUSTRIAL, TECHNO
LOGICAL, COMMERCIAL AND USER PURPOSES, DRAFT
be reproduced or utilized otherwise in any form or by any means, electronic or mechanical, including photocopying, or posting on
INTERNATIONAL STANDARDS MAY ON OCCASION HAVE
the internet or an intranet, without prior written permission. Permission can be requested from either ISO at the address below
TO BE CONSIDERED IN THE LIGHT OF THEIR POTENTIAL
or ISO’s member body in the country of the requester.
TO BECOME STAN DARDS TO WHICH REFERENCE MAY BE
MADE IN NATIONAL REGULATIONS.
ISO copyright office
CP 401 • Ch. de Blandonnet 8
CH-1214 Vernier, Geneva
Phone: +41 22 749 01 11
Email: copyright@iso.org
Website: www.iso.org
Published in Switzerland Reference number
ISO/FDIS 37304:2026(en) © ISO 2026
ii
ISO/FDIS 37304:2026(en)
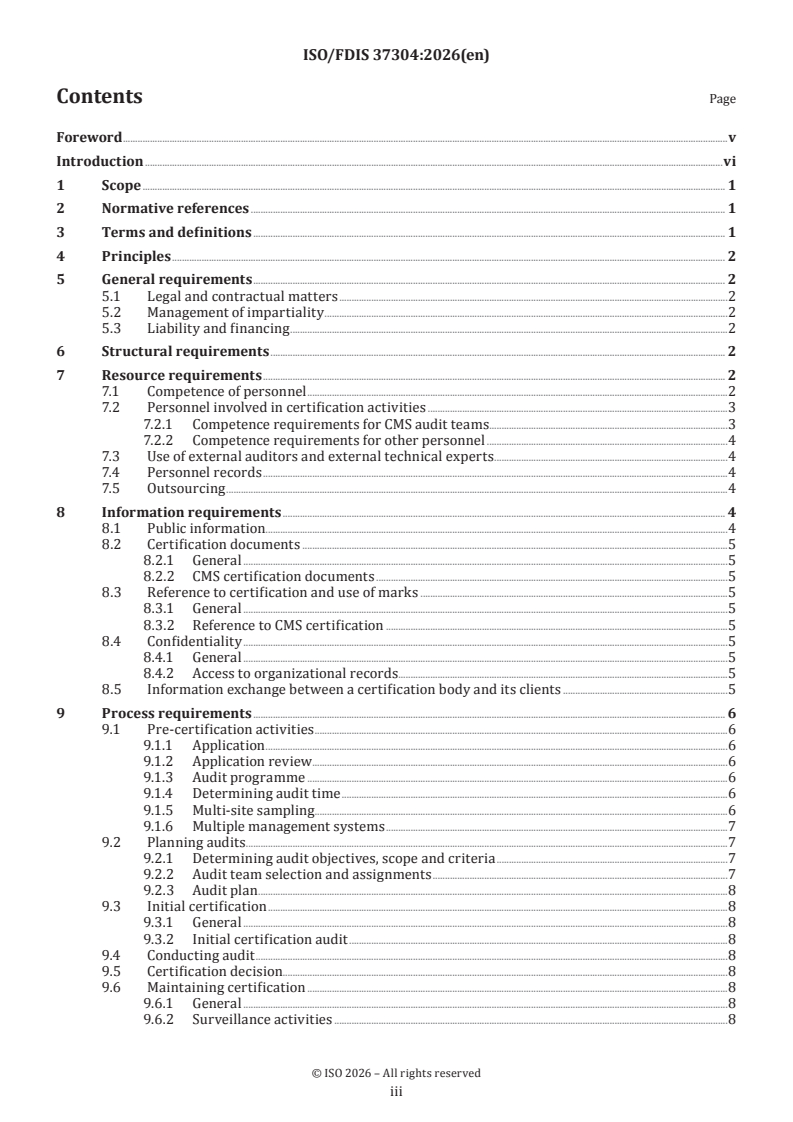
Contents Page
Foreword .v
Introduction .vi
1 Scope . 1
2 Normative references . 1
3 Terms and definitions . 1
4 Principles . 2
5 General requirements . 2
5.1 Legal and contractual matters .2
5.2 Management of impartiality .2
5.3 Liability and financing .2
6 Structural requirements . 2
7 Resource requirements . 2
7.1 Competence of personnel .2
7.2 Personnel involved in certification activities .3
7.2.1 Competence requirements for CMS audit teams.3
7.2.2 Competence requirements for other personnel .4
7.3 Use of external auditors and external technical experts .4
7.4 Personnel records .4
7.5 Outsourcing .4
8 Information requirements . 4
8.1 Public information . .4
8.2 Certification documents .5
8.2.1 General .5
8.2.2 CMS certification documents .5
8.3 Reference to certification and use of marks .5
8.3.1 General .5
8.3.2 Reference to CMS certification .5
8.4 Confidentiality .5
8.4.1 General .5
8.4.2 Access to organizational records.5
8.5 Information exchange between a certification body and its clients .5
9 Process requirements . 6
9.1 Pre-certification activities .6
9.1.1 Application .6
9.1.2 Application review . .6
9.1.3 Audit programme .6
9.1.4 Determining audit time .6
9.1.5 Multi-site sampling . .6
9.1.6 Multiple management systems .7
9.2 Planning audits .7
9.2.1 Determining audit objectives, scope and criteria .7
9.2.2 Audit team selection and assignments .7
9.2.3 Audit plan .8
9.3 Initial certification .8
9.3.1 General .8
9.3.2 Initial certification audit .8
9.4 Conducting audit .8
9.5 Certification decision . . .8
9.6 Maintaining certification .8
9.6.1 General .8
9.6.2 Surveillance activities .8
iii
ISO/FDIS 37304:2026(en)
9.6.3 Re-certification .8
9.6.4 Special audits .8
9.6.5 Suspending withdrawing or reducing the scope of certification .9
9.7 Appeals .9
9.8 Complaints.9
9.9 Client records .9
10 Management system requirements for certification bodies . 9
Annex A (informative) Further competence consideration for CMS auditing and certification .10
Annex B (normative) CMS audit time . 14
Bibliography . 17
iv
ISO/FDIS 37304:2026(en)
Foreword
ISO (the International Organization for Standardization) is a worldwide federation of national standards
bodies (ISO member bodies). The work of preparing International Standards is normally carried out through
ISO technical committees. Each member body interested in a subject for which a technical committee
has been established has the right to be represented on that committee. International organizations,
governmental and non-governmental, in liaison with ISO, also take part in the work. ISO collaborates closely
with the International Electrotechnical Commission (IEC) on all matters of electrotechnical standardization.
The procedures used to develop this document and those intended for its further maintenance are described
in the ISO/IEC Directives, Part 1. In particular, the different approval criteria needed for the different types
of ISO documents should be noted. This document was drafted in accordance with the editorial rules of the
ISO/IEC Directives, Part 2 (see www.iso.org/directives).
ISO draws attention to the possibility that the implementation of this document may involve the use of (a)
patent(s). ISO takes no position concerning the evidence, validity or applicability of any claimed patent
rights in respect thereof. As of the date of publication of this document, ISO had not received notice of (a)
patent(s) which may be required to implement this document. However, implementers are cautioned that
this may not represent the latest information, which may be obtained from the patent database available at
www.iso.org/patents. ISO shall not be held responsible for identifying any or all such patent rights.
Any trade name used in this document is information given for the convenience of users and does not
constitute an endorsement.
For an explanation of the voluntary nature of standards, the meaning of ISO specific terms and expressions
related to conformity assessment, as well as information about ISO's adherence to the World Trade
Organization (WTO) principles in the Technical Barriers to Trade (TBT), see www.iso.org/iso/foreword.html.
This document was prepared by Technical Committee ISO/TC 309, Governance of organizations, in
collaboration with ISO/CASCO, Committee on conformity assessment.
This first edition cancels and replaces ISO/IEC TS 17021-13:2021, which has been technically revised.
The main changes are as follows:
— The content of ISO/IEC TS 17021-13:2021 has been incorporated verbatim as 7.2 on competence
requirements, with one modification to 5.1.2, NOTE 1: the text has been incorporated into 7.2.1.2 as a
requirement in the final paragraph.
Any feedback or questions on this document should be directed to the user’s national standards body. A
complete listing of these bodies can be found at www.iso.org/members.html.
v
ISO/FDIS 37304:2026(en)
Introduction
Certification of the compliance management systems (CMS) of an organization is one means of providing
assurance that the organization has implemented a CMS in accordance with its compliance policy and
internationally accepted principles for measures to ensure that business activities are conducted in
accordance with applicable laws and regulations.
[1]
ISO/IEC 17021-1 sets out requirements for bodies which are referred to as “certification bodies providing
audit and certification of management systems". This document sets out requirements in addition to those
[1]
in ISO/IEC 17021-1 intended to promote international recognition of those certification bodies, and to
provide confidence in the effectiveness of CMS of certified organizations. The text in this document follows
[1]
the structure of ISO/IEC 17021-1 .
[1]
The CMS certification in accordance with ISO/IEC 17021-1 and this document is not a forensic audit nor
a legal review or financial audit. The certification confirms that a client’s CMS meets the requirements
[2]
specified in ISO 37301 .
vi
FINAL DRAFT International Standard ISO/FDIS 37304:2026(en)
Compliance management systems — Requirements for bodies
providing audit and certification of compliance management
systems
1 Scope
This document specifies requirements and provides guidance for bodies providing audit and certification of
compliance management systems (CMS), in addition to the requirements contained within ISO/IEC 17021-1
[1]
. Observance of these requirements is intended to ensure that certification bodies provide audit and
certification in a competent, consistent and impartial manner.
2 Normative references
The following documents are referred to in the text in such a way that some or all of their content constitutes
requirements of this document. For dated references, only the edition cited applies. For undated references,
the latest edition of the referenced document (including any amendments) applies.
ISO/IEC 17000, Conformity assessment — Vocabulary and general principles
ISO/IEC 17021-1:2015, Conformity assessment — Requirements for bodies providing audit and certification of
management systems — Part 1: Requirements
ISO/IEC 17021-1, Conformity assessment — Requirements for bodies providing audit and certification of
management systems — Part 1: Requirements
ISO 37301:2021, Compliance management systems — Requirements with guidance for use
ISO 37301, Compliance management systems — Requirements with guidance for use
3 Terms and definitions
For the purposes of this document, the terms and definitions given in ISO/IEC 17000, ISO 37301 and
ISO/IEC 17021-1 apply.
ISO and IEC maintain terminology databases for use in standardization at the following addresses:
— ISO Online browsing platform: available at https:// www .iso .org/ obp
— IEC Electropedia: available at https:// www .electropedia .org/
3.1
certification audit
audit carried out by an auditing organization independent of the client and the parties that rely on
certification, for the purpose of certifying the client's management system
Note 1 to entry: In the definitions which follow, the term “audit” has been used for simplicity to refer to third-party
certification audit.
Note 2 to entry: Certification audits include initial, surveillance, re-certification audits, and can also include special
audits.
Note 3 to entry: Certification audits are typically conducted by audit teams of those bodies providing certification of
conformity to the requirements of management system standards.
ISO/FDIS 37304:2026(en)
Note 4 to entry: A joint audit is when two or more auditing organizations cooperate to audit a single client.
Note 5 to entry: A combined audit is when a client is being audited against the requirements of two or more management
systems standards together.
Note 6 to entry: An integrated audit is when a client has integrated the application of requirements of two or more
management systems standards into a single management system and is being audited against more than one
standard.
[3]
[SOURCE: ISO/IEC 17021-1:2015 , 3.4]
3.2
CMS effective personnel
personnel who materially contribute to the effectiveness of the compliance management system (CMS) or
impact compliance performance
Note 1 to entry: CMS effective personnel is not necessarily the total number of employees (headcount).
Note 2 to entry: The CMS effective personnel number is a factor used to determine the audit time (3.3).
[4]
[SOURCE: ISO 50003:2021 , 3.5 modified — The term “EnMS” has been replaced by “CMS” throughout the
entry; "or impact energy performance” has been replaced with “or impact compliance performance”.]
3.3
audit time
time needed to plan and perform a complete and effective audit of the client organization’s management
system
[3]
[SOURCE: ISO/IEC 17021-1:2015 , 3.16]
4 Principles
The principles of ISO/IEC 17021-1:2015, 4 apply.
5 General requirements
5.1 Legal and contractual matters
The requirements of ISO/IEC 17021-1:2015, 5.1 apply.
5.2 Management of impartiality
The requirements of ISO/IEC 17021-1:2015, 5.2 apply.
5.3 Liability and financing
The requirements of ISO/IEC 17021-1:2015, 5.3 apply.
6 Structural requirements
The requirements of ISO/IEC 17021-1:2015, 6 apply.
7 Resource requirements
7.1 Competence of personnel
The certification body shall define the competence requirements for each certification function as referenced
in ISO/IEC 17021-1:2015, Table A.1. When defining these competence requirements, the certification body
ISO/FDIS 37304:2026(en)
shall take into account all the requirements specified in ISO/IEC 17021-1, as well as those specified in 7.2 of
this document.
NOTE 1 Annex A provides further considerations for competencies for personnel involved in specific certification
functions.
[5]
NOTE 2 Information on the principles of auditing is provided in ISO 19011 .
7.2 Personnel involved in certification activities
7.2.1 Competence requirements for CMS audit teams
7.2.1.1 General
All members of the CMS audit team shall have a level of competence that includes the generic competence
described in ISO/IEC 17021-1 and understand the requirements of ISO 37301 and the relationship between
those requirements, as well as the knowledge described in 7.2.1.2 to 7.2.1.5.
The competence requirements specified in 7.2.1.2 to 7.2.1.5 shall apply within the scope of the CMS to be
audited.
It is not necessary for each member of the audit team to have the same competence; however, the collective
competence of the audit team shall be sufficient to achieve the audit objectives.
7.2.1.2 Context of the organization
The audit team shall have knowledge of the context in which the organization operates. The audit team shall
be able to understand the business activities and processes of the organization in so far as they relate to the
compliance obligations and compliance risks arising from those activities and processes.
The audit team shall have the knowledge and skills necessary to conduct research related to the organization
to identify and understand applicable compliance obligations and risks.
7.2.1.3 Laws, regulations and other requirements
The audit team shall have knowledge and understanding concerning different legal systems, laws and
regulations. The audit team shall have the knowledge and skills to understand different types of legal texts
and to understand their relevance for the compliance obligations of the organization.
The audit team shall have knowledge about the legal framework in which the
...
Style Definition: Heading 1: Indent: Left: 0 cm, First
ISO/DISFDIS 37304
line: 0 cm
ISO/TC 309
Style Definition: Heading 2: Font: Bold, Indent: Left: 0
cm, First line: 0 cm
Secretariat: BSI
Style Definition: Heading 3: Font: Bold, Indent: Left: 0
cm, First line: 0 cm
Date: 2026-05-2807-16
Style Definition: Heading 4: Font: Bold, Indent: Left: 0
cm, First line: 0 cm
Style Definition: Heading 5: Font: Bold, Indent: Left: 0
cm, First line: 0 cm
Style Definition: Heading 6: Font: Bold
Style Definition: IntroHeading1: Font: Bold, Indent:
Compliance management systems — Requirements for bodies
Left: 0 cm, First line: 0 cm
providing audit and certification of compliance management systems
Style Definition: IntroHeading2: Font: Bold, Indent:
Left: 0 cm, First line: 0 cm
Systèmes de management de la conformité — Exigences pour les organismes d’audit et de certification des
Style Definition: IntroHeading3: Font: Bold, Indent:
système de management de la conformité
Left: 0 cm, First line: 0 cm
Style Definition: IntroHeading4: Font: Bold, Indent:
Left: 0 cm, First line: 0 cm
Style Definition: IntroHeading5: Font: Bold, Indent:
Left: 0 cm, First line: 0 cm
Style Definition: IntroHeading6
Style Definition: IntroHeading7
Style Definition: IntroHeading8
Style Definition: IntroHeading9
DISFDIS stage
Style Definition: ANNEX
Style Definition: Key Text
Style Definition: Key Title
Style Definition: List Continue 1
Style Definition: TermNum2: Font: Bold, Indent: Left:
0 cm, First line: 0 cm
Style Definition: TermNum3: Font: Bold, Indent: Left:
0 cm, First line: 0 cm
Style Definition: TermNum4: Font: Bold, Indent: Left:
0 cm, First line: 0 cm
Style Definition: TermNum5: Font: Bold, Indent: Left:
0 cm, First line: 0 cm
Style Definition: TermNum6: Font: Bold
Style Definition: Body Text
Style Definition: boxedText
Style Definition: Boxed List Continue 1
Style Definition: boxedTitle
VVototiinngg b beeggiinnss on on:: 22002255--1122--1166
Style Definition: FooterCentered
VVootintingg te termrmiinnaatetess o onn:: 2 2002266--0033--1100
Style Definition: FooterPageNumber
Style Definition: FooterPageRomanNumber
Style Definition: FooterCenteredContinued
MMMememembbbererer b b booodddiiieeesss ar ar are re re reqeqequuueeessstttededed t t tooo cccooonnnsssuuultltlt r r relevelevelevanananttt n n natatatiiiooonnnal al al iiinnntttererereeessstttsss iiinnn I I ISSSOOO///CCCAAASSSCCCOOO b b befoefoeforrre ce ce caaassstttiiinnnggg t t thhheieieirrr
Style Definition: TPS Markup Base
bbbaaallllllooot tot tot to th th theee e e e---BBBaaalllllloootttinininggg a a apppppplllicaicaicatttioioionnn.
ISO/DISFDIS 37304:2026(en)
All rights reserved. Unless otherwise specified, or required in the context of its implementation, no part of this publication
may be reproduced or utilized otherwise in any form or by any means, electronic or mechanical, including photocopying,
or posting on the internet or an intranet, without prior written permission. Permission can be requested from either ISO
at the address below or ISO’s member body in the country of the requester.
ISO copyright office
CP 401 • Ch. de Blandonnet 8
CH-1214 Vernier, Geneva
Phone: + 41 22 749 01 11
Formatted: French (Switzerland)
E-mail: copyright@iso.org
Website: www.iso.org
Published in Switzerland
ii
ISO/DISFDIS 37304:2026(en)
Contents
Foreword . iii
Introduction . iii
Scope . iii
Normative references . iii
Terms and definitions . iii
Principles. iii
General requirements . iii
Legal and contractual matters . iii
Management of impartiality . iii
Liability and financing . iii
Structural requirements . iii
Resource requirements . iii
Competence of personnel . iii
Personnel involved in certification activities . iii
Use of external auditors and external technical experts . iii
Personnel records . iii
Outsourcing . iii
Information requirements . iii
Public information . iii
Certification documents . iii
Reference to certification and use of marks . iii
Confidentiality . iii
Information exchange between a certification body and its clients . iii
Process requirements . iii
Pre-certification activities. iii
Planning audits. iii
Initial certification . iii
Conducting audit . iii
Certification decision . iii
Maintaining certification . iii
Appeals . iii
Complaints . iii
Client records . iii
Management system requirements for certification bodies . iii
(informative) Further competence consideration for CMS auditing and certification. iii
(normative) CMS audit time . iii
Bibliography . iii
Foreword . v
Introduction . vi
1 Scope . 1
2 Normative references . 1
3 Terms and definitions . 1
4 Principles . 2
iii
ISO/DISFDIS 37304:2026(en)
5 General requirements . 2
5.1 Legal and contractual matters . 2
5.2 Management of impartiality . 2
5.3 Liability and financing . 2
6 Structural requirements . 2
7 Resource requirements . 2
7.1 Competence of personnel . 2
7.2 Personnel involved in certification activities . 3
7.3 Use of external auditors and external technical experts . 4
7.4 Personnel records . 4
7.5 Outsourcing . 4
8 Information requirements . 5
8.1 Public information. 5
8.2 Certification documents . 5
8.3 Reference to certification and use of marks . 5
8.4 Confidentiality . 5
8.5 Information exchange between a certification body and its clients . 5
9 Process requirements . 6
9.1 Pre-certification activities . 6
9.2 Planning audits . 7
9.3 Initial certification . 8
9.4 Conducting audit . 8
9.5 Certification decision . 8
9.6 Maintaining certification. 8
9.7 Appeals . 9
9.8 Complaints . 9
9.9 Client records . 9
10 Management system requirements for certification bodies . 9
Annex A (informative) Further competence consideration for CMS auditing and certification . 10
Annex B (normative) CMS audit time . 14
Bibliography . 17
iv
ISO/DISFDIS 37304:2026(en)
Foreword
ISO (the International Organization for Standardization) is a worldwide federation of national standards
bodies (ISO member bodies). The work of preparing International Standards is normally carried out through
ISO technical committees. Each member body interested in a subject for which a technical committee has been
established has the right to be represented on that committee. International organizations, governmental and
non-governmental, in liaison with ISO, also take part in the work. ISO collaborates closely with the
International Electrotechnical Commission (IEC) on all matters of electrotechnical standardization.
The procedures used to develop this document and those intended for its further maintenance are described
in the ISO/IEC Directives, Part 1. In particular, the different approval criteria needed for the different types of
ISO documents should be noted. This document was drafted in accordance with the editorial rules of the
ISO/IEC Directives, Part 2 (see www.iso.org/directives).
ISO draws attention to the possibility that the implementation of this document may involve the use of (a)
patent(s). ISO takes no position concerning the evidence, validity or applicability of any claimed patent rights
in respect thereof. As of the date of publication of this document, ISO had not received notice of (a) patent(s)
which may be required to implement this document. However, implementers are cautioned that this may not
represent the latest information, which may be obtained from the patent database available at
www.iso.org/patents. ISO shall not be held responsible for identifying any or all such patent rights.
Any trade name used in this document is information given for the convenience of users and does not
constitute an endorsement.
For an explanation of the voluntary nature of standards, the meaning of ISO specific terms and expressions
related to conformity assessment, as well as information about ISO's adherence to the World Trade
Organization (WTO) principles in the Technical Barriers to Trade (TBT), see www.iso.org/iso/foreword.html.
This document was prepared by Technical Committee ISO/TC 309, Governance of organizations, in
collaboration with ISO/CASCO, Committee on conformity assessment.
This first edition cancels and replaces ISO/IEC TS 17021-13:2021, which has been technically revised.
The main changes are as follows:
— The content of ISO/IEC TS 17021-13:2021 has been incorporated verbatim as 7.2 on competence
requirements, with one modification to 5.1.2, NOTE 1: the text has been incorporated into 7.2.1.2 as a
requirement in the final paragraph.
Any feedback or questions on this document should be directed to the user’s national standards body. A
complete listing of these bodies can be found at www.iso.org/members.html.
v
ISO/DISFDIS 37304:2026(en)
Introduction
Certification of the compliance management systems (CMS) of an organization is one means of providing
assurance that the organization has implemented a CMS in accordance with its compliance policy and
internationally accepted principles for measures to ensure that business activities are conducted in
accordance with applicable laws and regulations.
ISO/IEC 17021-1 sets out requirements for bodies which are referred to as “certification bodies providing
audit and certification of management systems". This document sets out requirements in addition to those in
ISO/IEC 17021-1 intended to promote international recognition of those certification bodies, and to provide
confidence in the effectiveness of CMS of certified organizations. The text in this document follows the
structure of ISO/IEC 17021-1.
The CMS certification in accordance with ISO/IEC 17021-1 and this document is not a forensic audit nor a legal
review or financial audit. The certification confirms that a client’s CMS meets the requirements specified in
ISO 37301.
vi
ISO/DISFDIS 37304:2026(en)
Compliance management systems — Requirements for bodies
providing audit and certification of compliance management systems
1 Scope
This document specifies requirements and provides guidance for bodies providing audit and certification of
compliance management systems (CMS), in addition to the requirements contained within ISO/IEC 17021-1.
Observance of these requirements is intended to ensure that certification bodies provide audit and
certification in a competent, consistent and impartial manner.
2 Normative references
The following documents are referred to in the text in such a way that some or all of their content constitutes
requirements of this document. For dated references, only the edition cited applies. For undated references,
the latest edition of the referenced document (including any amendments) applies.
ISO/IEC 17000, Conformity assessment — Vocabulary and general principles
ISO/IEC 17021-1:2015, Conformity assessment — Requirements for bodies providing audit and certification of
management systems — Part 1: Requirements
ISO/IEC 17021-1, Conformity assessment — Requirements for bodies providing audit and certification of
management systems — Part 1: Requirements
ISO 37301:2021, Compliance management systems — Requirements with guidance for use
ISO 37301, Compliance management systems — Requirements with guidance for use
3 Terms and definitions
For the purposes of this document, the terms and definitions given in ISO/IEC 17000, ISO 37301 and ISO/IEC
17021-1 apply.
ISO and IEC maintain terminology databases for use in standardization at the following addresses:
— ISO Online browsing platform: available at https://www.iso.org/obphttps://www.iso.org/obp
— IEC Electropedia: available at https://www.electropedia.org/
3.1
certification audit
audit carried out by an auditing organization independent of the client and the parties that rely on
certification, for the purpose of certifying the client's management system
Note 1 to entry: In the definitions which follow, the term “audit” has been used for simplicity to refer to third-party
certification audit.
Note 2 to entry: Certification audits include initial, surveillance, re-certification audits, and can also include special audits.
Note 3 to entry: Certification audits are typically conducted by audit teams of those bodies providing certification of
conformity to the requirements of management system standards.
Note 4 to entry: A joint audit is when two or more auditing organizations cooperate to audit a single client.
ISO/DISFDIS 37304:2026(en)
Note 5 to entry: A combined audit is when a client is being audited against the requirements of two or more management
systems standards together.
Note 6 to entry: An integrated audit is when a client has integrated the application of requirements of two or more
management systems standards into a single management system and is being audited against more than one standard.
[SOURCE: ISO/IEC 17021-1:2015, 3.4]
3.2
CMS effective personnel
personnel who materially contribute to the effectiveness of the compliance management system (CMS) or
impact compliance performance
Note 1 to entry: CMS effective personnel is not necessarily the total number of employees (headcount).
Note 2 to entry: The CMS effective personnel number is a factor used to determine the audit time (3.3).
[SOURCE: ISO 50003:2021, 3.5 modified — The term “EnMS” has been replaced by “CMS” throughout the
entry; "or impact energy performance” has been replaced with “or impact compliance performance”.]
3.3
audit time
time needed to plan and perform a complete and effective audit of the client organization’s management
system
[SOURCE: ISO/IEC 17021-1:2015, 3.16]
4 Principles
The principles of ISO/IEC 17021-1:2015, 4 apply.
5 General requirements
5.1 Legal and contractual matters
The requirements of ISO/IEC 17021-1:2015, 5.1 apply.
5.2 Management of impartiality
The requirements of ISO/IEC 17021-1:2015, 5.2 apply.
5.3 Liability and financing
The requirements of ISO/IEC 17021-1:2015, 5.3 apply.
6 Structural requirements
The requirements of ISO/IEC 17021-1:2015, 6 apply.
7 Resource requirements
7.1 Competence of personnel
The certification body shall define the competence requirements for each certification function as referenced
in ISO/IEC 17021-1:2015, Table A.1. When defining these competence requirements, the certification body
ISO/DISFDIS 37304:2026(en)
shall take into account all the requirements specified in ISO/IEC 17021-1, as well as those specified in Clause
7.2 of this document.
NOTE 1 Annex A provides further considerations for competencies for personnel involved in specific certification
functions.
NOTE 2 Information on the principles of auditing is provided in ISO 19011.
7.2 Personnel involved in certification activities
7.2.1 Competence requirements for CMS audit teams
7.2.1.1 General
All members of the CMS audit team shall have a level of competence that includes the generic competence
described in ISO/IEC 17021-1 and understand the requirements of ISO 37301 and the relationship between
those requirements, as well as the knowledge described in 7.2.1.2 to 7.2.1.5.
The competence requirements specified in 7.2.1.2 to 7.2.1.5 shall apply within the scope of the CMS to be
audited.
It is not necessary for each member of the audit team to have the same competence; however, the collective
competence of the audit team shall be sufficient to achieve the audit objectives.
7.2.1.2 Context of the organization
The audit team shall have knowledge of the context in which the organization operates. The audit team shall
be able to understand the business activities and processes of the organization in so far as they relate to the
compliance obligations and compliance risks arising from those activities and processes.
The audit team shall have the knowledge and skills necessary to conduct research related to the organization
to identify and understand applicable compliance obligations and risks.
7.2.1.3 Laws, regulations and other requirements
The audit team shall have knowledge and understanding concerning different legal systems, laws and
regulations. The audit team shall have the knowledge and skills to understand different types of legal texts
and to understand their relevance for the compliance obligations of the organization.
The audit team shall have knowledge about the legal framework in which the organization operates and shall
be able to understand the applicable compliance obligations and compliance risks within the scope of the CMS
to be audited.
The audit team shall have knowledge about other applicable requirements to be able to understand their
relevance for the compliance obligations and risks which arise from these other requirements within the scope
of the CMS to be audited.
NOTE Other applicable requirements can be, for example, directives, licence agreements, voluntary codes,
organizational and industry standards, contractual relationships, codes of practice and agreements with community
groups or non-governmental organizations.
7.2.1.4 Compliance risk assessment and controls
The audit team shall have knowledge about how compliance risk assessments as described in ISO 37301:2021,
4.6 are conducted.
ISO/DISFDIS 37304:2026(en)
The audit team shall have knowledge and understanding of methods for assessing and treating compliance
risks.
The audit team shall have knowledge and understanding in evaluating compliance controls.
7.2.1.5 Compliance management systems (CMS)
The audit team shall have knowledge and understanding of how a CMS is established and implemented in
accordance with ISO 37301.
The audit team shall have specific CMS knowledge about at least the following:
a) the drivers and indicators of compliance culture;
Formatted: Numbered + Level: 1 + Numbering Style: a,
b, c, … + Start at: 1 + Alignment: Left + Aligned at: 0
b) leadership that contributes to an effective CMS;
cm + Indent at: 0 cm
Formatted: Numbered + Level: 1 + Numbering Style: a,
c) the role and responsibility of the compliance function;
b, c, … + Start at: 2 + Alignment: Left + Aligned at: 0
cm + Indent at: 0 cm
d) compliance training;
Formatted: Numbered + Level: 1 + Numbering Style: a,
b, c, … + Start at: 3 + Alignment: Left + Aligned at: 0
e) processes of monitoring, measuring, and reporting compliance performance;
cm + Indent at: 0 cm
f) systems for raising concerns and processes to address them; Formatted: Numbered + Level: 1 + Numbering Style: a,
b, c, … + Start at: 4 + Alignment: Left + Aligned at: 0
g) investigation of instances of non-compliance. cm + Indent at: 0 cm
Formatted: Numbered + Level: 1 + Numbering Style: a,
7.2.2 Competence requirements for other personnel
b, c, … + Start at: 5 + Alignment: Left + Aligned at: 0
cm + Indent at: 0 cm
7.2.2.1 General
Formatted: Numbered + Level: 1 + Numbering Style: a,
b, c, … + Start at: 6 + Alignment: Left + Aligned at: 0
Personnel conducting the application review to determine the audit team competence required, to select the
cm + Indent at: 0 cm
audit team members and to determine the audit time, those. Those reviewing audit reports and those making
certification decisions are referred to as other personnel.
Formatted: Numbered + Level: 1 + Numbering Style: a,
b, c, … + Start at: 7 + Alignment: Left + Aligned at: 0
Other personnel shall have the generic competence described in ISO/IEC 17021-1, shall understand the
cm + Indent at: 0 cm
requirements of ISO 37301 and the relationship between those requirements, and shall have the CMS
knowledge requirements described in 7.2.2.2.
7.2.2.2 Context of the organization
Other personnel shall have knowledge of the context in which the organization operates. Other personnel shall
be
...